Heroes, your curated look at the current cybersecurity landscape for June 10, 2026.
Critical Threats
Microsoft's June 2026 Patch Tuesday is massive, resolving 206 vulnerabilities, including three critical zero-days and severe 9.8 CVSS flaws affecting the kernel, network, and HTTP.sys components. This broad attack surface requires immediate triage to prevent widespread exploitation.
Business Impact
Unpatched systems expose the organization to immediate ransomware and data theft risks, potentially causing massive operational downtime, regulatory fines, and loss of customer trust.
Recommended Action
Ask your IT team: Have we prioritized and deployed the June 2026 Microsoft patches, specifically targeting the three zero-days and internet-facing systems?
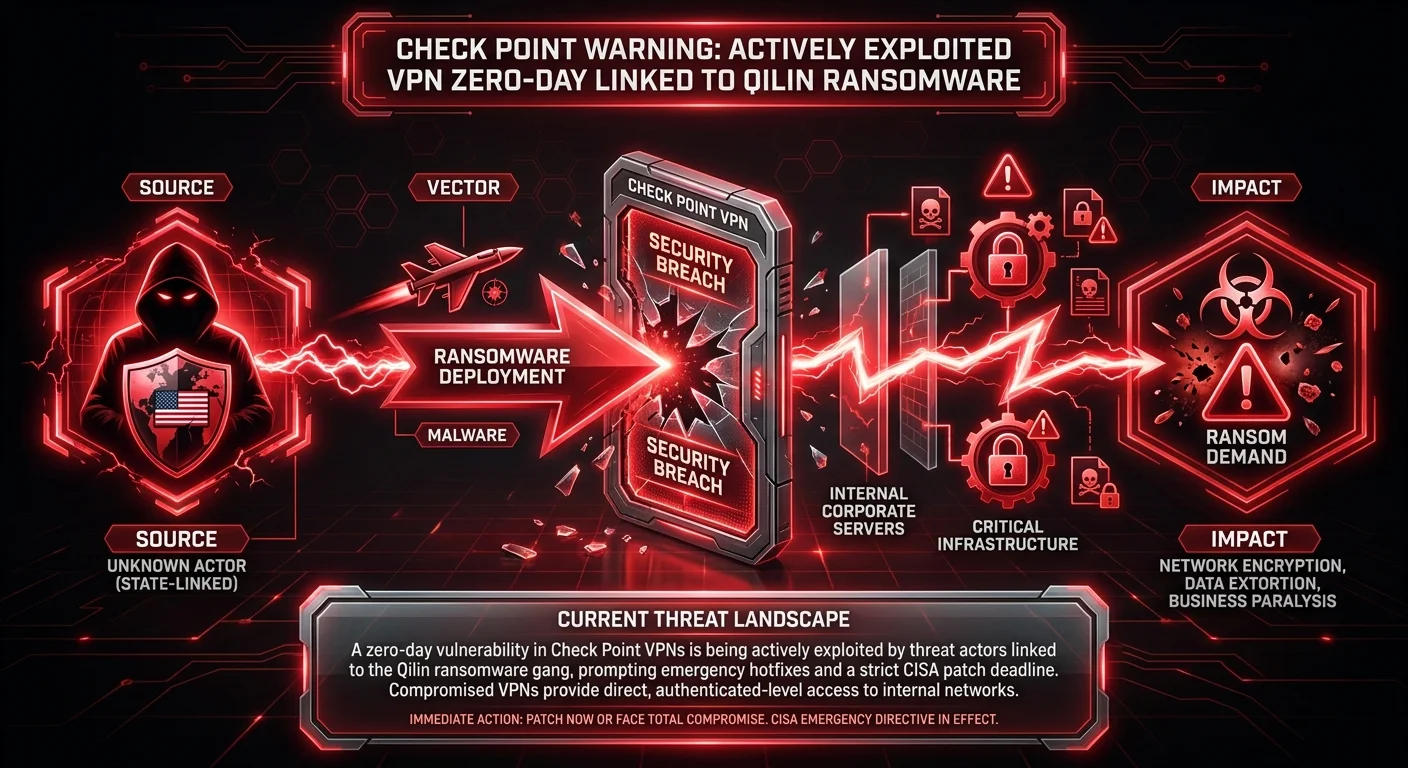
A zero-day vulnerability in Check Point VPNs is being actively exploited by threat actors linked to the Qilin ransomware gang, prompting emergency hotfixes and a strict CISA patch deadline. Compromised VPNs provide direct, authenticated-level access to internal networks.
Business Impact
Active exploitation by ransomware gangs means an immediate risk of network encryption, data extortion, and total business paralysis if perimeter VPNs are not secured immediately.
Recommended Action
Ask your IT team: Have we applied the emergency hotfixes for our Check Point VPNs to meet the CISA patch deadline and checked for signs of Qilin ransomware activity?
Unknown threat actors have actively exploited a vulnerability in ServiceNow to gain unauthorized access to susceptible customer instances. ServiceNow applied a security update to hosted instances on June 5, but self-hosted customers must patch manually.
Business Impact
Unauthorized access to IT service management platforms can lead to the theft of sensitive corporate data, employee records, and IT infrastructure maps, triggering severe compliance penalties and reputational damage.
Recommended Action
Ask your IT team: Have we verified that our ServiceNow instances received the June 5 security update, and have we audited access logs for unauthorized entry?
High Severity
Major industrial control system (ICS) vendors, including Siemens, Schneider Electric, and Phoenix Contact, have released their Patch Tuesday updates to address multiple vulnerabilities affecting operational technology environments.
Business Impact
Vulnerabilities in industrial control systems can lead to physical equipment damage, production halts, and severe safety risks for manufacturing and critical infrastructure operations.
Recommended Action
Ask your OT/IT teams: Have we reviewed and scheduled the latest ICS patches from Siemens, Schneider, and Phoenix Contact during our next maintenance window?
A threat actor known as Chaotic Eclipse has released a new Windows Defender evasion tool dubbed "RoguePlanet" on GitHub. This release coincides with Patch Tuesday, potentially complicating defensive efforts.
Business Impact
Evasion of endpoint detection systems allows threat actors to operate undetected, increasing the risk of prolonged data exfiltration, ransomware deployment, and costly incident response engagements.
Recommended Action
Ask your IT team: Are our endpoint security tools and SOC teams aware of the new RoguePlanet evasion techniques, and have we updated our detection logic?
Other Noteworthy
Executive Briefing
Anthropic has launched Claude Fable 5, a Mythos-class AI featuring enhanced cybersecurity guardrails. Project Glasswing partners are receiving early access to explore defensive AI applications, highlighting the industry's shift toward AI-augmented SOC operations.
Zscaler has updated its Zero Trust Exchange platform to secure how artificial intelligence agents connect and access data. As organizations adopt autonomous AI agents, traditional human-centric identity frameworks are proving insufficient.
Security leaders in marketing and advertising face unique challenges managing client relationships, audience data, and compliance obligations. The article highlights how CISOs in this sector are scaling brand trust alongside complex technology workflows.
Public sector cybersecurity teams are navigating strict budgetary constraints while facing rising global cyber attacks. Strategic SIEM optimization is critical for government engineers to maintain visibility without exceeding budget limits.
Vendor Spotlight
AppOmni (Specialized Vendor)
Specialization: SaaS Security Posture Management (SSPM)
Why AppOmni Today: AppOmni is highly relevant to today's threat landscape, specifically regarding the active exploitation of the ServiceNow flaw that grants unauthorized access to customer instances. As a leader in SaaS Security Posture Management (SSPM), AppOmni provides deep visibility, permission mapping, and configuration monitoring for enterprise SaaS platforms like ServiceNow to detect misconfigurations and prevent unauthorized access.
Key Capability: Continuous configuration monitoring and threat detection for enterprise SaaS applications to prevent unauthorized access and data leakage.
Recommended Actions:
1. Navigate to AppOmni Console → Policies → Posture
2. Navigate to AppOmni Console → SaaS Identity → Users
3. Navigate to AppOmni Console → Threat Detection → Rules
Verification Steps:
- Review the 'Insights → Posture' dashboard, filtering by 'ServiceNow' and 'High Severity' alerts related to ACLs or public access.
- Navigate to 'Settings → SaaS Services → ServiceNow' and verify the Event Log ingestion status.