Monday, March 23, 2026

MikeGPT CyberSecurity

“Playbook for the Secure Enterprise”

MikeGPT Daily Threat Rundown

Heroes, your curated look at the current cybersecurity landscape for March 23, 2026.

Critical Threats
U.S. CISA adds Apple, Laravel Livewire and Craft CMS flaws to its Known Exploited Vulnerabilities catalog

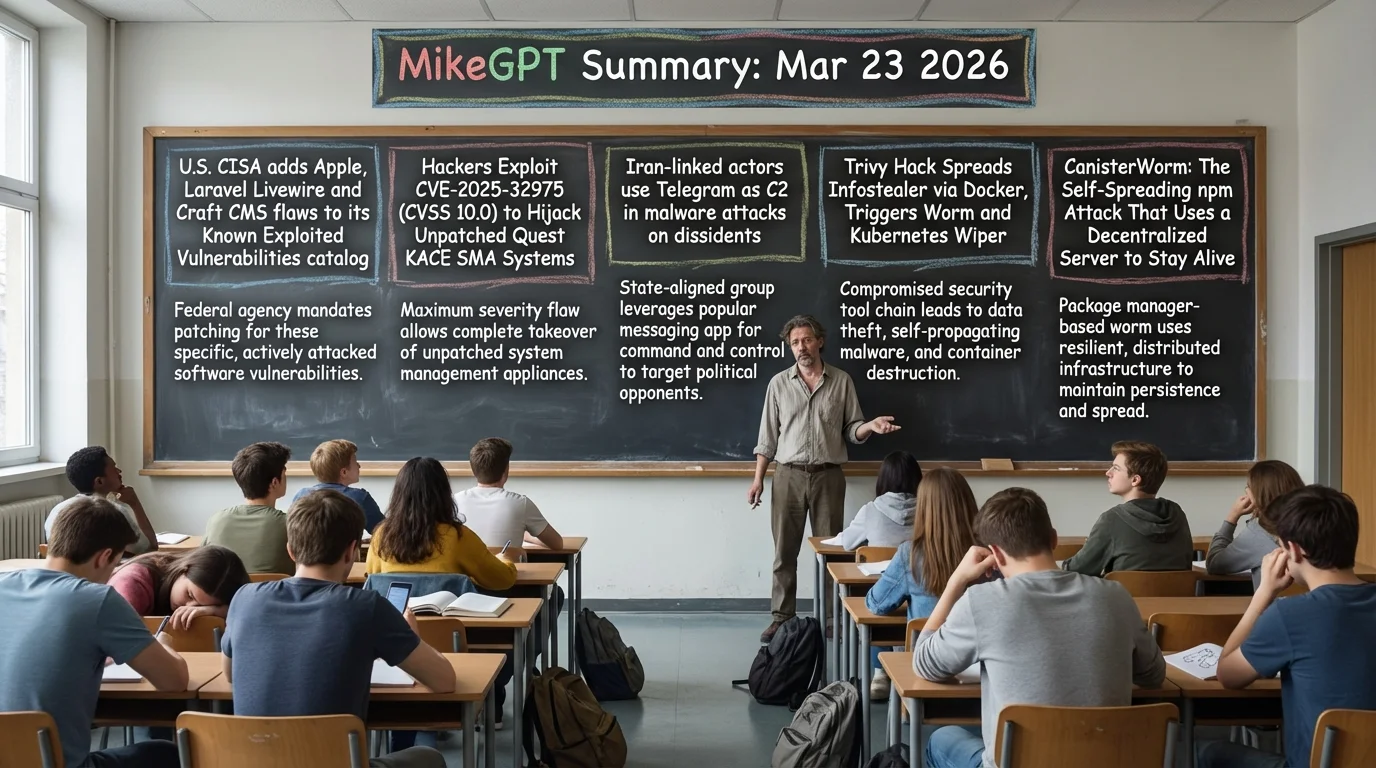
    The Cybersecurity and Infrastructure Security Agency (CISA) has added multiple actively exploited vulnerabilities affecting Apple, Laravel Livewire, and Craft CMS to its KEV catalog. These flaws are currently being leveraged by threat actors in the wild to compromise enterprise environments.

    Business Impact

    Unpatched systems face an immediate risk of compromise by active threat actors, potentially leading to data breaches, regulatory penalties, and loss of customer trust.

    Recommended Action

    Ask your IT team: Have we audited our environment for Apple, Laravel, and Craft CMS instances and applied the CISA-mandated patches?
Threat actors are actively exploiting a maximum-severity security flaw (CVSS 10.0) in Quest KACE Systems Management Appliances (SMA) to gain complete control over unpatched systems. Arctic Wolf has observed malicious activity, including the deployment of post-exploitation tools, originating from these compromised appliances since early March.

Business Impact

Complete system takeover allows attackers to deploy ransomware, steal sensitive corporate data, and move laterally across the network, resulting in massive operational downtime, severe financial losses, and mandatory breach disclosures.

Recommended Action

Ask your IT team: Are our Quest KACE SMA systems updated to the latest patched version, and have we scanned our environment for indicators of compromise?

CVE-2025-32975 General Enterprise The Hacker News ↗
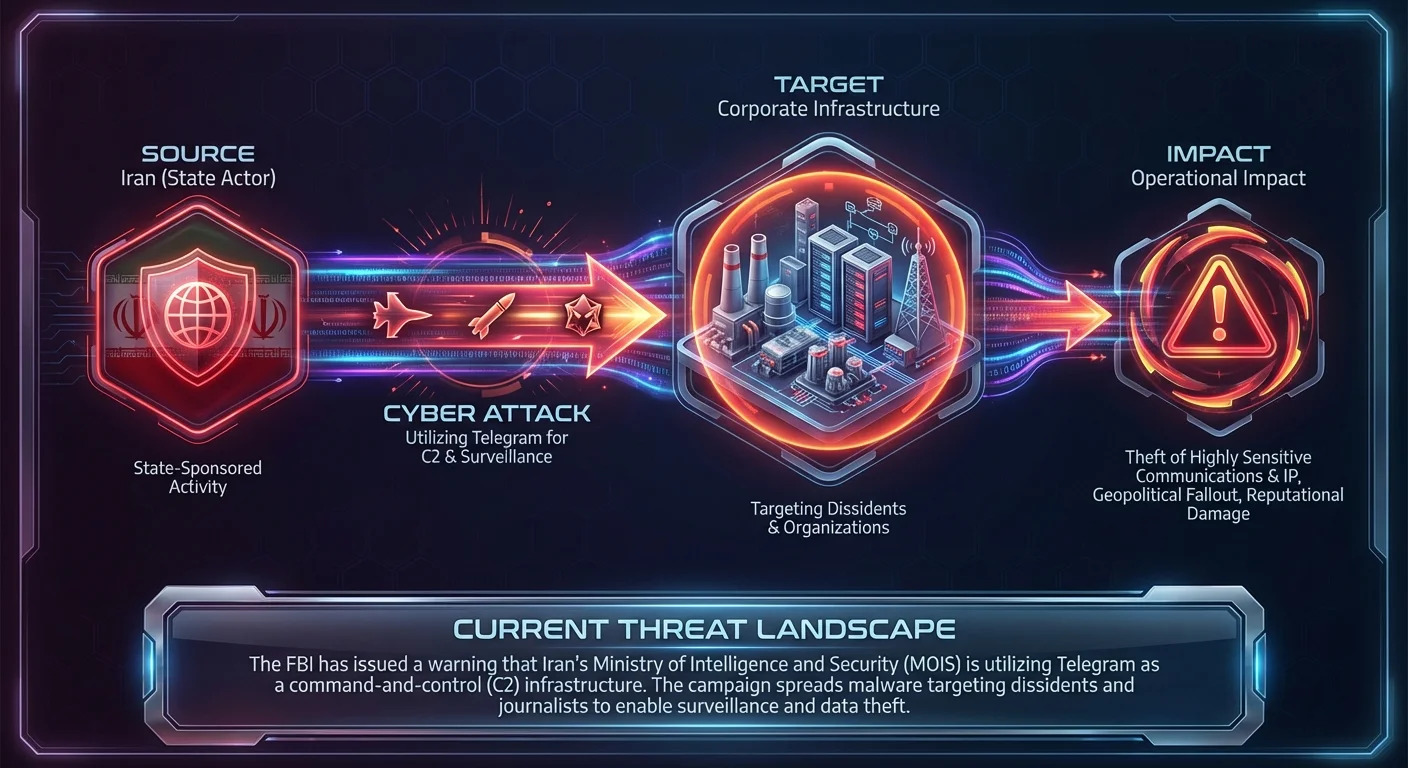
Iran-linked actors use Telegram as C2 in malware attacks on dissidents

    The FBI has issued a warning that Iran's Ministry of Intelligence and Security (MOIS) is utilizing Telegram as a command-and-control (C2) infrastructure. The campaign spreads malware targeting dissidents and journalists to enable surveillance and data theft.

    Business Impact

    State-sponsored espionage can result in the theft of highly sensitive communications and intellectual property, causing severe geopolitical fallout and reputational damage for targeted organizations.

    Recommended Action

    Ask your security team: Do our network controls block unauthorized Telegram API traffic from corporate devices to prevent C2 communication?

    General Enterprise Security Affairs ↗

High Severity

Trivy Hack Spreads Infostealer via Docker, Triggers Worm and Kubernetes Wiper

    Malicious artifacts are being distributed via Docker Hub following a supply chain attack on the Trivy vulnerability scanner. The compromised versions (0.69.4, 0.69.5) are spreading infostealers, worms, and Kubernetes wipers across developer environments.

    Business Impact

    Compromised developer environments can lead to the destruction of cloud infrastructure and theft of proprietary source code, causing catastrophic operational halts and loss of competitive advantage.

    Recommended Action

    Ask your DevOps team: Have we audited our container registries to ensure we are not pulling Trivy versions 0.69.4 or 0.69.5?

    General Enterprise The Hacker News ↗

Aikido Security detected a self-spreading npm worm dubbed CanisterWorm infecting dozens of packages across multiple organizations. The attack uses unauthorized patch updates containing hidden malicious code and relies on a decentralized server to maintain persistence.

Business Impact

Software supply chain infections can compromise proprietary applications shipped to clients, leading to downstream customer breaches, massive recall efforts, and significant legal liabilities.

Recommended Action

Ask your engineering team: Have we scanned our npm dependencies for unauthorized patch updates or indicators of the CanisterWorm infection?

General Enterprise Mend.io ↗

Executive Briefing

MY TAKE: As RSAC 2026 opens, AI has bifurcated cybersecurity into two wars

As the RSA Conference 2026 opens in San Francisco, industry leaders are highlighting how artificial intelligence has fundamentally split cybersecurity into two distinct battlegrounds. Organizations are facing acute pressure to modernize their defensive postures as AI accelerates both offensive capabilities and defensive requirements.

Last Watchdog · 10:35 AM ·
Booz Allen Rolls Out Vellox, a Five-Product AI Cyber Suite Built on Adversary Tradecraft

Booz Allen Hamilton introduced Vellox, a new AI-native suite designed to counter adversary tradecraft at machine speed. The launch emphasizes a growing industry consensus that traditional, human-speed defense mechanisms are no longer sufficient against modern, automated threat actors.

Security Boulevard · 1:33 AM ·
AI Security Startup Xbow Valued at More Than $1B

Reflecting the massive market shift toward automated defense and offensive security testing, AI security startup Xbow has reached a valuation exceeding $1 billion, underscoring investor confidence in AI-driven security solutions.

Hacker News · 6:17 PM ·

Vendor Spotlight

Arctic Wolf

Specialization: Managed Detection & Response (MDR)

Why Arctic Wolf Today: Arctic Wolf's threat intelligence team directly discovered and observed the active exploitation of the maximum-severity CVE-2025-32975 flaw in Quest KACE SMA systems mentioned in today's briefing. Highlighting them provides readers with the primary source of this critical threat intel, while their MDR platform is specifically designed to detect the post-exploitation malicious activity and lateral movement originating from such unpatched appliances.

Key Capability: 24/7 SOC monitoring and appliance exploitation detection

Recommended Actions:
1. Navigate to Arctic Wolf Unified Portal → Managed Risk → Vulnerabilities
2. Navigate to Arctic Wolf Unified Portal → Tickets → Create Ticket
3. Navigate to Arctic Wolf Unified Portal → Log Search

Verification Steps:
- Review the CST threat hunt ticket updates in the Unified Portal
- Rescan the KACE SMA appliances via the Managed Risk scanner and check the Asset Details page

Learn More About Arctic Wolf ↗

Detection & Response

Detection & Response Kit (4 items)

⚠️ Disclaimer: Test all detection logic in non-production environments before deployment.

1. Vendor Platform Configuration - Arctic Wolf

# Actionable Guidance for Arctic Wolf # Generated: 2026-03-23 11:00:45 # Step 1: Navigate to Arctic Wolf Unified Portal → Managed Risk → Vulnerabilities # Purpose: Identify any Quest KACE SMA appliances in your environment vulnerable to CVE-2025-32975 # Expected: A filtered list of internal or external assets running the vulnerable Quest KACE SMA software version, allowing you to prioritize immediate patching or isolation. # Step 2: Navigate to Arctic Wolf Unified Portal → Tickets → Create Ticket # Purpose: Engage your Concierge Security Team (CST) to initiate a targeted threat hunt for post-exploitation activity # Expected: A confirmed threat hunting ticket opened with the CST, specifically requesting them to leverage Arctic Wolf MDR to look for lateral movement, anomalous network traffic, or suspicious process execution originating from your KACE SMA IP addresses. # Step 3: Navigate to Arctic Wolf Unified Portal → Log Search # Purpose: Query network and endpoint logs for anomalous outbound connections or unauthorized authentication attempts originating from the KACE SMA appliance # Expected: Immediate visibility into any potential post-exploitation lateral movement, unusual administrative logins, or suspicious payload executions tied to the appliance. # Verification Steps: # - Review the CST threat hunt ticket updates in the Unified Portal # Expected: CST confirms no IoCs or lateral movement detected from KACE SMA appliances, or provides an immediate incident remediation plan if malicious activity is found # - Rescan the KACE SMA appliances via the Managed Risk scanner and check the Asset Details page # Expected: CVE-2025-32975 is marked as 'Resolved' and no longer appears under the active vulnerabilities for the Quest KACE assets

2. YARA Rule for Quest KACE SMA Post-Exploitation (CVE-2025-32975)

rule Quest_KACE_SMA_Exploitation_Artifacts { meta: description = "Detects post-exploitation artifacts related to CVE-2025-32975 in Quest KACE SMA" author = "Threat Rundown" date = "2026-03-24" reference = "https://thehackernews.com/2026/03/hackers-exploit-cve-2025-32975-cvss-100.html" severity = "critical" tlp = "white" strings: $s1 = "KPluginRunProcess" ascii wide nocase $s2 = "Mimikatz" ascii wide nocase $s3 = "216.126.225.156" ascii wide condition: any of ($s*) }

3. SIEM Query — Quest KACE SMA Exploitation Activity

index=security sourcetype="sysmon" OR sourcetype="WinEventLog:Security" (EventCode=1 OR EventCode=3) (Image="*\\KPluginRunProcess*" OR Image="*\\Mimikatz*" OR dest_ip="216.126.225.156") | eval risk_score=case( dest_ip=="216.126.225.156", 100, match(Image, "(?i)Mimikatz"), 100, match(Image, "(?i)KPluginRunProcess"), 75, 1==1, 25) | where risk_score >= 75 | table _time, host, user, Image, CommandLine, dest_ip, risk_score | sort -_time

4. PowerShell Script — Rapid Indicator Sweep

$computers = "localhost", "KACE-SMA-01", "MGMT-SRV-01" $maliciousIP = "216.126.225.156" $suspiciousProcesses = @("KPluginRunProcess", "mimikatz") foreach ($computer in $computers) { if (Test-Connection -ComputerName $computer -Count 1 -Quiet) { Write-Host "Checking $computer for CVE-2025-32975 indicators..." -ForegroundColor Cyan # Check for running malicious processes foreach ($proc in $suspiciousProcesses) { $found = Get-Process -ComputerName $computer -Name $proc -ErrorAction SilentlyContinue if ($found) { Write-Host "[!] CRITICAL: Suspicious process $proc found running on $computer!" -ForegroundColor Red } } # Check active network connections (Requires WinRM/Invoke-Command for remote) Invoke-Command -ComputerName $computer -ScriptBlock { $conns = Get-NetTCPConnection -RemoteAddress $using:maliciousIP -ErrorAction SilentlyContinue if ($conns) { Write-Host "[!] CRITICAL: Active connection to malicious IP $using:maliciousIP found!" -ForegroundColor Red } } -ErrorAction SilentlyContinue } else { Write-Host "$computer is offline or unreachable." -ForegroundColor Yellow } }

This rundown should provide a solid overview of the current threat landscape. Thank you to all our cyberheroes for your diligence and hard work. Stay vigilant!