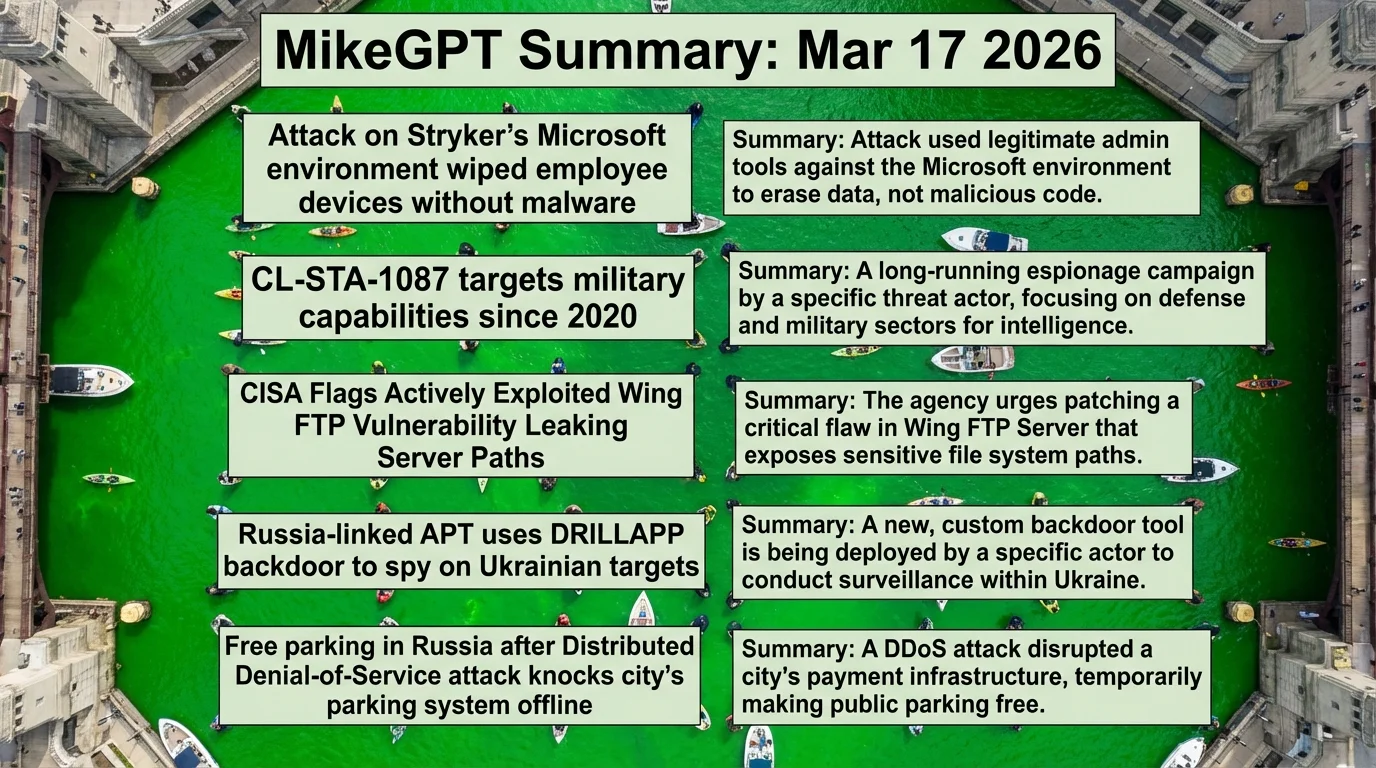
Heroes, your curated look at the current cybersecurity landscape for Mar 17, 2026.
Critical Threats
Attack on Stryker’s Microsoft environment wiped employee devices without malware
A cyberattack on medical technology giant Stryker targeted its internal Microsoft environment, wiping tens of thousands of employee devices without using traditional malware. Systems remain offline as the company responds to the incident.
Business Impact
If exploited, attackers could cause massive operational downtime and data destruction - expect severe revenue loss, delayed medical device manufacturing, and significant reputational damage.
Recommended Action
Ask your IT team: are we monitoring for living-off-the-land (LotL) techniques in our Microsoft environment? Do we have offline backups for critical employee devices?
CL-STA-1087 targets military capabilities since 2020
A suspected China-linked espionage campaign tracked as CL-STA-1087 has been targeting Southeast Asian militaries since 2020 using custom malware like AppleChris and MemFun.
Business Impact
If targeted, organizations could suffer severe intellectual property theft and espionage - expect compromised strategic communications, loss of competitive advantage, and national security implications.
Recommended Action
Ask your IT team: are our endpoint detection systems configured to detect known indicators for AppleChris and MemFun malware?
CISA Flags Actively Exploited Wing FTP Vulnerability Leaking Server Paths
CISA has added a medium-severity information disclosure flaw in Wing FTP to its Known Exploited Vulnerabilities catalog due to active exploitation.
Business Impact
If exploited, attackers could map internal server paths and infrastructure - expect accelerated secondary attacks, potential data breaches, and regulatory scrutiny.
Recommended Action
Ask your IT team: do we use Wing FTP in our environment? Have we applied the latest vendor patches to address the KEV-listed vulnerability?
High Severity
Russia-linked APT uses DRILLAPP backdoor to spy on Ukrainian targets
A new campaign by Russia-linked threat actors targets Ukrainian organizations with the DRILLAPP backdoor, abusing Microsoft Edge debugging features to evade detection.
Business Impact
If exploited, attackers could establish persistent stealth access - expect long-term espionage, intellectual property theft, and severe operational disruption.
Recommended Action
Ask your IT team: are we monitoring for unauthorized use of Microsoft Edge debugging flags in our environment?
Free parking in Russia after Distributed Denial-of-Service attack knocks city’s parking system offline
Hackers successfully knocked the city of Perm's payment system offline via a DDoS attack, resulting in free parking for drivers.
Business Impact
If targeted by similar DDoS attacks, municipal or enterprise payment systems could fail - expect direct revenue loss, customer frustration, and emergency incident response costs.
Recommended Action
Ask your IT team: do we have robust DDoS mitigation controls in place for our public-facing payment gateways?
Open, Closed and Broken: Prompt Fuzzing Finds LLMs Still Fragile Across Open and Closed Models
Unit 42 researchers demonstrated that LLM guardrails remain fragile, using genetic algorithm-inspired prompt fuzzing to discover scalable evasion methods.
BSidesCache 2025 – Hackers Don’t Break In. They Log In.
A presentation from BSidesCache emphasizes the growing trend of identity-based attacks, highlighting that threat actors increasingly abuse legitimate credentials rather than exploiting technical flaws.
How smart should your secrets rotation technology be
Industry guidance highlights the critical importance of securing Non-Human Identities (NHIs) and implementing intelligent secrets rotation to prevent inadvertent data exposure.
UK security adviser attended US-Iran talks and judged deal was within reach
Reports indicate a UK security adviser attended US-Iran talks, assessing that a geopolitical deal was within reach, which could have downstream impacts on state-sponsored cyber activity.
Other Noteworthy
Open, Closed and Broken: Prompt Fuzzing Finds LLMs Still Fragile Across Open and Closed Models
Unit 42 researchers demonstrated that LLM guardrails remain fragile, using genetic algorithm-inspired prompt fuzzing to discover scalable evasion methods.
BSidesCache 2025 – Hackers Don’t Break In. They Log In.
A presentation from BSidesCache emphasizes the growing trend of identity-based attacks, highlighting that threat actors increasingly abuse legitimate credentials rather than exploiting technical flaws.
How smart should your secrets rotation technology be
Industry guidance highlights the critical importance of securing Non-Human Identities (NHIs) and implementing intelligent secrets rotation to prevent inadvertent data exposure.
UK security adviser attended US-Iran talks and judged deal was within reach
Reports indicate a UK security adviser attended US-Iran talks, assessing that a geopolitical deal was within reach, which could have downstream impacts on state-sponsored cyber activity.
Executive Briefing
Security leaders are advised to implement strict governance layers—including policy-driven guardrails, human-approval gates, and blast-radius limits—before allowing agentic AI to execute automated actions in the SOC.
Vendor Spotlight
Specialization: Managed Detection & Response (MDR)
Why Red Canary Today: The catastrophic attack on Stryker wiped tens of thousands of devices through its Microsoft environment without using traditional malware, while the CL-STA-1087 APT continues to target organizations using custom tooling. Red Canary's MDR platform excels at detecting these exact types of living-off-the-land (LotL) techniques and identity-based abuses by analyzing deep behavioral telemetry across endpoints and Microsoft environments.
Key Capability: Behavioral analytics for detecting non-malware and living-off-the-land (LotL) attacks
Recommended Actions:
1. Navigate to Red Canary Console → Integrations → Cloud & SaaS Providers → Microsoft 365
2. Navigate to Red Canary Console → Automations → Playbooks → Create Playbook
3. Navigate to Red Canary Console → Threats → Add Filter
Verification Steps:
- Review the 'Endpoints' dashboard to verify EDR sensor health and ensure devices are not being systematically taken offline or wiped.
- Execute a benign test detection to trigger the newly created Isolation Playbook and review the Red Canary 'Action Logs'.
Detection & Response
⚠️ Disclaimer: Test all detection logic in non-production environments before deployment.
1. Vendor Platform Configuration - Red Canary
2. YARA Rule for CL-STA-1087 & Stryker Attack Indicators
3. SIEM Query — Edge Debugging Abuse & Malware Execution
4. PowerShell Script — Edge Debugging & Artifact Discovery
This rundown should provide a solid overview of the current threat landscape. Thank you to all our cyberheroes for your diligence and hard work. Stay vigilant!