Heroes, your curated look at the current cybersecurity landscape for Mar 11, 2026.
Critical Threats
Microsoft released patches for 84 security vulnerabilities, including two publicly disclosed zero-days and eight flaws rated as Critical. These updates address significant risks across various Windows and Microsoft software components.
Business Impact
Unpatched systems expose the organization to immediate exploitation, potentially leading to unauthorized access, data theft, and subsequent regulatory fines or operational downtime.
Recommended Action
Ask your IT team: Have we prioritized and deployed the March 2026 Microsoft security updates across all endpoints and servers, particularly for the known zero-days?
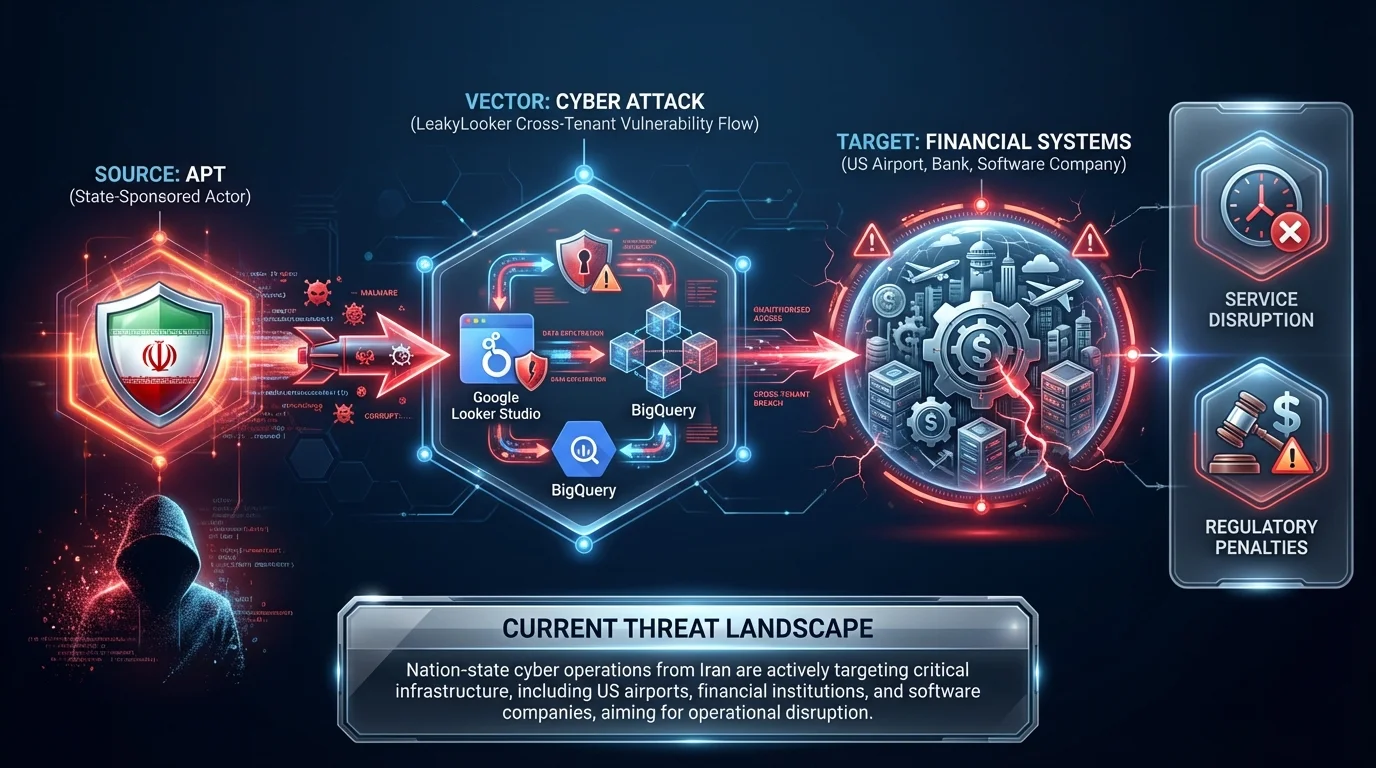
Nation-state cyber operations from Iran are actively targeting critical infrastructure, including US airports, financial institutions, and software companies, aiming for operational disruption.
Business Impact
Successful intrusions by nation-state actors can cause catastrophic operational paralysis, massive financial losses, and severe regulatory scrutiny for critical infrastructure operators.
Recommended Action
Ask your threat intelligence team: Have we updated our defenses with the latest IOCs related to Iranian APT groups targeting our sector?
High Severity
A novel evasion technique called "Zombie ZIP" allows attackers to conceal malicious payloads within compressed files, successfully bypassing antivirus and Endpoint Detection and Response (EDR) solutions.
Business Impact
If malware bypasses endpoint defenses, it can silently establish persistence, leading to undetected data theft and costly incident response engagements.
Recommended Action
Ask your security operations center: Is our EDR vendor aware of the Zombie ZIP technique, and do we have behavioral rules to catch post-extraction anomalies?
An insider threat incident occurred where an employee reportedly stole sensitive Social Security data by exfiltrating it onto a physical thumb drive.
Business Impact
Insider data theft directly results in privacy violations, mandatory breach notifications, loss of customer trust, and potential class-action lawsuits.
Recommended Action
Ask your IT team: Do we have strict USB mass storage restrictions and Data Loss Prevention (DLP) policies actively enforced on all employee endpoints?
Executive Briefing
The latest Threat Horizons report highlights emerging cloud security trends, focusing on identity hijacking, misconfigurations, and the evolving tactics of cloud-focused threat actors targeting enterprise environments.
Vendor Spotlight
Why Cloudflare Today: Cloudflare's edge security and Zero Trust architecture directly mitigate today's active exploitation of perimeter firewalls, outbound data exfiltration from compromised CI/CD pipelines, and emerging web application vulnerabilities.
FortiGate Devices Exploited to Breach Networks and Steal Service Account Credentials
- Threat — Active exploitation of FortiGate Next-Generation Firewall (NGFW) appliances and weak credentials to breach networks and steal service accounts.
- Cloudflare Product(s) — Zero Trust (Cloudflare Access), WAF (Web Application Firewall)
- Configuration Guidance — To protect exposed administrative interfaces from exploitation, remove them from the public internet and place them behind an identity-aware proxy:
Dashboard → Zero Trust → Access → Applications → Add an application (Configure policies to require MFA and restrict access to specific user groups).
For interfaces that must remain public, deploy virtual patching:
Dashboard → Security → WAF → Managed Rules → Enable the "Cloudflare Managed Ruleset" to block known exploit payloads. - Coverage Assessment — Strong
- Integration Note — Microsoft Entra ID or Okta to provide the underlying identity verification, MFA enforcement, and conditional access policies for Cloudflare Access.
Malicious Rust Crates Stealing Developer Secrets (.env files)
- Threat — Five malicious Rust crates (chrono_anchor, dnp3times, etc.) exploiting CI/CD pipelines to steal and transmit
.envfile data containing developer secrets. - Cloudflare Product(s) — Cloudflare Gateway, Data Loss Prevention (DLP), Secrets Store
- Configuration Guidance — Prevent outbound exfiltration of
.envdata from CI/CD runners by routing their egress traffic through Cloudflare Gateway with DLP inspection:
Dashboard → Zero Trust → Gateway → Policies → HTTP → Create rule:
Selector: DLP ProfileOperator: inValue: Credentials and Secrets→ Action:Block.
Note: Migrate hardcoded.envsecrets to Cloudflare Secrets Store for secure management. - Coverage Assessment — Moderate (Requires CI/CD egress traffic to be actively routed through the Gateway proxy/agent).
- Integration Note — Splunk (via Logpush) to ingest Gateway HTTP logs and trigger SOAR playbooks when outbound credential exfiltration is blocked.
Adobe Commerce Vulnerabilities (Adobe Patch Tuesday)
- Threat — 80 vulnerabilities patched across Adobe products, specifically targeting web-facing Adobe Commerce (Magento) applications.
- Cloudflare Product(s) — WAF (Web Application Firewall)
- Configuration Guidance — Deploy virtual patching to protect Adobe Commerce endpoints before origin servers can be manually updated:
Dashboard → Security → WAF → Managed Rules → Select "Cloudflare Managed Ruleset" → Search for "Adobe" or "Magento" tags and ensure the action is set toBlock. - Coverage Assessment — Strong