[copy]
{
"type": "bundle",
"id": "bundle--8713f5aa-1eaf-434e-9d9e-f7dac80ce90b",
"objects": [
{
"type": "marking-definition",
"spec_version": "2.1",
"id": "marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487",
"created": "2022-10-01T00:00:00.000Z",
"definition_type": "tlp:2.0",
"name": "TLP:CLEAR",
"definition": {
"tlp": "clear"
}
},
{
"type": "identity",
"spec_version": "2.1",
"id": "identity--caf1dc18-12ad-4b11-a8ab-af65ebd7da1d",
"created": "2026-03-03T13:20:18.123Z",
"modified": "2026-03-03T13:20:18.123Z",
"name": "MikeGPT Intelligence Platform",
"description": "AI-powered threat intelligence collection and analysis platform providing automated cybersecurity intelligence feeds",
"identity_class": "organization",
"sectors": [
"technology",
"defense"
],
"contact_information": "Website: https://mikegptai.com | Email: intel@mikegptai.com",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"type": "report",
"spec_version": "2.1",
"id": "report--2b90f28e-58d4-4a11-aede-e8451af433e2",
"created": "2026-03-03T13:20:18.123Z",
"modified": "2026-03-03T13:20:18.123Z",
"name": "Threat Intelligence Report - 2026-03-03",
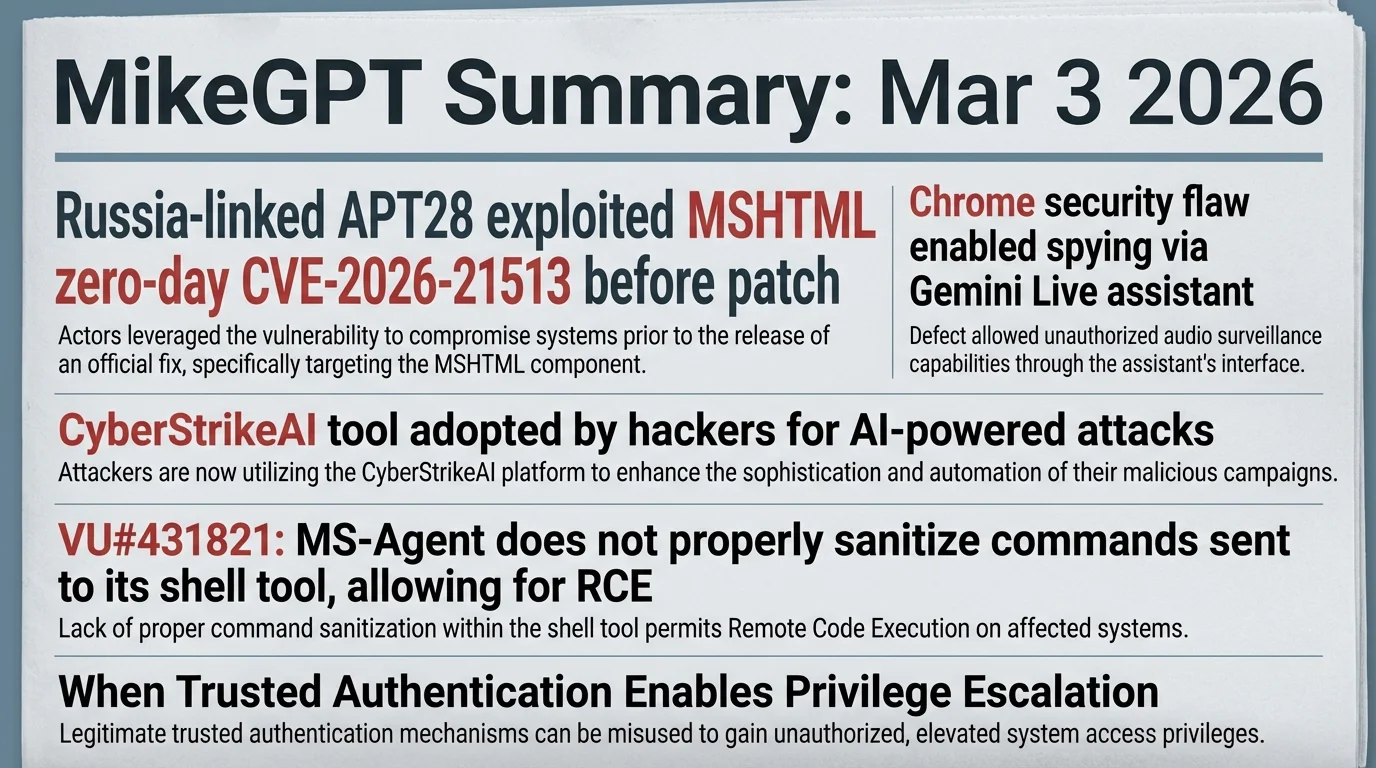
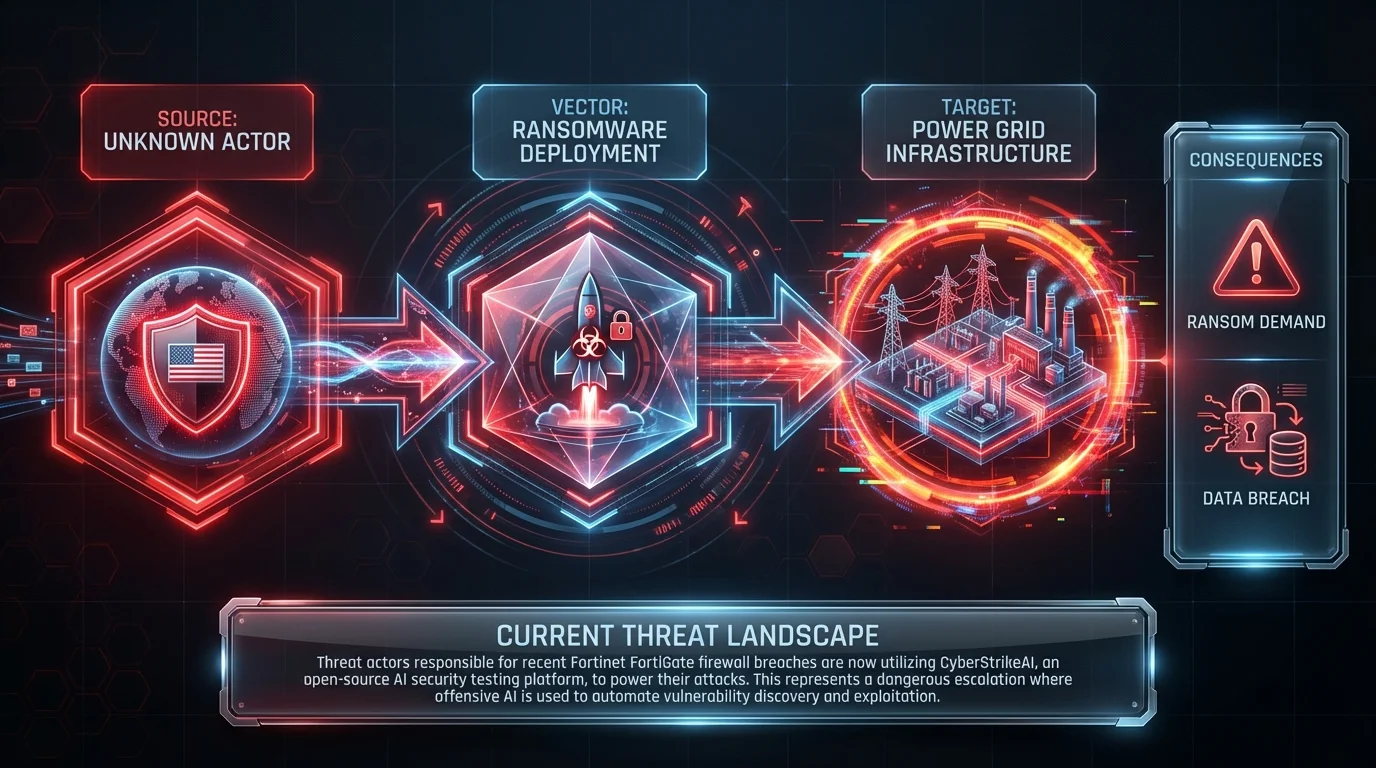
"description": "Threat Intelligence Report - 2026-03-03\n\nThis report consolidates actionable cybersecurity intelligence from 76 sources, processed through automated threat analysis and relationship extraction.\n\nKEY FINDINGS:\n• Chrome security flaw enabled spying via Gemini Live assistant (Score: 100)\n• Talos on the developing situation in the Middle East (Score: 100)\n• Threat Brief: March 2026 Escalation of Cyber Risk Related to Iran (Score: 100)\n• CyberStrikeAI tool adopted by hackers for AI-powered attacks (Score: 100)\n• Fake Google Security site uses PWA app to steal credentials, MFA codes (Score: 100)\n\nEXTRACTED ENTITIES:\n• 19 Attack Pattern(s)\n• 50 Domain Name(s)\n• 50 Indicator(s)\n• 1 Marking Definition(s)\n• 50 Relationship(s)\n• 1 Threat Actor(s)\n• 2 Vulnerability(s)\n\nCONFIDENCE ASSESSMENT:\nVariable confidence scoring applied based on entity type and intelligence source reliability. Confidence ranges from 30-95% reflecting professional intelligence assessment practices.\n\nGENERATION METADATA:\n- Processing Time: Automated\n- Validation: Three-LLM consensus committee\n- Standards Compliance: STIX 2.1\n",
"published": "2026-03-03T13:20:18.123Z",
"object_refs": [
"identity--caf1dc18-12ad-4b11-a8ab-af65ebd7da1d",
"identity--69aa5d6f-85af-4de1-8aae-4064ba1566c3",
"identity--6f0bf2cd-7561-4393-8250-44c39f8a12f8",
"identity--fd1e3790-7e3a-48a3-8684-16f17330c96f",
"identity--d3da56c0-c933-4ac5-94f4-a5aa68ae5a77",
"identity--e7aaa346-3c47-410b-b7ac-2f53a69389c5",
"identity--68d5e0b1-4a32-4b0e-82f8-cf3521e297d9",
"identity--798dea09-c600-4af2-b078-819fa8479138",
"identity--97c7100b-5163-4e33-a926-ff1bf2062824",
"identity--5644c017-50f4-4316-9112-85831636b4c9",
"identity--a88478d8-481d-4fe4-80d1-5b1952ca2bbf",
"identity--34563d1b-a2e9-44ab-a65f-fb43a343ee32",
"identity--ef3514f5-090e-4090-8568-36680f106989",
"identity--4de38111-9093-4cb0-ae1d-8512f5ee7773",
"identity--39bc2030-ded5-40b5-be7a-6c2d627e2378",
"identity--c877be6e-5a87-41d2-b67e-fc0c6a8c863a",
"identity--f7423a25-c230-4896-ac95-2374a11bb1e0",
"identity--4fcb1491-74e5-4b75-8f63-5498c2b5f714",
"identity--f3bdd2a6-9aa9-4e4a-8593-165380c7ffd0",
"identity--6d7560b4-b89e-4459-b56b-c43ebd64a687",
"identity--083217f4-2992-4a6c-be9f-11a0e6716025",
"identity--d48d0179-a8bc-4c9e-89ef-4347fcbce1fa",
"identity--8dd81c81-6fef-45ca-b1e1-160489fc3f14",
"identity--98f20e05-ff41-460d-88f1-77efc295dfe2",
"identity--700e8e95-d6a0-4451-ae5a-5dc670c96905",
"identity--e579f0b6-29fc-4f87-be26-0870951a61da",
"identity--421dd0c0-c7eb-4edf-9cc1-bdfd1cbe9d15",
"identity--f32388a2-ff73-427d-8139-65139b46fda1",
"identity--d6fbbbd5-d4a2-4517-87ee-699f986f5720",
"identity--161fc746-cd49-4615-ab48-81a93a1b16b4",
"identity--f9f67fe7-735c-4107-8f6e-5dc3164bc5ce",
"vulnerability--3d1131b8-f17e-4e78-b180-e044e863e774",
"vulnerability--628167a8-ec55-45db-a347-8df2801619bb",
"identity--67504360-5ac2-467e-a28b-a560b4f91de9",
"threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"attack-pattern--280ebd89-59bc-4ae2-a9db-1c01a56e50dc",
"attack-pattern--e5974f70-5745-450a-908a-6483ad9c4678",
"attack-pattern--e8d516a9-a107-4c4b-806f-bc9c612eef18",
"attack-pattern--2da268b5-7100-4dbc-b23b-d5deafdf268c",
"attack-pattern--baad7d00-8591-4c49-8f48-fabb6a35df65",
"attack-pattern--c627c29c-1385-4d76-9046-9c2db86dab11",
"attack-pattern--f33f5834-6a9a-4727-88a5-9d35eeba1cff",
"attack-pattern--2d26e3d0-4bbf-44c3-aa9e-5aeab4937638",
"attack-pattern--13fc9cbe-9444-4eba-872b-a44565ae3ab7",
"attack-pattern--775a5581-fd79-4cfc-a505-6d409b3bbfba",
"attack-pattern--a45b8295-9056-4ed5-b811-6e7d2a71483e",
"attack-pattern--d2a77ce3-d278-4f77-97f0-227b744a33d3",
"attack-pattern--a6ff86fe-f269-42e5-9428-ab17d04e30e2",
"attack-pattern--27b36b6d-ae90-4767-b07a-563ecef589ea",
"attack-pattern--ed3369e1-8515-458a-99e3-cb9283fb73d1",
"attack-pattern--5cf0f3fb-3459-4a3d-ad3c-4700efcfecd8",
"attack-pattern--172f3845-7870-4c1c-80bd-251e10ce9f1e",
"attack-pattern--26d99677-799b-44ed-bc54-5fef76cbc72c",
"attack-pattern--be71cb85-e563-474f-8840-07da4ab201ed",
"domain-name--8b98bdde-8bcf-4325-b51a-89666b49c2b1",
"domain-name--0440734c-15d2-4a78-9e1f-f7bd861f76f5",
"domain-name--0c460c64-9a9d-478e-a0a4-0433ba7c9deb",
"domain-name--263fff58-928d-442e-a7bc-8cc9aef31ee3",
"domain-name--2e4e9bae-2292-4289-9fe1-2b245623e528",
"domain-name--8fd66513-f421-4ddf-8911-aad5ce039cb5",
"domain-name--be27b2fc-7e24-4acf-94b7-e8ab5aa251da",
"domain-name--3a0ad85f-b527-4cc0-9968-4f0c8f118e4b",
"domain-name--e4c8aeca-7c0a-4464-82fb-696f9e053eee",
"domain-name--bd35c94e-e875-474a-bce2-88746f3cddd2",
"domain-name--c6af8ee9-acad-409f-bb6c-073820998850",
"domain-name--19d3a34f-6134-4e8a-a3f6-7b00416ad3f2",
"domain-name--578b72ee-2b3e-4dc0-9992-3b211c4fbe8b",
"domain-name--06e5fa66-839c-4583-a2a1-96bd1474fa5e",
"domain-name--cac4285e-efa9-4692-bbe5-db6494f04250",
"domain-name--41fbc983-7949-4472-9390-94bfa4156d48",
"domain-name--736399a0-7c1d-4d61-913a-806286c41683",
"domain-name--c58de322-ccc5-41c3-bdbf-cd0f95baffd8",
"domain-name--1463f160-5d0b-42e5-ab58-a9e14dd14208",
"domain-name--fba5bdca-2fd9-48f6-ae3d-de539a1fc603",
"domain-name--32c6c3a3-3215-437b-a9ef-bd72e1bbf205",
"domain-name--047d160d-3a12-448b-afda-ca133ad178ae",
"domain-name--9510e736-9780-4c66-b443-ecdaef7bf8e1",
"domain-name--81f9814a-e8b6-44c1-bc14-59a10e69849c",
"domain-name--ce2b09a9-b789-4856-8fc6-35d3d0969d0d",
"domain-name--9f03cf30-ca60-4312-8f99-7dbe68130775",
"domain-name--8e3c1c98-21f7-4081-9ec1-e02808b973d7",
"domain-name--6b74b08c-bacf-45ff-872a-ad50cdc4a6e8",
"domain-name--fadf82df-9659-4548-9870-b437d64042bd",
"domain-name--e1df7c16-91f6-4773-bf94-5883e5be7f87",
"domain-name--99be0ed9-b394-4a45-9835-8e3b613f0971",
"domain-name--1ca123a5-4b46-4bcc-91a5-78d09abe9871",
"domain-name--a5790629-5ed2-48af-860d-17cd563869de",
"domain-name--73c50bdb-d258-4152-bb43-351fe13d7f1d",
"domain-name--7515c5f6-1d63-4735-8ead-72bc2a47b299",
"domain-name--52c1e65e-56b3-4c4e-87c5-d5e81f7e2fbb",
"domain-name--91801439-6f5f-4c0a-9d41-020ae94ae5e3",
"domain-name--f6566940-1e9f-49f1-b461-a4e944eddbc1",
"domain-name--34472b52-8a12-40e6-9c5b-3b8eb7ceb062",
"domain-name--084d8805-7049-46df-a09e-0e52d8061142",
"domain-name--7d0d55dc-3ec0-4922-bd45-5d0e9942970d",
"domain-name--eee93bdb-54df-48ed-8e2b-2e15dafc96ed",
"domain-name--377a5aa6-6c5c-4d0e-911f-22f754173ac2",
"domain-name--0789a611-43db-4db3-bd5a-fadda8a8bfd4",
"domain-name--f1458a07-eb03-4011-bc12-fef35de0a236",
"domain-name--d0dc6777-abc9-4942-a0ed-8a388fecffad",
"domain-name--d39fed4a-1a9b-4a65-8d3b-168ba4d08906",
"domain-name--ce131e1b-99e6-4331-97a1-8e85b7373bc5",
"domain-name--0676c51a-6c9f-402e-b1ee-a958cca194b4",
"domain-name--352511e3-0ead-43af-acde-18e497fbfe2c",
"indicator--16be39ca-e44e-4cf5-ad48-42f320c93edb",
"relationship--ed375bff-48f5-4a4d-bb65-3b4b671a5934",
"indicator--18dd1d40-c086-4abc-8705-979f8e4831ef",
"relationship--3b41cd12-aae4-4534-8787-a8cf7d5e7723",
"indicator--71d8575b-2aab-48f5-9d83-9a33c309a2f7",
"relationship--436c60c6-93f8-470a-94e7-ba78e5c3c572",
"indicator--fc215645-02bc-4d43-9e57-a755e6b26e5b",
"relationship--a7e14210-1348-498d-a89d-3ac2cfc4735a",
"indicator--6294ad4a-2547-4405-b9e7-f2e414a78124",
"relationship--127b9e47-5f61-484a-a9c8-3022170c86c6",
"indicator--6d3ba2fa-1e77-4bd2-be19-6100641f7ae9",
"relationship--11811a72-f1f1-4fe4-8011-f3a28a97d33e",
"indicator--b3c99328-be28-47b6-8c7f-d84e3a42b70b",
"relationship--dd245e19-e2db-431e-b26b-821f7898d6eb",
"indicator--8cfe095c-7f4c-46ec-81fb-3482784915fe",
"relationship--85803a60-3002-4305-b4a1-fe2aee7c79b3",
"indicator--6b536942-1407-4e0d-8bcf-c61250b08bb5",
"relationship--26b44fc9-52ca-45b2-8af1-928e4835d8cc",
"indicator--849d1112-f358-459d-8297-938bbe0072e5",
"relationship--86ca259b-d5ba-4837-9184-2da9462db5d5",
"indicator--f3c14fb0-bc94-4c38-8bca-8e73b2bf0a5f",
"relationship--70bf6a02-1f57-4d8d-8784-6b043d238607",
"indicator--bea3e6d7-8e58-45f5-a33f-eb44dce34729",
"relationship--a7fc7137-2194-4345-af3b-c1abdddd6b1f",
"indicator--6cd8d304-c9a1-47d2-8347-46d7a62320ae",
"relationship--f8dee5fc-cb72-4a3f-9fb7-f1b073243c09",
"indicator--1547656d-30b6-4596-ace2-009b2ccb6d49",
"relationship--7f8e2e29-4359-4436-8d38-b315d567ce5e",
"indicator--5f5228de-4a2e-457a-b00d-4f6441fdc97d",
"relationship--35b7d034-f36b-4d1b-92f3-083922af8e36",
"indicator--2fd8c9b6-b845-4f7f-b4e4-19bbb1eb942c",
"relationship--039efc78-a77e-46a7-839d-f58c0f1c02c0",
"indicator--10532643-a7e9-45c8-8bf7-cb88316199ac",
"relationship--5f3760a8-4ff3-49c2-9bfe-b8ac4a2fae3c",
"indicator--29cd0a0b-0ea5-4daf-a7a4-1c6c8209157c",
"relationship--e181396a-7cae-4fdd-a6d7-e5d4972012a6",
"indicator--fb1f897e-35b8-4892-9ff7-a03a5386f535",
"relationship--2b8a7145-1df2-4bf3-b22a-ccb4ff871fb8",
"indicator--284d88b3-b9f5-4983-a67d-b2458cc7ce42",
"relationship--80f80095-0357-4963-8b1e-e85d310c6e2e",
"indicator--f4691487-93d9-4694-8219-a389da1dbf4d",
"relationship--804988f7-5cde-42b9-bd6e-81def38e6ce1",
"indicator--4bfe0c88-67c5-4097-aea1-c42821331443",
"relationship--ba55d46d-87a2-498f-802c-74e864c2359d",
"indicator--f4956e3e-bafa-4f63-b845-6c2571c752d5",
"relationship--4cd3cfe2-f321-4e40-8605-046c24dd1b9e",
"indicator--1726c8ef-730d-437a-8771-fb63a8291de1",
"relationship--b55e118e-1454-4283-9c79-4b3756a1640b",
"indicator--ea981d7a-dd61-4884-b156-57d5df9f4ed5",
"relationship--6610d955-3eac-40d5-8f0f-49b19fced624",
"indicator--d93ff187-ed15-4497-a15d-8d939573fd57",
"relationship--07d18448-7fbc-4af5-a683-acfead418267",
"indicator--8c4cb30e-1224-4eaa-87d6-c19310815328",
"relationship--20c27a71-58b6-4cb4-a142-8deb919690db",
"indicator--bd7442a8-90c8-4510-ac37-b0a1bd210af0",
"relationship--c5e51201-af03-459b-8c49-95efa71da028",
"indicator--fd2174fd-d87e-423e-ba59-9c38fd22f8ab",
"relationship--afc277ac-7386-4485-8417-a4aa0c5d04f0",
"indicator--eb7d6b05-b7ff-4066-8b0d-757028ec84cd",
"relationship--463e8ff9-fec0-4a0a-b599-0ee1caac5b51",
"indicator--92f4da5b-330c-4eaf-b0b5-84e269b6b3e2",
"relationship--315a0c0e-ca22-4b78-ab0e-376b7ed9f03a",
"indicator--5b619e00-284a-4006-9867-821364ac7063",
"relationship--484ce8f5-2a7c-45b3-92a0-026704d3db70",
"indicator--f06006c5-4bd7-4cc0-ac3a-8720948b8888",
"relationship--0f62645f-4892-4527-90a4-9071e418a2ac",
"indicator--6b2b0bd9-0a75-4e82-b0a6-c8e6f5358c4d",
"relationship--13152c0f-37c8-40b3-a5f6-b9d782cb4f1b",
"indicator--72239e40-c07c-4064-a7a3-0e9a9344f6b9",
"relationship--c423cc51-be01-4cc5-b1eb-cd14360f44dd",
"indicator--ea4ce053-230f-4a84-bc51-b426a6c152b8",
"relationship--97f17f6c-9f5f-45c3-b13f-f07a962537dd",
"indicator--4b6ccb6d-1213-4b77-be91-26e65cd2a90d",
"relationship--5adc1e0d-1033-4946-b3d6-b2ecd1d3d775",
"indicator--1f4da9e3-a0cb-4338-b891-dcd33cc9bd52",
"relationship--0e693a1e-a0f6-48df-ae79-27b924c3e549",
"indicator--9bb1e6b5-c55f-4c5e-addc-ea27a895f1a9",
"relationship--9946b693-d7ce-49b1-9ffe-14680436701b",
"indicator--d1f01337-6971-4638-9607-d8d160338f8f",
"relationship--eb0978bf-97a7-4e91-b00e-e9c0de63bfbc",
"indicator--e68cf356-bc75-46c4-8671-20537dbfa38e",
"relationship--017ce478-3322-4cc3-9019-9719b1b2c9e6",
"indicator--0df52944-98d7-4797-bdf8-0b5f1401cae1",
"relationship--65f96cf1-610b-4a2e-82ea-df5059a1e51d",
"indicator--47405e88-3e95-4fe5-aa5d-acaa808a6c10",
"relationship--3beedc2e-d6f9-48d3-9fe6-285e398ecdba",
"indicator--51e3a48b-b127-4ec6-967e-7be0f7c45795",
"relationship--acf641db-eedd-4f41-97b4-3b7f5e8a3e08",
"indicator--bd811f8e-5747-4ab1-9b16-9f9b93529932",
"relationship--b0471ff2-aebf-492d-8e3a-70aacce9daf5",
"indicator--0f2c18b3-4d33-4c54-ba28-af049574d639",
"relationship--30f6e695-1164-493e-a135-13ad67c46083",
"indicator--fd34ef28-c9ed-4e35-8fe2-abddaf316cc2",
"relationship--5e860103-b1fd-4a4f-9e5e-1e24ba406d98",
"indicator--dd096dac-5722-4bc4-aab7-77c96b22f9f1",
"relationship--6e8a9677-b00d-4a9a-a422-49f5bbf07a33",
"indicator--efb86c98-0419-4f31-b167-d0a4201a11c3",
"relationship--348aa556-257f-4fbf-9fd8-67b350596094",
"indicator--d5623781-1270-495e-ba47-6c21281b7973",
"relationship--bb423dd6-c94e-44d4-a959-3e9d9c9f4baf"
],
"labels": [
"threat-report",
"threat-intelligence"
],
"created_by_ref": "identity--caf1dc18-12ad-4b11-a8ab-af65ebd7da1d",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.098Z",
"modified": "2026-03-03T13:20:18.099Z",
"confidence": 95,
"type": "identity",
"id": "identity--69aa5d6f-85af-4de1-8aae-4064ba1566c3",
"name": "Beijing Jiaotong University",
"identity_class": "organization",
"labels": [
"identity"
],
"description": "A specific university in China.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.099Z",
"modified": "2026-03-03T13:20:18.099Z",
"confidence": 95,
"type": "identity",
"id": "identity--6f0bf2cd-7561-4393-8250-44c39f8a12f8",
"name": "Zhejiang University",
"identity_class": "organization",
"labels": [
"identity"
],
"description": "A specific university in China.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.100Z",
"modified": "2026-03-03T13:20:18.100Z",
"confidence": 95,
"type": "identity",
"id": "identity--fd1e3790-7e3a-48a3-8684-16f17330c96f",
"name": "Palo Alto Networks",
"identity_class": "organization",
"labels": [
"identity"
],
"description": "A cybersecurity company.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.100Z",
"modified": "2026-03-03T13:20:18.100Z",
"confidence": 95,
"type": "identity",
"id": "identity--d3da56c0-c933-4ac5-94f4-a5aa68ae5a77",
"name": "CyberRisk Alliance",
"identity_class": "organization",
"labels": [
"identity"
],
"description": "A cybersecurity company",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.115Z",
"modified": "2026-03-03T13:20:18.115Z",
"confidence": 95,
"type": "identity",
"id": "identity--e7aaa346-3c47-410b-b7ac-2f53a69389c5",
"name": "Strobes Security",
"identity_class": "organization",
"labels": [
"identity"
],
"description": "A company providing cybersecurity services",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.115Z",
"modified": "2026-03-03T13:20:18.115Z",
"confidence": 95,
"type": "identity",
"id": "identity--68d5e0b1-4a32-4b0e-82f8-cf3521e297d9",
"name": "Garrett Calpouz",
"identity_class": "individual",
"labels": [
"identity"
],
"description": "A person, possibly a cybersecurity researcher or expert",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.116Z",
"modified": "2026-03-03T13:20:18.116Z",
"confidence": 95,
"type": "identity",
"id": "identity--798dea09-c600-4af2-b078-819fa8479138",
"name": "Cloudflare One",
"identity_class": "system",
"labels": [
"identity"
],
"description": "Cloudflare One is a product or service offered by Cloudflare.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.116Z",
"modified": "2026-03-03T13:20:18.116Z",
"confidence": 95,
"type": "identity",
"id": "identity--97c7100b-5163-4e33-a926-ff1bf2062824",
"name": "John Hultquist",
"identity_class": "individual",
"labels": [
"identity"
],
"description": "A cybersecurity expert and researcher",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.116Z",
"modified": "2026-03-03T13:20:18.116Z",
"confidence": 95,
"type": "identity",
"id": "identity--5644c017-50f4-4316-9112-85831636b4c9",
"name": "Andres Andreu",
"identity_class": "individual",
"labels": [
"identity"
],
"description": "Specific individual",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.116Z",
"modified": "2026-03-03T13:20:18.116Z",
"confidence": 95,
"type": "identity",
"id": "identity--a88478d8-481d-4fe4-80d1-5b1952ca2bbf",
"name": "Insikt Group®",
"identity_class": "organization",
"labels": [
"identity"
],
"description": "A cyber threat intelligence team known for its research and analysis.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.116Z",
"modified": "2026-03-03T13:20:18.116Z",
"confidence": 95,
"type": "identity",
"id": "identity--34563d1b-a2e9-44ab-a65f-fb43a343ee32",
"name": "CyberNewswire",
"identity_class": "organization",
"labels": [
"identity"
],
"description": "A company or organization related to cybersecurity",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.116Z",
"modified": "2026-03-03T13:20:18.116Z",
"confidence": 95,
"type": "identity",
"id": "identity--ef3514f5-090e-4090-8568-36680f106989",
"name": "Yuejia Cheng",
"identity_class": "individual",
"labels": [
"identity"
],
"description": "A specific individual, likely a researcher or academic.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.116Z",
"modified": "2026-03-03T13:20:18.116Z",
"confidence": 95,
"type": "identity",
"id": "identity--4de38111-9093-4cb0-ae1d-8512f5ee7773",
"name": "Cortex XSOAR",
"identity_class": "system",
"labels": [
"identity"
],
"description": "A security orchestration, automation, and response (SOAR) platform",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.117Z",
"modified": "2026-03-03T13:20:18.117Z",
"confidence": 95,
"type": "identity",
"id": "identity--39bc2030-ded5-40b5-be7a-6c2d627e2378",
"name": "Ali Khamenei",
"identity_class": "individual",
"labels": [
"identity"
],
"description": "The Supreme Leader of Iran",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.117Z",
"modified": "2026-03-03T13:20:18.117Z",
"confidence": 95,
"type": "identity",
"id": "identity--c877be6e-5a87-41d2-b67e-fc0c6a8c863a",
"name": "Cisco Talos",
"identity_class": "organization",
"labels": [
"identity"
],
"description": "A cybersecurity research organization",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.117Z",
"modified": "2026-03-03T13:20:18.117Z",
"confidence": 95,
"type": "identity",
"id": "identity--f7423a25-c230-4896-ac95-2374a11bb1e0",
"name": "Kailun Wang",
"identity_class": "individual",
"labels": [
"identity"
],
"description": "A specific individual, likely a researcher or academic.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.117Z",
"modified": "2026-03-03T13:20:18.117Z",
"confidence": 95,
"type": "identity",
"id": "identity--4fcb1491-74e5-4b75-8f63-5498c2b5f714",
"name": "Perplexity",
"identity_class": "organization",
"labels": [
"identity"
],
"description": "Perplexity is a specific entity, possibly related to a company or organization.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.117Z",
"modified": "2026-03-03T13:20:18.117Z",
"confidence": 95,
"type": "identity",
"id": "identity--f3bdd2a6-9aa9-4e4a-8593-165380c7ffd0",
"name": "Yunbo Yang",
"identity_class": "individual",
"labels": [
"identity"
],
"description": "A specific individual, likely a researcher or academic.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.118Z",
"modified": "2026-03-03T13:20:18.118Z",
"confidence": 95,
"type": "identity",
"id": "identity--6d7560b4-b89e-4459-b56b-c43ebd64a687",
"name": "Xiaoguo Li",
"identity_class": "individual",
"labels": [
"identity"
],
"description": "A specific individual, likely a researcher or academic.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.118Z",
"modified": "2026-03-03T13:20:18.118Z",
"confidence": 95,
"type": "identity",
"id": "identity--083217f4-2992-4a6c-be9f-11a0e6716025",
"name": "Constella",
"identity_class": "organization",
"labels": [
"identity"
],
"description": "A cybersecurity company that provides threat intelligence services.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.118Z",
"modified": "2026-03-03T13:20:18.118Z",
"confidence": 95,
"type": "identity",
"id": "identity--d48d0179-a8bc-4c9e-89ef-4347fcbce1fa",
"name": "Barracuda",
"identity_class": "organization",
"labels": [
"identity"
],
"description": "Barracuda Networks, a cybersecurity company",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.118Z",
"modified": "2026-03-03T13:20:18.118Z",
"confidence": 95,
"type": "identity",
"id": "identity--8dd81c81-6fef-45ca-b1e1-160489fc3f14",
"name": "OpenClaw",
"identity_class": "system",
"labels": [
"identity"
],
"description": "OpenClaw is a security tool that has addressed a high-severity vulnerability that could have allowed unauthorized access.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.118Z",
"modified": "2026-03-03T13:20:18.118Z",
"confidence": 95,
"type": "identity",
"id": "identity--98f20e05-ff41-460d-88f1-77efc295dfe2",
"name": "Sonatype",
"identity_class": "organization",
"labels": [
"identity"
],
"description": "Sonatype is a software company.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.118Z",
"modified": "2026-03-03T13:20:18.118Z",
"confidence": 95,
"type": "identity",
"id": "identity--700e8e95-d6a0-4451-ae5a-5dc670c96905",
"name": "Morpheus",
"identity_class": "system",
"labels": [
"identity"
],
"description": "Morpheus is a specific named tool or software.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.118Z",
"modified": "2026-03-03T13:20:18.118Z",
"confidence": 95,
"type": "identity",
"id": "identity--e579f0b6-29fc-4f87-be26-0870951a61da",
"name": "Android",
"identity_class": "organization",
"labels": [
"identity"
],
"description": "Android is a company",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.118Z",
"modified": "2026-03-03T13:20:18.118Z",
"confidence": 95,
"type": "identity",
"id": "identity--421dd0c0-c7eb-4edf-9cc1-bdfd1cbe9d15",
"name": "Akamai",
"identity_class": "organization",
"labels": [
"identity"
],
"description": "Akamai is a content delivery network and cloud services provider that offers cybersecurity solutions.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.118Z",
"modified": "2026-03-03T13:20:18.118Z",
"confidence": 95,
"type": "identity",
"id": "identity--f32388a2-ff73-427d-8139-65139b46fda1",
"name": "Ledger",
"identity_class": "organization",
"labels": [
"identity"
],
"description": "A company that produces cryptocurrency hardware wallets",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.119Z",
"modified": "2026-03-03T13:20:18.119Z",
"confidence": 95,
"type": "identity",
"id": "identity--d6fbbbd5-d4a2-4517-87ee-699f986f5720",
"name": "Link11",
"identity_class": "organization",
"labels": [
"identity"
],
"description": "A cybersecurity company",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.119Z",
"modified": "2026-03-03T13:20:18.119Z",
"confidence": 95,
"type": "identity",
"id": "identity--161fc746-cd49-4615-ab48-81a93a1b16b4",
"name": "GitHub",
"identity_class": "organization",
"labels": [
"identity"
],
"description": "GitHub is a company",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.119Z",
"modified": "2026-03-03T13:20:18.119Z",
"confidence": 95,
"type": "identity",
"id": "identity--f9f67fe7-735c-4107-8f6e-5dc3164bc5ce",
"name": "CISOs",
"identity_class": "individual",
"labels": [
"identity"
],
"description": "Chief Information Security Officers",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.119Z",
"modified": "2026-03-03T13:20:18.119Z",
"confidence": 95,
"type": "vulnerability",
"id": "vulnerability--3d1131b8-f17e-4e78-b180-e044e863e774",
"name": "CVE-2026-21513",
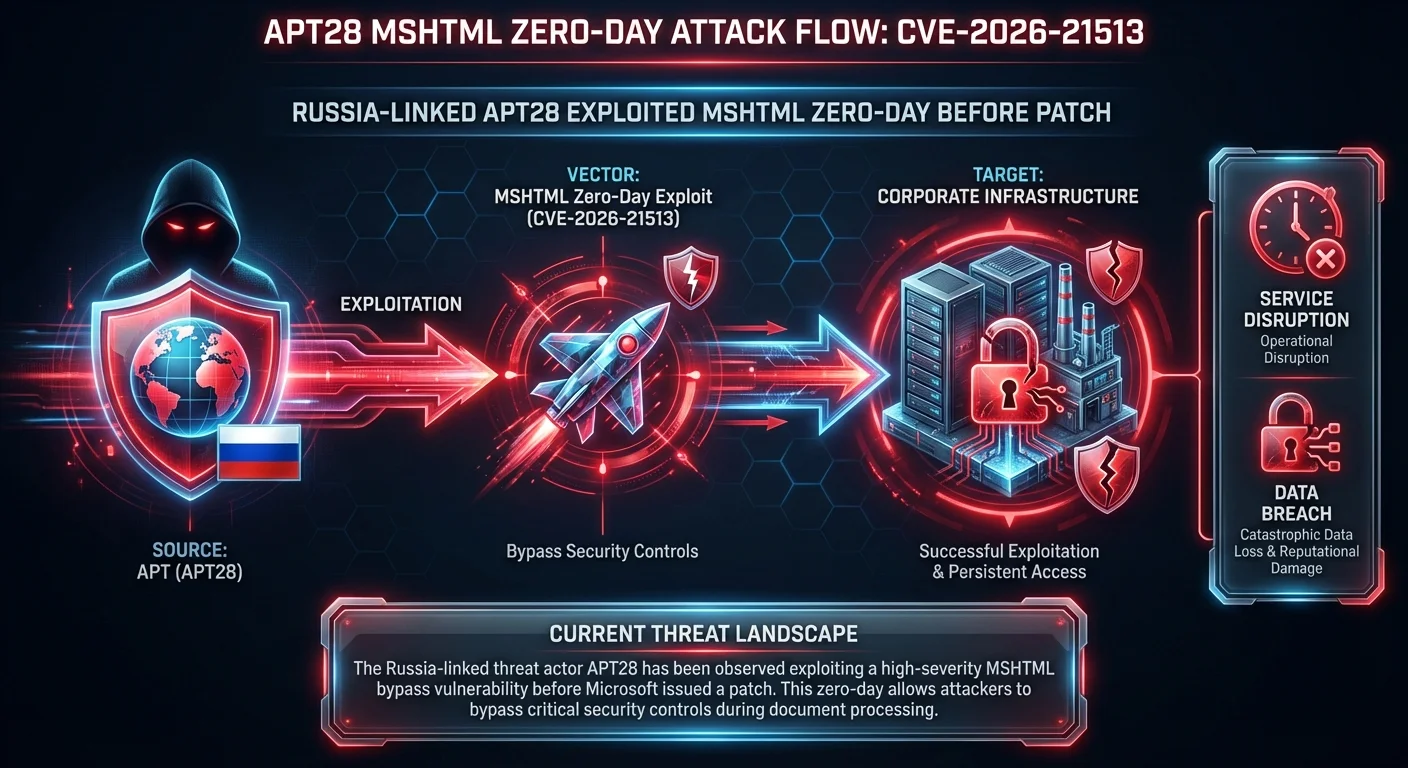
"description": "Protection mechanism failure in MSHTML Framework allows an unauthorized attacker to bypass a security feature over a network.. CVSS Score: 8.8 (HIGH). CISA KEV: Active exploitation confirmed. EPSS: 4.1% exploitation probability",
"x_cvss_score": 8.8,
"x_cvss_severity": "HIGH",
"x_kev_status": true,
"x_epss_score": 0.04119,
"external_references": [
{
"source_name": "cve",
"external_id": "CVE-2026-21513",
"url": "https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2026-21513"
},
{
"source_name": "nvd",
"external_id": "CVE-2026-21513",
"url": "https://nvd.nist.gov/vuln/detail/CVE-2026-21513"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"vulnerability"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.119Z",
"modified": "2026-03-03T13:20:18.119Z",
"confidence": 95,
"type": "vulnerability",
"id": "vulnerability--628167a8-ec55-45db-a347-8df2801619bb",
"name": "CVE-2026-0628",
"description": "Insufficient policy enforcement in WebView tag in Google Chrome prior to 143.0.7499.192 allowed an attacker who convinced a user to install a malicious extension to inject scripts or HTML into a privileged page via a crafted Chrome Extension. (Chromium security severity: High). CVSS Score: 8.8 (HIGH). EPSS: 0.0% exploitation probability",
"x_cvss_score": 8.8,
"x_cvss_severity": "HIGH",
"x_kev_status": false,
"x_epss_score": 0.00022,
"external_references": [
{
"source_name": "cve",
"external_id": "CVE-2026-0628",
"url": "https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2026-0628"
},
{
"source_name": "nvd",
"external_id": "CVE-2026-0628",
"url": "https://nvd.nist.gov/vuln/detail/CVE-2026-0628"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"vulnerability"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.120Z",
"modified": "2026-03-03T13:20:18.120Z",
"confidence": 80,
"type": "identity",
"id": "identity--67504360-5ac2-467e-a28b-a560b4f91de9",
"name": "MSHTML",
"identity_class": "system",
"labels": [
"identity"
],
"description": "A Microsoft HTML component",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.120Z",
"modified": "2026-03-03T13:20:18.120Z",
"confidence": 95,
"type": "threat-actor",
"id": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"name": "APT28",
"threat_actor_types": [
"hacker"
],
"labels": [
"threat-actor"
],
"description": "APT28, also known as Fancy Bear, is a sophisticated threat actor group attributed to Russian intelligence services, known for cyber espionage campaigns targeting government, defense, and other high-profile sectors. They are known for their advanced tactics, techniques, and procedures (TTPs), including the use of zero-day exploits and social engineering. APT28 has been linked to several high-profile breaches and is considered a significant threat to global cybersecurity.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.120Z",
"modified": "2026-03-03T13:20:18.120Z",
"confidence": 90,
"type": "attack-pattern",
"id": "attack-pattern--280ebd89-59bc-4ae2-a9db-1c01a56e50dc",
"name": "Exploit Public-Facing Application",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "initial-access"
}
],
"x_mitre_id": "T1190",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1190/",
"external_id": "T1190"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.120Z",
"modified": "2026-03-03T13:20:18.120Z",
"confidence": 90,
"type": "attack-pattern",
"id": "attack-pattern--e5974f70-5745-450a-908a-6483ad9c4678",
"name": "Exploitation for Client Execution",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "execution"
}
],
"x_mitre_id": "T1203",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1203/",
"external_id": "T1203"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.120Z",
"modified": "2026-03-03T13:20:18.120Z",
"confidence": 90,
"type": "attack-pattern",
"id": "attack-pattern--e8d516a9-a107-4c4b-806f-bc9c612eef18",
"name": "Adversary-in-the-Middle",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "credential-access"
},
{
"kill_chain_name": "mitre-attack",
"phase_name": "collection"
}
],
"x_mitre_id": "T1557",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1557/",
"external_id": "T1557"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.120Z",
"modified": "2026-03-03T13:20:18.120Z",
"confidence": 90,
"type": "attack-pattern",
"id": "attack-pattern--2da268b5-7100-4dbc-b23b-d5deafdf268c",
"name": "Spearphishing Attachment",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "initial-access"
}
],
"x_mitre_id": "T1566.001",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1566/001/",
"external_id": "T1566.001"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.120Z",
"modified": "2026-03-03T13:20:18.120Z",
"confidence": 90,
"type": "attack-pattern",
"id": "attack-pattern--baad7d00-8591-4c49-8f48-fabb6a35df65",
"name": "Spearphishing Link",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "initial-access"
}
],
"x_mitre_id": "T1566.002",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1566/002/",
"external_id": "T1566.002"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.120Z",
"modified": "2026-03-03T13:20:18.120Z",
"confidence": 90,
"type": "attack-pattern",
"id": "attack-pattern--c627c29c-1385-4d76-9046-9c2db86dab11",
"name": "Spearphishing via Service",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "initial-access"
}
],
"x_mitre_id": "T1566.003",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1566/003/",
"external_id": "T1566.003"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.120Z",
"modified": "2026-03-03T13:20:18.120Z",
"confidence": 90,
"type": "attack-pattern",
"id": "attack-pattern--f33f5834-6a9a-4727-88a5-9d35eeba1cff",
"name": "Abuse Elevation Control Mechanism",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "privilege-escalation"
},
{
"kill_chain_name": "mitre-attack",
"phase_name": "defense-evasion"
}
],
"x_mitre_id": "T1548",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1548/",
"external_id": "T1548"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.120Z",
"modified": "2026-03-03T13:20:18.120Z",
"confidence": 90,
"type": "attack-pattern",
"id": "attack-pattern--2d26e3d0-4bbf-44c3-aa9e-5aeab4937638",
"name": "Access Token Manipulation",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "defense-evasion"
},
{
"kill_chain_name": "mitre-attack",
"phase_name": "privilege-escalation"
}
],
"x_mitre_id": "T1134",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1134/",
"external_id": "T1134"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.120Z",
"modified": "2026-03-03T13:20:18.120Z",
"confidence": 90,
"type": "attack-pattern",
"id": "attack-pattern--13fc9cbe-9444-4eba-872b-a44565ae3ab7",
"name": "Supply Chain Compromise",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "initial-access"
}
],
"x_mitre_id": "T1195",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1195/",
"external_id": "T1195"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.120Z",
"modified": "2026-03-03T13:20:18.120Z",
"confidence": 85,
"type": "attack-pattern",
"id": "attack-pattern--775a5581-fd79-4cfc-a505-6d409b3bbfba",
"name": "Browser Session Hijacking",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "collection"
}
],
"x_mitre_id": "T1185",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1185/",
"external_id": "T1185"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.120Z",
"modified": "2026-03-03T13:20:18.120Z",
"confidence": 73,
"type": "attack-pattern",
"id": "attack-pattern--a45b8295-9056-4ed5-b811-6e7d2a71483e",
"name": "Multi-Factor Authentication",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "credential-access"
},
{
"kill_chain_name": "mitre-attack",
"phase_name": "defense-evasion"
},
{
"kill_chain_name": "mitre-attack",
"phase_name": "persistence"
}
],
"x_mitre_id": "T1556.006",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1556/006/",
"external_id": "T1556.006"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.120Z",
"modified": "2026-03-03T13:20:18.120Z",
"confidence": 70,
"type": "attack-pattern",
"id": "attack-pattern--d2a77ce3-d278-4f77-97f0-227b744a33d3",
"name": "Archive via Utility",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "collection"
}
],
"x_mitre_id": "T1560.001",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1560/001/",
"external_id": "T1560.001"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.120Z",
"modified": "2026-03-03T13:20:18.120Z",
"confidence": 70,
"type": "attack-pattern",
"id": "attack-pattern--a6ff86fe-f269-42e5-9428-ab17d04e30e2",
"name": "Screen Capture",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "collection"
}
],
"x_mitre_id": "T1113",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1113/",
"external_id": "T1113"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.120Z",
"modified": "2026-03-03T13:20:18.120Z",
"confidence": 70,
"type": "attack-pattern",
"id": "attack-pattern--27b36b6d-ae90-4767-b07a-563ecef589ea",
"name": "Scheduled Task",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "execution"
},
{
"kill_chain_name": "mitre-attack",
"phase_name": "persistence"
},
{
"kill_chain_name": "mitre-attack",
"phase_name": "privilege-escalation"
}
],
"x_mitre_id": "T1053.005",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1053/005/",
"external_id": "T1053.005"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.120Z",
"modified": "2026-03-03T13:20:18.120Z",
"confidence": 70,
"type": "attack-pattern",
"id": "attack-pattern--ed3369e1-8515-458a-99e3-cb9283fb73d1",
"name": "Socket Filters",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "defense-evasion"
},
{
"kill_chain_name": "mitre-attack",
"phase_name": "persistence"
},
{
"kill_chain_name": "mitre-attack",
"phase_name": "command-and-control"
}
],
"x_mitre_id": "T1205.002",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1205/002/",
"external_id": "T1205.002"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.120Z",
"modified": "2026-03-03T13:20:18.120Z",
"confidence": 70,
"type": "attack-pattern",
"id": "attack-pattern--5cf0f3fb-3459-4a3d-ad3c-4700efcfecd8",
"name": "Boot or Logon Initialization Scripts",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "persistence"
},
{
"kill_chain_name": "mitre-attack",
"phase_name": "privilege-escalation"
}
],
"x_mitre_id": "T1037",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1037/",
"external_id": "T1037"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.120Z",
"modified": "2026-03-03T13:20:18.120Z",
"confidence": 68,
"type": "attack-pattern",
"id": "attack-pattern--172f3845-7870-4c1c-80bd-251e10ce9f1e",
"name": "Browser Extensions",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "persistence"
}
],
"x_mitre_id": "T1176.001",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1176/001/",
"external_id": "T1176.001"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.120Z",
"modified": "2026-03-03T13:20:18.120Z",
"confidence": 66,
"type": "attack-pattern",
"id": "attack-pattern--26d99677-799b-44ed-bc54-5fef76cbc72c",
"name": "Outlook Home Page",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "persistence"
}
],
"x_mitre_id": "T1137.004",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1137/004/",
"external_id": "T1137.004"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2026-03-03T13:20:18.120Z",
"modified": "2026-03-03T13:20:18.120Z",
"confidence": 65,
"type": "attack-pattern",
"id": "attack-pattern--be71cb85-e563-474f-8840-07da4ab201ed",
"name": "Asymmetric Cryptography",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "command-and-control"
}
],
"x_mitre_id": "T1573.002",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1573/002/",
"external_id": "T1573.002"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"type": "domain-name",
"value": "13003.vip",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--8b98bdde-8bcf-4325-b51a-89666b49c2b1"
},
{
"type": "domain-name",
"value": "5ql.site",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--0440734c-15d2-4a78-9e1f-f7bd861f76f5"
},
{
"type": "domain-name",
"value": "argosonline.vip",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--0c460c64-9a9d-478e-a0a4-0433ba7c9deb"
},
{
"type": "domain-name",
"value": "argosgroup.vip",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--263fff58-928d-442e-a7bc-8cc9aef31ee3"
},
{
"type": "domain-name",
"value": "dermatologyhormones.info",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--2e4e9bae-2292-4289-9fe1-2b245623e528"
},
{
"type": "domain-name",
"value": "greaterclevelandconnection.com",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--8fd66513-f421-4ddf-8911-aad5ce039cb5"
},
{
"type": "domain-name",
"value": "imvickykumar999.online",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--be27b2fc-7e24-4acf-94b7-e8ab5aa251da"
},
{
"type": "domain-name",
"value": "multiproshop.xyz",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--3a0ad85f-b527-4cc0-9968-4f0c8f118e4b"
},
{
"type": "domain-name",
"value": "nationwiderelocations.in",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--e4c8aeca-7c0a-4464-82fb-696f9e053eee"
},
{
"type": "domain-name",
"value": "thetrapstar.com",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--bd35c94e-e875-474a-bce2-88746f3cddd2"
},
{
"type": "domain-name",
"value": "www.allmartsonline.com",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--c6af8ee9-acad-409f-bb6c-073820998850"
},
{
"type": "domain-name",
"value": "www.imvickykumar999.online",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--19d3a34f-6134-4e8a-a3f6-7b00416ad3f2"
},
{
"type": "domain-name",
"value": "www.ucdim.com",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--578b72ee-2b3e-4dc0-9992-3b211c4fbe8b"
},
{
"type": "domain-name",
"value": "ad-drivers.com",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--06e5fa66-839c-4583-a2a1-96bd1474fa5e"
},
{
"type": "domain-name",
"value": "1156zz.net",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--cac4285e-efa9-4692-bbe5-db6494f04250"
},
{
"type": "domain-name",
"value": "jefimenko.com",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--41fbc983-7949-4472-9390-94bfa4156d48"
},
{
"type": "domain-name",
"value": "quickcloud.shop",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--736399a0-7c1d-4d61-913a-806286c41683"
},
{
"type": "domain-name",
"value": "www.biopar.space",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--c58de322-ccc5-41c3-bdbf-cd0f95baffd8"
},
{
"type": "domain-name",
"value": "annaleec21.com",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--1463f160-5d0b-42e5-ab58-a9e14dd14208"
},
{
"type": "domain-name",
"value": "availity4u.com",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--fba5bdca-2fd9-48f6-ae3d-de539a1fc603"
},
{
"type": "domain-name",
"value": "amstyle.fashion",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--32c6c3a3-3215-437b-a9ef-bd72e1bbf205"
},
{
"type": "domain-name",
"value": "essaypropromo.top",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--047d160d-3a12-448b-afda-ca133ad178ae"
},
{
"type": "domain-name",
"value": "fodi-social.store",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--9510e736-9780-4c66-b443-ecdaef7bf8e1"
},
{
"type": "domain-name",
"value": "g8t.me",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--81f9814a-e8b6-44c1-bc14-59a10e69849c"
},
{
"type": "domain-name",
"value": "jasalivestreamingmurah.com",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--ce2b09a9-b789-4856-8fc6-35d3d0969d0d"
},
{
"type": "domain-name",
"value": "litonali.com",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--9f03cf30-ca60-4312-8f99-7dbe68130775"
},
{
"type": "domain-name",
"value": "mido-plus.store",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--8e3c1c98-21f7-4081-9ec1-e02808b973d7"
},
{
"type": "domain-name",
"value": "tbfs.xyz",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--6b74b08c-bacf-45ff-872a-ad50cdc4a6e8"
},
{
"type": "domain-name",
"value": "yardbombsgone.com",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--fadf82df-9659-4548-9870-b437d64042bd"
},
{
"type": "domain-name",
"value": "zenrootfeet.life",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--e1df7c16-91f6-4773-bf94-5883e5be7f87"
},
{
"type": "domain-name",
"value": "bhaktibhavna.space",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--99be0ed9-b394-4a45-9835-8e3b613f0971"
},
{
"type": "domain-name",
"value": "cuneiform.ru",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--1ca123a5-4b46-4bcc-91a5-78d09abe9871"
},
{
"type": "domain-name",
"value": "escuelaastrouranianaydemisterios.org",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--a5790629-5ed2-48af-860d-17cd563869de"
},
{
"type": "domain-name",
"value": "h9986.com",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--73c50bdb-d258-4152-bb43-351fe13d7f1d"
},
{
"type": "domain-name",
"value": "houseofkings.online",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--7515c5f6-1d63-4735-8ead-72bc2a47b299"
},
{
"type": "domain-name",
"value": "quedecositas.com",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--52c1e65e-56b3-4c4e-87c5-d5e81f7e2fbb"
},
{
"type": "domain-name",
"value": "techiq.xyz",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--91801439-6f5f-4c0a-9d41-020ae94ae5e3"
},
{
"type": "domain-name",
"value": "wilbursoot.store",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--f6566940-1e9f-49f1-b461-a4e944eddbc1"
},
{
"type": "domain-name",
"value": "wiredtech-ux-demo2.online",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--34472b52-8a12-40e6-9c5b-3b8eb7ceb062"
},
{
"type": "domain-name",
"value": "youtubethumbnaildownloader.tech",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--084d8805-7049-46df-a09e-0e52d8061142"
},
{
"type": "domain-name",
"value": "0000111.xyz",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--7d0d55dc-3ec0-4922-bd45-5d0e9942970d"
},
{
"type": "domain-name",
"value": "00dd22495661v772c.christmas",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--eee93bdb-54df-48ed-8e2b-2e15dafc96ed"
},
{
"type": "domain-name",
"value": "007win.link",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--377a5aa6-6c5c-4d0e-911f-22f754173ac2"
},
{
"type": "domain-name",
"value": "010.one",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--0789a611-43db-4db3-bd5a-fadda8a8bfd4"
},
{
"type": "domain-name",
"value": "010097.bond",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--f1458a07-eb03-4011-bc12-fef35de0a236"
},
{
"type": "domain-name",
"value": "010417712.email",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--d0dc6777-abc9-4942-a0ed-8a388fecffad"
},
{
"type": "domain-name",
"value": "01044323111.click",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--d39fed4a-1a9b-4a65-8d3b-168ba4d08906"
},
{
"type": "domain-name",
"value": "012226.com",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--ce131e1b-99e6-4331-97a1-8e85b7373bc5"
},
{
"type": "domain-name",
"value": "017805.com",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--0676c51a-6c9f-402e-b1ee-a958cca194b4"
},
{
"type": "domain-name",
"value": "030129.com",
"source": "OTX-Subscribed",
"pulse_name": "Infrastructure of Interest: Medium Confidence FastFlux",
"id": "domain-name--352511e3-0ead-43af-acde-18e497fbfe2c"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--16be39ca-e44e-4cf5-ad48-42f320c93edb",
"created": "2026-03-03T13:18:40.289Z",
"modified": "2026-03-03T13:18:40.289Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = '13003.vip']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.289Z",
"labels": [
"malicious-activity"
],
"confidence": 75
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--ed375bff-48f5-4a4d-bb65-3b4b671a5934",
"created": "2026-03-03T13:18:40.289Z",
"modified": "2026-03-03T13:18:40.289Z",
"relationship_type": "based-on",
"source_ref": "indicator--16be39ca-e44e-4cf5-ad48-42f320c93edb",
"target_ref": "domain-name--8b98bdde-8bcf-4325-b51a-89666b49c2b1"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--18dd1d40-c086-4abc-8705-979f8e4831ef",
"created": "2026-03-03T13:18:40.310Z",
"modified": "2026-03-03T13:18:40.310Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = '5ql.site']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.310Z",
"labels": [
"malicious-activity"
],
"confidence": 75
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--3b41cd12-aae4-4534-8787-a8cf7d5e7723",
"created": "2026-03-03T13:18:40.310Z",
"modified": "2026-03-03T13:18:40.310Z",
"relationship_type": "based-on",
"source_ref": "indicator--18dd1d40-c086-4abc-8705-979f8e4831ef",
"target_ref": "domain-name--0440734c-15d2-4a78-9e1f-f7bd861f76f5"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--71d8575b-2aab-48f5-9d83-9a33c309a2f7",
"created": "2026-03-03T13:18:40.330Z",
"modified": "2026-03-03T13:18:40.330Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'argosonline.vip']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.330Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--436c60c6-93f8-470a-94e7-ba78e5c3c572",
"created": "2026-03-03T13:18:40.330Z",
"modified": "2026-03-03T13:18:40.330Z",
"relationship_type": "based-on",
"source_ref": "indicator--71d8575b-2aab-48f5-9d83-9a33c309a2f7",
"target_ref": "domain-name--0c460c64-9a9d-478e-a0a4-0433ba7c9deb"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--fc215645-02bc-4d43-9e57-a755e6b26e5b",
"created": "2026-03-03T13:18:40.351Z",
"modified": "2026-03-03T13:18:40.351Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'argosgroup.vip']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.351Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--a7e14210-1348-498d-a89d-3ac2cfc4735a",
"created": "2026-03-03T13:18:40.351Z",
"modified": "2026-03-03T13:18:40.351Z",
"relationship_type": "based-on",
"source_ref": "indicator--fc215645-02bc-4d43-9e57-a755e6b26e5b",
"target_ref": "domain-name--263fff58-928d-442e-a7bc-8cc9aef31ee3"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--6294ad4a-2547-4405-b9e7-f2e414a78124",
"created": "2026-03-03T13:18:40.370Z",
"modified": "2026-03-03T13:18:40.370Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'dermatologyhormones.info']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.370Z",
"labels": [
"malicious-activity"
],
"confidence": 75
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--127b9e47-5f61-484a-a9c8-3022170c86c6",
"created": "2026-03-03T13:18:40.370Z",
"modified": "2026-03-03T13:18:40.370Z",
"relationship_type": "based-on",
"source_ref": "indicator--6294ad4a-2547-4405-b9e7-f2e414a78124",
"target_ref": "domain-name--2e4e9bae-2292-4289-9fe1-2b245623e528"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--6d3ba2fa-1e77-4bd2-be19-6100641f7ae9",
"created": "2026-03-03T13:18:40.390Z",
"modified": "2026-03-03T13:18:40.390Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'greaterclevelandconnection.com']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.390Z",
"labels": [
"malicious-activity"
],
"confidence": 75
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--11811a72-f1f1-4fe4-8011-f3a28a97d33e",
"created": "2026-03-03T13:18:40.390Z",
"modified": "2026-03-03T13:18:40.390Z",
"relationship_type": "based-on",
"source_ref": "indicator--6d3ba2fa-1e77-4bd2-be19-6100641f7ae9",
"target_ref": "domain-name--8fd66513-f421-4ddf-8911-aad5ce039cb5"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--b3c99328-be28-47b6-8c7f-d84e3a42b70b",
"created": "2026-03-03T13:18:40.411Z",
"modified": "2026-03-03T13:18:40.411Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'imvickykumar999.online']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.411Z",
"labels": [
"malicious-activity"
],
"confidence": 80
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--dd245e19-e2db-431e-b26b-821f7898d6eb",
"created": "2026-03-03T13:18:40.411Z",
"modified": "2026-03-03T13:18:40.411Z",
"relationship_type": "based-on",
"source_ref": "indicator--b3c99328-be28-47b6-8c7f-d84e3a42b70b",
"target_ref": "domain-name--be27b2fc-7e24-4acf-94b7-e8ab5aa251da"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--8cfe095c-7f4c-46ec-81fb-3482784915fe",
"created": "2026-03-03T13:18:40.429Z",
"modified": "2026-03-03T13:18:40.429Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'multiproshop.xyz']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.429Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--85803a60-3002-4305-b4a1-fe2aee7c79b3",
"created": "2026-03-03T13:18:40.429Z",
"modified": "2026-03-03T13:18:40.429Z",
"relationship_type": "based-on",
"source_ref": "indicator--8cfe095c-7f4c-46ec-81fb-3482784915fe",
"target_ref": "domain-name--3a0ad85f-b527-4cc0-9968-4f0c8f118e4b"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--6b536942-1407-4e0d-8bcf-c61250b08bb5",
"created": "2026-03-03T13:18:40.446Z",
"modified": "2026-03-03T13:18:40.447Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'nationwiderelocations.in']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.447Z",
"labels": [
"malicious-activity"
],
"confidence": 75
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--26b44fc9-52ca-45b2-8af1-928e4835d8cc",
"created": "2026-03-03T13:18:40.447Z",
"modified": "2026-03-03T13:18:40.447Z",
"relationship_type": "based-on",
"source_ref": "indicator--6b536942-1407-4e0d-8bcf-c61250b08bb5",
"target_ref": "domain-name--e4c8aeca-7c0a-4464-82fb-696f9e053eee"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--849d1112-f358-459d-8297-938bbe0072e5",
"created": "2026-03-03T13:18:40.464Z",
"modified": "2026-03-03T13:18:40.464Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'thetrapstar.com']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.464Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--86ca259b-d5ba-4837-9184-2da9462db5d5",
"created": "2026-03-03T13:18:40.464Z",
"modified": "2026-03-03T13:18:40.464Z",
"relationship_type": "based-on",
"source_ref": "indicator--849d1112-f358-459d-8297-938bbe0072e5",
"target_ref": "domain-name--bd35c94e-e875-474a-bce2-88746f3cddd2"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--f3c14fb0-bc94-4c38-8bca-8e73b2bf0a5f",
"created": "2026-03-03T13:18:40.481Z",
"modified": "2026-03-03T13:18:40.481Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'www.allmartsonline.com']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.481Z",
"labels": [
"malicious-activity"
],
"confidence": 75
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--70bf6a02-1f57-4d8d-8784-6b043d238607",
"created": "2026-03-03T13:18:40.481Z",
"modified": "2026-03-03T13:18:40.481Z",
"relationship_type": "based-on",
"source_ref": "indicator--f3c14fb0-bc94-4c38-8bca-8e73b2bf0a5f",
"target_ref": "domain-name--c6af8ee9-acad-409f-bb6c-073820998850"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--bea3e6d7-8e58-45f5-a33f-eb44dce34729",
"created": "2026-03-03T13:18:40.498Z",
"modified": "2026-03-03T13:18:40.498Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'www.imvickykumar999.online']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.498Z",
"labels": [
"malicious-activity"
],
"confidence": 80
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--a7fc7137-2194-4345-af3b-c1abdddd6b1f",
"created": "2026-03-03T13:18:40.498Z",
"modified": "2026-03-03T13:18:40.498Z",
"relationship_type": "based-on",
"source_ref": "indicator--bea3e6d7-8e58-45f5-a33f-eb44dce34729",
"target_ref": "domain-name--19d3a34f-6134-4e8a-a3f6-7b00416ad3f2"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--6cd8d304-c9a1-47d2-8347-46d7a62320ae",
"created": "2026-03-03T13:18:40.514Z",
"modified": "2026-03-03T13:18:40.514Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'www.ucdim.com']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.514Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--f8dee5fc-cb72-4a3f-9fb7-f1b073243c09",
"created": "2026-03-03T13:18:40.514Z",
"modified": "2026-03-03T13:18:40.514Z",
"relationship_type": "based-on",
"source_ref": "indicator--6cd8d304-c9a1-47d2-8347-46d7a62320ae",
"target_ref": "domain-name--578b72ee-2b3e-4dc0-9992-3b211c4fbe8b"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--1547656d-30b6-4596-ace2-009b2ccb6d49",
"created": "2026-03-03T13:18:40.530Z",
"modified": "2026-03-03T13:18:40.530Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'ad-drivers.com']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.530Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--7f8e2e29-4359-4436-8d38-b315d567ce5e",
"created": "2026-03-03T13:18:40.530Z",
"modified": "2026-03-03T13:18:40.530Z",
"relationship_type": "based-on",
"source_ref": "indicator--1547656d-30b6-4596-ace2-009b2ccb6d49",
"target_ref": "domain-name--06e5fa66-839c-4583-a2a1-96bd1474fa5e"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--5f5228de-4a2e-457a-b00d-4f6441fdc97d",
"created": "2026-03-03T13:18:40.549Z",
"modified": "2026-03-03T13:18:40.549Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = '1156zz.net']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.549Z",
"labels": [
"malicious-activity"
],
"confidence": 75
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--35b7d034-f36b-4d1b-92f3-083922af8e36",
"created": "2026-03-03T13:18:40.549Z",
"modified": "2026-03-03T13:18:40.549Z",
"relationship_type": "based-on",
"source_ref": "indicator--5f5228de-4a2e-457a-b00d-4f6441fdc97d",
"target_ref": "domain-name--cac4285e-efa9-4692-bbe5-db6494f04250"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--2fd8c9b6-b845-4f7f-b4e4-19bbb1eb942c",
"created": "2026-03-03T13:18:40.564Z",
"modified": "2026-03-03T13:18:40.564Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'jefimenko.com']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.564Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--039efc78-a77e-46a7-839d-f58c0f1c02c0",
"created": "2026-03-03T13:18:40.564Z",
"modified": "2026-03-03T13:18:40.564Z",
"relationship_type": "based-on",
"source_ref": "indicator--2fd8c9b6-b845-4f7f-b4e4-19bbb1eb942c",
"target_ref": "domain-name--41fbc983-7949-4472-9390-94bfa4156d48"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--10532643-a7e9-45c8-8bf7-cb88316199ac",
"created": "2026-03-03T13:18:40.580Z",
"modified": "2026-03-03T13:18:40.580Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'quickcloud.shop']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.580Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--5f3760a8-4ff3-49c2-9bfe-b8ac4a2fae3c",
"created": "2026-03-03T13:18:40.580Z",
"modified": "2026-03-03T13:18:40.580Z",
"relationship_type": "based-on",
"source_ref": "indicator--10532643-a7e9-45c8-8bf7-cb88316199ac",
"target_ref": "domain-name--736399a0-7c1d-4d61-913a-806286c41683"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--29cd0a0b-0ea5-4daf-a7a4-1c6c8209157c",
"created": "2026-03-03T13:18:40.596Z",
"modified": "2026-03-03T13:18:40.596Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'www.biopar.space']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.596Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--e181396a-7cae-4fdd-a6d7-e5d4972012a6",
"created": "2026-03-03T13:18:40.596Z",
"modified": "2026-03-03T13:18:40.596Z",
"relationship_type": "based-on",
"source_ref": "indicator--29cd0a0b-0ea5-4daf-a7a4-1c6c8209157c",
"target_ref": "domain-name--c58de322-ccc5-41c3-bdbf-cd0f95baffd8"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--fb1f897e-35b8-4892-9ff7-a03a5386f535",
"created": "2026-03-03T13:18:40.613Z",
"modified": "2026-03-03T13:18:40.613Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'annaleec21.com']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.613Z",
"labels": [
"malicious-activity"
],
"confidence": 75
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--2b8a7145-1df2-4bf3-b22a-ccb4ff871fb8",
"created": "2026-03-03T13:18:40.613Z",
"modified": "2026-03-03T13:18:40.613Z",
"relationship_type": "based-on",
"source_ref": "indicator--fb1f897e-35b8-4892-9ff7-a03a5386f535",
"target_ref": "domain-name--1463f160-5d0b-42e5-ab58-a9e14dd14208"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--284d88b3-b9f5-4983-a67d-b2458cc7ce42",
"created": "2026-03-03T13:18:40.628Z",
"modified": "2026-03-03T13:18:40.628Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'availity4u.com']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.628Z",
"labels": [
"malicious-activity"
],
"confidence": 75
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--80f80095-0357-4963-8b1e-e85d310c6e2e",
"created": "2026-03-03T13:18:40.628Z",
"modified": "2026-03-03T13:18:40.628Z",
"relationship_type": "based-on",
"source_ref": "indicator--284d88b3-b9f5-4983-a67d-b2458cc7ce42",
"target_ref": "domain-name--fba5bdca-2fd9-48f6-ae3d-de539a1fc603"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--f4691487-93d9-4694-8219-a389da1dbf4d",
"created": "2026-03-03T13:18:40.645Z",
"modified": "2026-03-03T13:18:40.645Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'amstyle.fashion']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.645Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--804988f7-5cde-42b9-bd6e-81def38e6ce1",
"created": "2026-03-03T13:18:40.645Z",
"modified": "2026-03-03T13:18:40.645Z",
"relationship_type": "based-on",
"source_ref": "indicator--f4691487-93d9-4694-8219-a389da1dbf4d",
"target_ref": "domain-name--32c6c3a3-3215-437b-a9ef-bd72e1bbf205"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--4bfe0c88-67c5-4097-aea1-c42821331443",
"created": "2026-03-03T13:18:40.668Z",
"modified": "2026-03-03T13:18:40.668Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'essaypropromo.top']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.668Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--ba55d46d-87a2-498f-802c-74e864c2359d",
"created": "2026-03-03T13:18:40.668Z",
"modified": "2026-03-03T13:18:40.668Z",
"relationship_type": "based-on",
"source_ref": "indicator--4bfe0c88-67c5-4097-aea1-c42821331443",
"target_ref": "domain-name--047d160d-3a12-448b-afda-ca133ad178ae"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--f4956e3e-bafa-4f63-b845-6c2571c752d5",
"created": "2026-03-03T13:18:40.688Z",
"modified": "2026-03-03T13:18:40.688Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'fodi-social.store']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.688Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--4cd3cfe2-f321-4e40-8605-046c24dd1b9e",
"created": "2026-03-03T13:18:40.688Z",
"modified": "2026-03-03T13:18:40.688Z",
"relationship_type": "based-on",
"source_ref": "indicator--f4956e3e-bafa-4f63-b845-6c2571c752d5",
"target_ref": "domain-name--9510e736-9780-4c66-b443-ecdaef7bf8e1"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--1726c8ef-730d-437a-8771-fb63a8291de1",
"created": "2026-03-03T13:18:40.705Z",
"modified": "2026-03-03T13:18:40.705Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'g8t.me']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.705Z",
"labels": [
"malicious-activity"
],
"confidence": 75
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--b55e118e-1454-4283-9c79-4b3756a1640b",
"created": "2026-03-03T13:18:40.705Z",
"modified": "2026-03-03T13:18:40.705Z",
"relationship_type": "based-on",
"source_ref": "indicator--1726c8ef-730d-437a-8771-fb63a8291de1",
"target_ref": "domain-name--81f9814a-e8b6-44c1-bc14-59a10e69849c"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--ea981d7a-dd61-4884-b156-57d5df9f4ed5",
"created": "2026-03-03T13:18:40.724Z",
"modified": "2026-03-03T13:18:40.724Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'jasalivestreamingmurah.com']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.724Z",
"labels": [
"malicious-activity"
],
"confidence": 75
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--6610d955-3eac-40d5-8f0f-49b19fced624",
"created": "2026-03-03T13:18:40.724Z",
"modified": "2026-03-03T13:18:40.724Z",
"relationship_type": "based-on",
"source_ref": "indicator--ea981d7a-dd61-4884-b156-57d5df9f4ed5",
"target_ref": "domain-name--ce2b09a9-b789-4856-8fc6-35d3d0969d0d"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--d93ff187-ed15-4497-a15d-8d939573fd57",
"created": "2026-03-03T13:18:40.745Z",
"modified": "2026-03-03T13:18:40.745Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'litonali.com']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.745Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--07d18448-7fbc-4af5-a683-acfead418267",
"created": "2026-03-03T13:18:40.745Z",
"modified": "2026-03-03T13:18:40.745Z",
"relationship_type": "based-on",
"source_ref": "indicator--d93ff187-ed15-4497-a15d-8d939573fd57",
"target_ref": "domain-name--9f03cf30-ca60-4312-8f99-7dbe68130775"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--8c4cb30e-1224-4eaa-87d6-c19310815328",
"created": "2026-03-03T13:18:40.762Z",
"modified": "2026-03-03T13:18:40.762Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'mido-plus.store']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.762Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--20c27a71-58b6-4cb4-a142-8deb919690db",
"created": "2026-03-03T13:18:40.762Z",
"modified": "2026-03-03T13:18:40.762Z",
"relationship_type": "based-on",
"source_ref": "indicator--8c4cb30e-1224-4eaa-87d6-c19310815328",
"target_ref": "domain-name--8e3c1c98-21f7-4081-9ec1-e02808b973d7"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--bd7442a8-90c8-4510-ac37-b0a1bd210af0",
"created": "2026-03-03T13:18:40.779Z",
"modified": "2026-03-03T13:18:40.779Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'tbfs.xyz']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.779Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--c5e51201-af03-459b-8c49-95efa71da028",
"created": "2026-03-03T13:18:40.779Z",
"modified": "2026-03-03T13:18:40.779Z",
"relationship_type": "based-on",
"source_ref": "indicator--bd7442a8-90c8-4510-ac37-b0a1bd210af0",
"target_ref": "domain-name--6b74b08c-bacf-45ff-872a-ad50cdc4a6e8"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--fd2174fd-d87e-423e-ba59-9c38fd22f8ab",
"created": "2026-03-03T13:18:40.796Z",
"modified": "2026-03-03T13:18:40.796Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'yardbombsgone.com']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.796Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--afc277ac-7386-4485-8417-a4aa0c5d04f0",
"created": "2026-03-03T13:18:40.796Z",
"modified": "2026-03-03T13:18:40.796Z",
"relationship_type": "based-on",
"source_ref": "indicator--fd2174fd-d87e-423e-ba59-9c38fd22f8ab",
"target_ref": "domain-name--fadf82df-9659-4548-9870-b437d64042bd"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--eb7d6b05-b7ff-4066-8b0d-757028ec84cd",
"created": "2026-03-03T13:18:40.812Z",
"modified": "2026-03-03T13:18:40.812Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'zenrootfeet.life']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.812Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--463e8ff9-fec0-4a0a-b599-0ee1caac5b51",
"created": "2026-03-03T13:18:40.812Z",
"modified": "2026-03-03T13:18:40.812Z",
"relationship_type": "based-on",
"source_ref": "indicator--eb7d6b05-b7ff-4066-8b0d-757028ec84cd",
"target_ref": "domain-name--e1df7c16-91f6-4773-bf94-5883e5be7f87"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--92f4da5b-330c-4eaf-b0b5-84e269b6b3e2",
"created": "2026-03-03T13:18:40.828Z",
"modified": "2026-03-03T13:18:40.828Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'bhaktibhavna.space']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.828Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--315a0c0e-ca22-4b78-ab0e-376b7ed9f03a",
"created": "2026-03-03T13:18:40.828Z",
"modified": "2026-03-03T13:18:40.828Z",
"relationship_type": "based-on",
"source_ref": "indicator--92f4da5b-330c-4eaf-b0b5-84e269b6b3e2",
"target_ref": "domain-name--99be0ed9-b394-4a45-9835-8e3b613f0971"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--5b619e00-284a-4006-9867-821364ac7063",
"created": "2026-03-03T13:18:40.846Z",
"modified": "2026-03-03T13:18:40.846Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'cuneiform.ru']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.846Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--484ce8f5-2a7c-45b3-92a0-026704d3db70",
"created": "2026-03-03T13:18:40.846Z",
"modified": "2026-03-03T13:18:40.846Z",
"relationship_type": "based-on",
"source_ref": "indicator--5b619e00-284a-4006-9867-821364ac7063",
"target_ref": "domain-name--1ca123a5-4b46-4bcc-91a5-78d09abe9871"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--f06006c5-4bd7-4cc0-ac3a-8720948b8888",
"created": "2026-03-03T13:18:40.867Z",
"modified": "2026-03-03T13:18:40.867Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'escuelaastrouranianaydemisterios.org']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.867Z",
"labels": [
"malicious-activity"
],
"confidence": 75
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--0f62645f-4892-4527-90a4-9071e418a2ac",
"created": "2026-03-03T13:18:40.867Z",
"modified": "2026-03-03T13:18:40.867Z",
"relationship_type": "based-on",
"source_ref": "indicator--f06006c5-4bd7-4cc0-ac3a-8720948b8888",
"target_ref": "domain-name--a5790629-5ed2-48af-860d-17cd563869de"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--6b2b0bd9-0a75-4e82-b0a6-c8e6f5358c4d",
"created": "2026-03-03T13:18:40.884Z",
"modified": "2026-03-03T13:18:40.884Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'h9986.com']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.884Z",
"labels": [
"malicious-activity"
],
"confidence": 75
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--13152c0f-37c8-40b3-a5f6-b9d782cb4f1b",
"created": "2026-03-03T13:18:40.885Z",
"modified": "2026-03-03T13:18:40.885Z",
"relationship_type": "based-on",
"source_ref": "indicator--6b2b0bd9-0a75-4e82-b0a6-c8e6f5358c4d",
"target_ref": "domain-name--73c50bdb-d258-4152-bb43-351fe13d7f1d"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--72239e40-c07c-4064-a7a3-0e9a9344f6b9",
"created": "2026-03-03T13:18:40.901Z",
"modified": "2026-03-03T13:18:40.901Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'houseofkings.online']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.901Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--c423cc51-be01-4cc5-b1eb-cd14360f44dd",
"created": "2026-03-03T13:18:40.901Z",
"modified": "2026-03-03T13:18:40.901Z",
"relationship_type": "based-on",
"source_ref": "indicator--72239e40-c07c-4064-a7a3-0e9a9344f6b9",
"target_ref": "domain-name--7515c5f6-1d63-4735-8ead-72bc2a47b299"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--ea4ce053-230f-4a84-bc51-b426a6c152b8",
"created": "2026-03-03T13:18:40.922Z",
"modified": "2026-03-03T13:18:40.922Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'quedecositas.com']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.922Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--97f17f6c-9f5f-45c3-b13f-f07a962537dd",
"created": "2026-03-03T13:18:40.922Z",
"modified": "2026-03-03T13:18:40.922Z",
"relationship_type": "based-on",
"source_ref": "indicator--ea4ce053-230f-4a84-bc51-b426a6c152b8",
"target_ref": "domain-name--52c1e65e-56b3-4c4e-87c5-d5e81f7e2fbb"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--4b6ccb6d-1213-4b77-be91-26e65cd2a90d",
"created": "2026-03-03T13:18:40.941Z",
"modified": "2026-03-03T13:18:40.941Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'techiq.xyz']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.941Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--5adc1e0d-1033-4946-b3d6-b2ecd1d3d775",
"created": "2026-03-03T13:18:40.941Z",
"modified": "2026-03-03T13:18:40.941Z",
"relationship_type": "based-on",
"source_ref": "indicator--4b6ccb6d-1213-4b77-be91-26e65cd2a90d",
"target_ref": "domain-name--91801439-6f5f-4c0a-9d41-020ae94ae5e3"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--1f4da9e3-a0cb-4338-b891-dcd33cc9bd52",
"created": "2026-03-03T13:18:40.958Z",
"modified": "2026-03-03T13:18:40.958Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'wilbursoot.store']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.958Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--0e693a1e-a0f6-48df-ae79-27b924c3e549",
"created": "2026-03-03T13:18:40.958Z",
"modified": "2026-03-03T13:18:40.958Z",
"relationship_type": "based-on",
"source_ref": "indicator--1f4da9e3-a0cb-4338-b891-dcd33cc9bd52",
"target_ref": "domain-name--f6566940-1e9f-49f1-b461-a4e944eddbc1"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--9bb1e6b5-c55f-4c5e-addc-ea27a895f1a9",
"created": "2026-03-03T13:18:40.993Z",
"modified": "2026-03-03T13:18:40.993Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'wiredtech-ux-demo2.online']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:40.993Z",
"labels": [
"malicious-activity"
],
"confidence": 80
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--9946b693-d7ce-49b1-9ffe-14680436701b",
"created": "2026-03-03T13:18:40.993Z",
"modified": "2026-03-03T13:18:40.993Z",
"relationship_type": "based-on",
"source_ref": "indicator--9bb1e6b5-c55f-4c5e-addc-ea27a895f1a9",
"target_ref": "domain-name--34472b52-8a12-40e6-9c5b-3b8eb7ceb062"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--d1f01337-6971-4638-9607-d8d160338f8f",
"created": "2026-03-03T13:18:41.030Z",
"modified": "2026-03-03T13:18:41.030Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'youtubethumbnaildownloader.tech']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:41.030Z",
"labels": [
"malicious-activity"
],
"confidence": 75
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--eb0978bf-97a7-4e91-b00e-e9c0de63bfbc",
"created": "2026-03-03T13:18:41.030Z",
"modified": "2026-03-03T13:18:41.030Z",
"relationship_type": "based-on",
"source_ref": "indicator--d1f01337-6971-4638-9607-d8d160338f8f",
"target_ref": "domain-name--084d8805-7049-46df-a09e-0e52d8061142"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--e68cf356-bc75-46c4-8671-20537dbfa38e",
"created": "2026-03-03T13:18:41.056Z",
"modified": "2026-03-03T13:18:41.056Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = '0000111.xyz']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:41.056Z",
"labels": [
"malicious-activity"
],
"confidence": 75
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--017ce478-3322-4cc3-9019-9719b1b2c9e6",
"created": "2026-03-03T13:18:41.056Z",
"modified": "2026-03-03T13:18:41.056Z",
"relationship_type": "based-on",
"source_ref": "indicator--e68cf356-bc75-46c4-8671-20537dbfa38e",
"target_ref": "domain-name--7d0d55dc-3ec0-4922-bd45-5d0e9942970d"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--0df52944-98d7-4797-bdf8-0b5f1401cae1",
"created": "2026-03-03T13:18:41.077Z",
"modified": "2026-03-03T13:18:41.077Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = '00dd22495661v772c.christmas']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:41.077Z",
"labels": [
"malicious-activity"
],
"confidence": 80
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--65f96cf1-610b-4a2e-82ea-df5059a1e51d",
"created": "2026-03-03T13:18:41.077Z",
"modified": "2026-03-03T13:18:41.077Z",
"relationship_type": "based-on",
"source_ref": "indicator--0df52944-98d7-4797-bdf8-0b5f1401cae1",
"target_ref": "domain-name--eee93bdb-54df-48ed-8e2b-2e15dafc96ed"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--47405e88-3e95-4fe5-aa5d-acaa808a6c10",
"created": "2026-03-03T13:18:41.099Z",
"modified": "2026-03-03T13:18:41.099Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = '007win.link']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:41.099Z",
"labels": [
"malicious-activity"
],
"confidence": 75
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--3beedc2e-d6f9-48d3-9fe6-285e398ecdba",
"created": "2026-03-03T13:18:41.099Z",
"modified": "2026-03-03T13:18:41.099Z",
"relationship_type": "based-on",
"source_ref": "indicator--47405e88-3e95-4fe5-aa5d-acaa808a6c10",
"target_ref": "domain-name--377a5aa6-6c5c-4d0e-911f-22f754173ac2"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--51e3a48b-b127-4ec6-967e-7be0f7c45795",
"created": "2026-03-03T13:18:41.126Z",
"modified": "2026-03-03T13:18:41.126Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = '010.one']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:41.126Z",
"labels": [
"malicious-activity"
],
"confidence": 75
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--acf641db-eedd-4f41-97b4-3b7f5e8a3e08",
"created": "2026-03-03T13:18:41.126Z",
"modified": "2026-03-03T13:18:41.126Z",
"relationship_type": "based-on",
"source_ref": "indicator--51e3a48b-b127-4ec6-967e-7be0f7c45795",
"target_ref": "domain-name--0789a611-43db-4db3-bd5a-fadda8a8bfd4"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--bd811f8e-5747-4ab1-9b16-9f9b93529932",
"created": "2026-03-03T13:18:41.150Z",
"modified": "2026-03-03T13:18:41.150Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = '010097.bond']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:41.150Z",
"labels": [
"malicious-activity"
],
"confidence": 75
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--b0471ff2-aebf-492d-8e3a-70aacce9daf5",
"created": "2026-03-03T13:18:41.150Z",
"modified": "2026-03-03T13:18:41.150Z",
"relationship_type": "based-on",
"source_ref": "indicator--bd811f8e-5747-4ab1-9b16-9f9b93529932",
"target_ref": "domain-name--f1458a07-eb03-4011-bc12-fef35de0a236"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--0f2c18b3-4d33-4c54-ba28-af049574d639",
"created": "2026-03-03T13:18:41.170Z",
"modified": "2026-03-03T13:18:41.170Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = '010417712.email']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:41.170Z",
"labels": [
"malicious-activity"
],
"confidence": 75
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--30f6e695-1164-493e-a135-13ad67c46083",
"created": "2026-03-03T13:18:41.170Z",
"modified": "2026-03-03T13:18:41.170Z",
"relationship_type": "based-on",
"source_ref": "indicator--0f2c18b3-4d33-4c54-ba28-af049574d639",
"target_ref": "domain-name--d0dc6777-abc9-4942-a0ed-8a388fecffad"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--fd34ef28-c9ed-4e35-8fe2-abddaf316cc2",
"created": "2026-03-03T13:18:41.190Z",
"modified": "2026-03-03T13:18:41.190Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = '01044323111.click']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:41.190Z",
"labels": [
"malicious-activity"
],
"confidence": 75
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--5e860103-b1fd-4a4f-9e5e-1e24ba406d98",
"created": "2026-03-03T13:18:41.190Z",
"modified": "2026-03-03T13:18:41.190Z",
"relationship_type": "based-on",
"source_ref": "indicator--fd34ef28-c9ed-4e35-8fe2-abddaf316cc2",
"target_ref": "domain-name--d39fed4a-1a9b-4a65-8d3b-168ba4d08906"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--dd096dac-5722-4bc4-aab7-77c96b22f9f1",
"created": "2026-03-03T13:18:41.210Z",
"modified": "2026-03-03T13:18:41.210Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = '012226.com']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:41.210Z",
"labels": [
"malicious-activity"
],
"confidence": 75
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--6e8a9677-b00d-4a9a-a422-49f5bbf07a33",
"created": "2026-03-03T13:18:41.210Z",
"modified": "2026-03-03T13:18:41.211Z",
"relationship_type": "based-on",
"source_ref": "indicator--dd096dac-5722-4bc4-aab7-77c96b22f9f1",
"target_ref": "domain-name--ce131e1b-99e6-4331-97a1-8e85b7373bc5"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--efb86c98-0419-4f31-b167-d0a4201a11c3",
"created": "2026-03-03T13:18:41.232Z",
"modified": "2026-03-03T13:18:41.232Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = '017805.com']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:41.232Z",
"labels": [
"malicious-activity"
],
"confidence": 75
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--348aa556-257f-4fbf-9fd8-67b350596094",
"created": "2026-03-03T13:18:41.232Z",
"modified": "2026-03-03T13:18:41.232Z",
"relationship_type": "based-on",
"source_ref": "indicator--efb86c98-0419-4f31-b167-d0a4201a11c3",
"target_ref": "domain-name--0676c51a-6c9f-402e-b1ee-a958cca194b4"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--d5623781-1270-495e-ba47-6c21281b7973",
"created": "2026-03-03T13:18:41.248Z",
"modified": "2026-03-03T13:18:41.248Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = '030129.com']",
"pattern_type": "stix",
"valid_from": "2026-03-03T13:18:41.248Z",
"labels": [
"malicious-activity"
],
"confidence": 75
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--bb423dd6-c94e-44d4-a959-3e9d9c9f4baf",
"created": "2026-03-03T13:18:41.248Z",
"modified": "2026-03-03T13:18:41.248Z",
"relationship_type": "based-on",
"source_ref": "indicator--d5623781-1270-495e-ba47-6c21281b7973",
"target_ref": "domain-name--352511e3-0ead-43af-acde-18e497fbfe2c"
}
]
}