Heroes, here's info your security rundown for Jan 15, 2026.
Critical Threats
Palo Alto Networks has patched a high-severity vulnerability in GlobalProtect Gateway and Portal that allows unauthenticated attackers to crash the service. A proof-of-concept exploit exists, making immediate exploitation highly likely for exposed interfaces.
Business Impact
A successful attack results in a Denial of Service (DoS), severing VPN access for remote employees and potentially disrupting business continuity. While data theft is not the primary risk, operational downtime for remote workforces could be significant.
Recommended Action
Ask your IT team: "Have we applied the latest PAN-OS updates to our GlobalProtect Gateways, specifically addressing CVE-2026-0227?"
High Severity
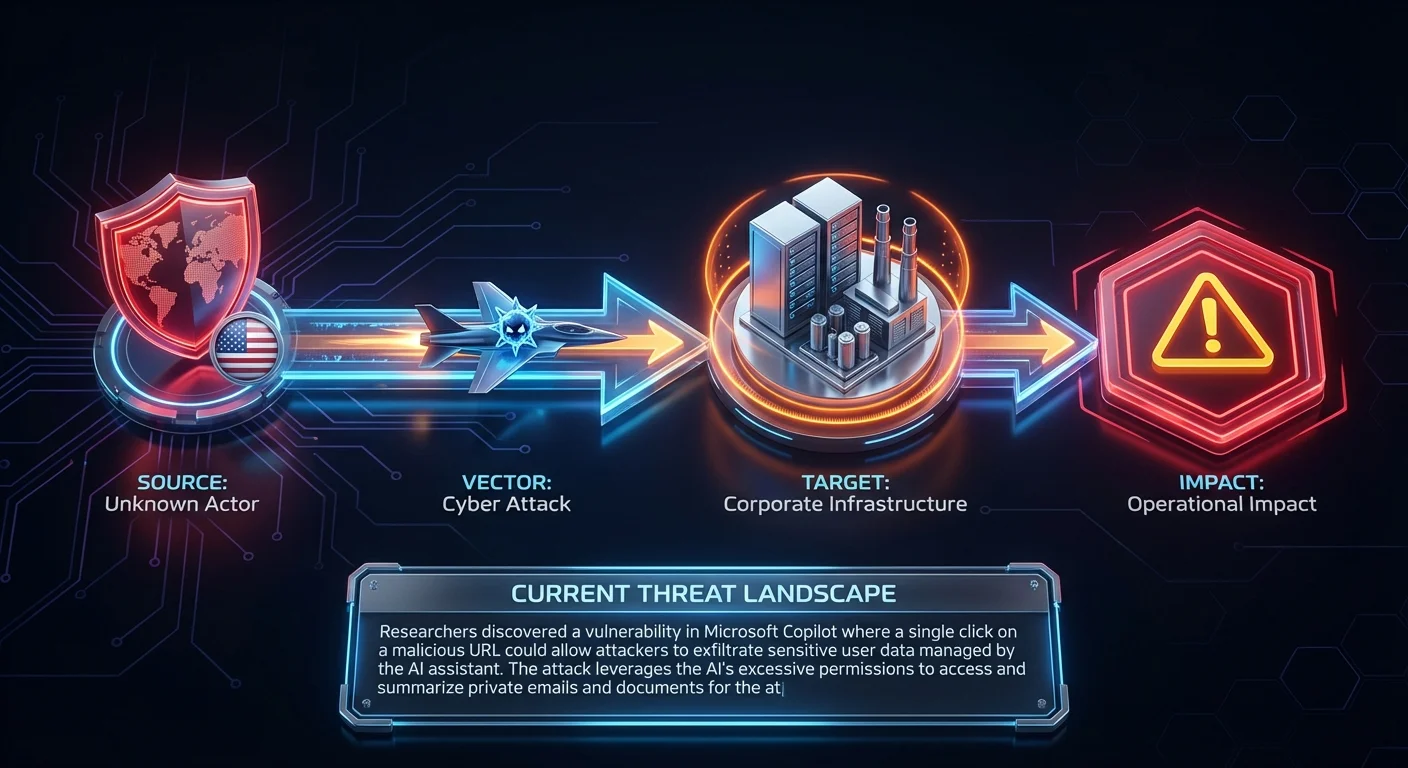
Researchers discovered a vulnerability in Microsoft Copilot where a single click on a malicious URL could allow attackers to exfiltrate sensitive user data managed by the AI assistant. The attack leverages the AI's excessive permissions to access and summarize private emails and documents for the attacker.
Business Impact
This exposes organizations to massive data leakage of intellectual property and internal communications. If an executive clicks a lure, the AI could inadvertently package and send confidential strategy documents to an external adversary.
Recommended Action
Verify with your security team: "Do we have Data Security Posture Management (DSPM) controls in place to limit what data Copilot can access, and has the Microsoft fix been verified in our tenant?"
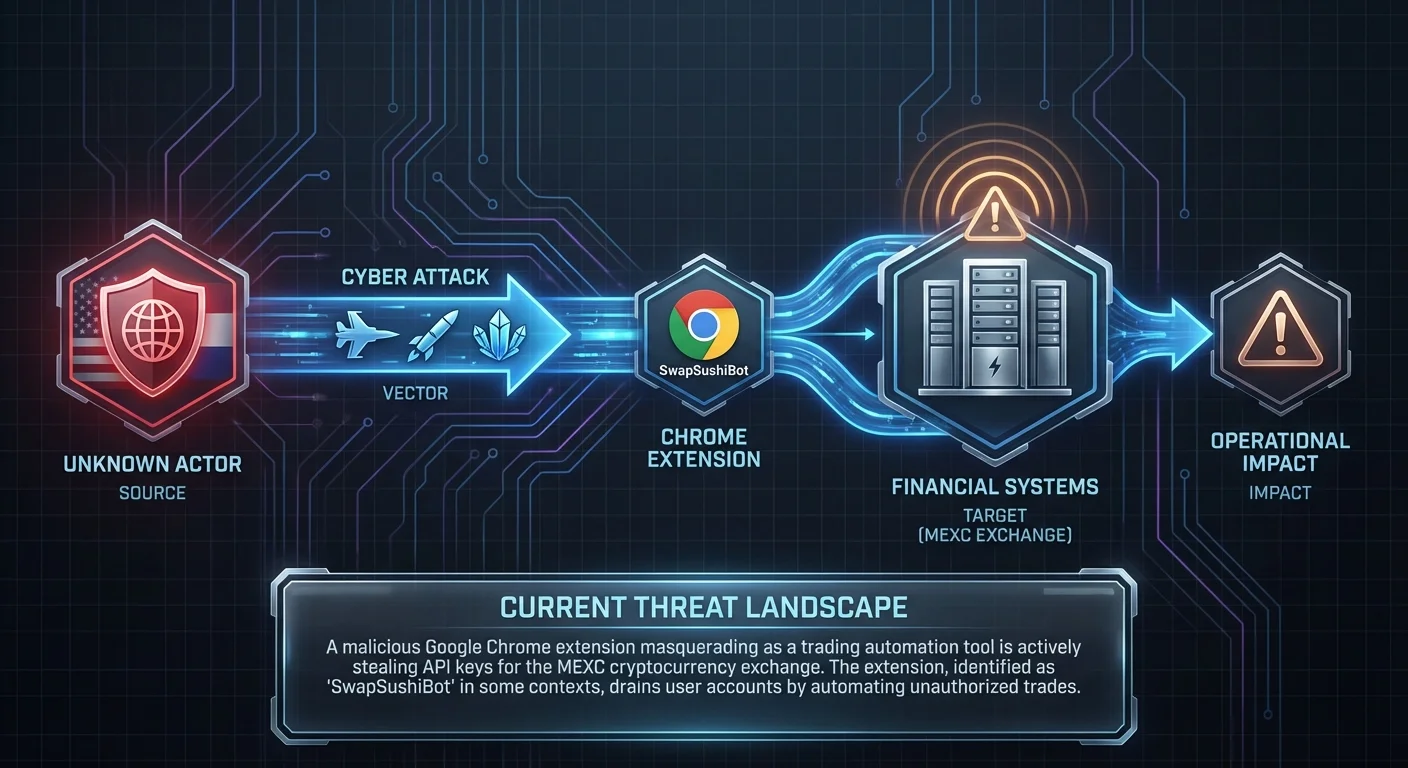
A malicious Google Chrome extension masquerading as a trading automation tool is actively stealing API keys for the MEXC cryptocurrency exchange. The extension, identified as "SwapSushiBot" in some contexts, drains user accounts by automating unauthorized trades.
Business Impact
For financial organizations or employees managing corporate crypto assets, this represents a direct financial loss risk. It also highlights the danger of unmanaged browser extensions in the enterprise environment.
Recommended Action
Ask IT: "Do we enforce a blocklist for browser extensions, and can we scan endpoints for the presence of unauthorized trading tools?"
New analysis reveals that Predator spyware has advanced capabilities to detect when it is being analyzed by researchers and can troubleshoot its own failed infection attempts. This makes detection and analysis significantly harder for defense teams.
Business Impact
High-value targets (executives, R&D leads) are at increased risk of undetectable mobile espionage. Compromise could lead to the theft of sensitive conversations, location data, and trade secrets without the victim's knowledge.
Recommended Action
Review mobile device management (MDM) policies for executive devices and consider specialized mobile threat defense solutions for high-risk personnel.
Other Noteworthy
New analysis reveals that Predator spyware has advanced capabilities to detect when it is being analyzed by researchers and can troubleshoot its own failed infection attempts. This makes detection and analysis significantly harder for defense teams.
Business Impact
High-value targets (executives, R&D leads) are at increased risk of undetectable mobile espionage. Compromise could lead to the theft of sensitive conversations, location data, and trade secrets without the victim's knowledge.
Recommended Action
Review mobile device management (MDM) policies for executive devices and consider specialized mobile threat defense solutions for high-risk personnel.
Vendor Spotlight
Specialization: Browser Security and Secure Access Service Edge (SASE)
Why Menlo Security Today: Menlo Security is directly relevant to the threat involving the malicious Chrome extension, as their browser security platform specifically detects and blocks malicious extensions and prevents credential theft. Furthermore, their Remote Browser Isolation (RBI) technology neutralizes risks associated with clicking malicious URLs, such as the vector described in the Microsoft Copilot attack.
Key Capability: Remote Browser Isolation (RBI) to neutralize browser-based threats and extension risks
Recommended Actions: 1. Navigate to Menlo Security Admin Console → Policy → Browser Security → Extension Policy 2. Navigate to Menlo Security Admin Console → Policy → Web Policy → Security 3. Navigate to Menlo Security Admin Console → Policy → Web Policy → Content & File Controls → Input Controls
Verification Steps: - Attempt to install a test extension not on the Allow List or visit a site hosting the blocked extension ID - Navigate to a test site categorized as 'Uncategorized' (or use safe.menlosecurity.com/isolate)