Heroes, late breaking critical news. Here's a detailed look at the current cybersecurity landscape for December 19, 2025.
Critical Threats
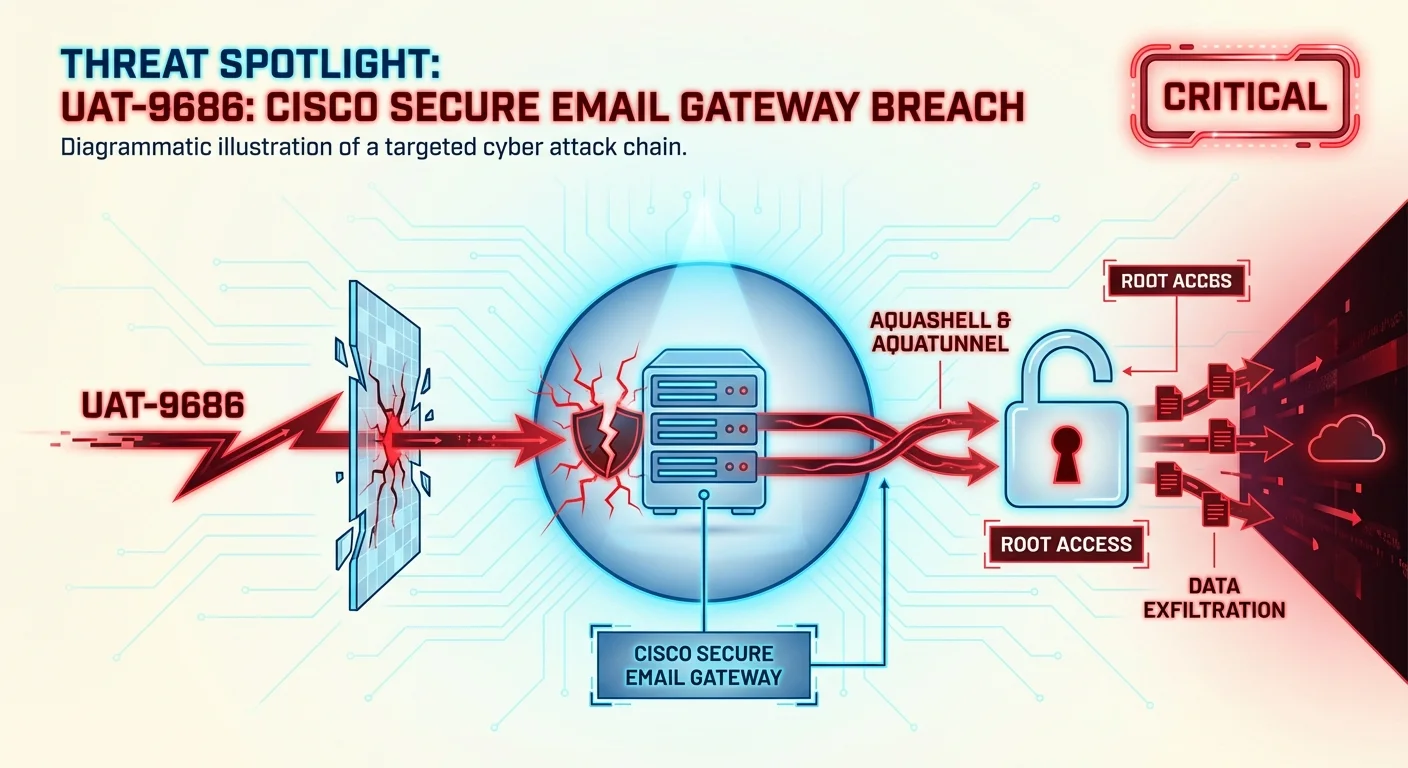
Cisco Secure Email Gateway Zero-Day Exploited by China-Linked Group
Security Affairs·8:53 AM·CVE-2025-20393
▾
Cisco has confirmed a critical zero-day vulnerability in its Secure Email Gateway and Web Manager is being actively exploited by a China-linked threat group known as UAT-9686. The attackers are deploying sophisticated malware, including AquaShell and AquaTunnel, to maintain persistence and exfiltrate data.
Business Impact
This vulnerability allows attackers to bypass authentication and gain root access to email infrastructure. If exploited, organizations face total compromise of email communications, theft of sensitive corporate data, and potential lateral movement into the broader network, leading to severe regulatory penalties under SOX and reputational ruin.
Recommended Action
Ask your IT team: "Have we verified if our Cisco Secure Email Gateways are running vulnerable firmware, and have we scanned for the specific 'AquaShell' indicators of compromise released by Cisco?"
Hewlett Packard Enterprise (HPE) has issued a patch for a critical vulnerability in its OneView infrastructure management software that carries a maximum CVSS score of 10.0. This flaw allows remote attackers to execute arbitrary code without authentication.
Business Impact
OneView is often used to manage physical servers and virtualization infrastructure; a compromise here effectively hands over the keys to the data center. This could result in total operational shutdown, unauthorized manipulation of hardware, and massive data breaches affecting all hosted applications.
Recommended Action
Ask your Infrastructure team: "Is our HPE OneView instance exposed to the network, and has the critical patch for CVE-2025-37164 been applied immediately?"
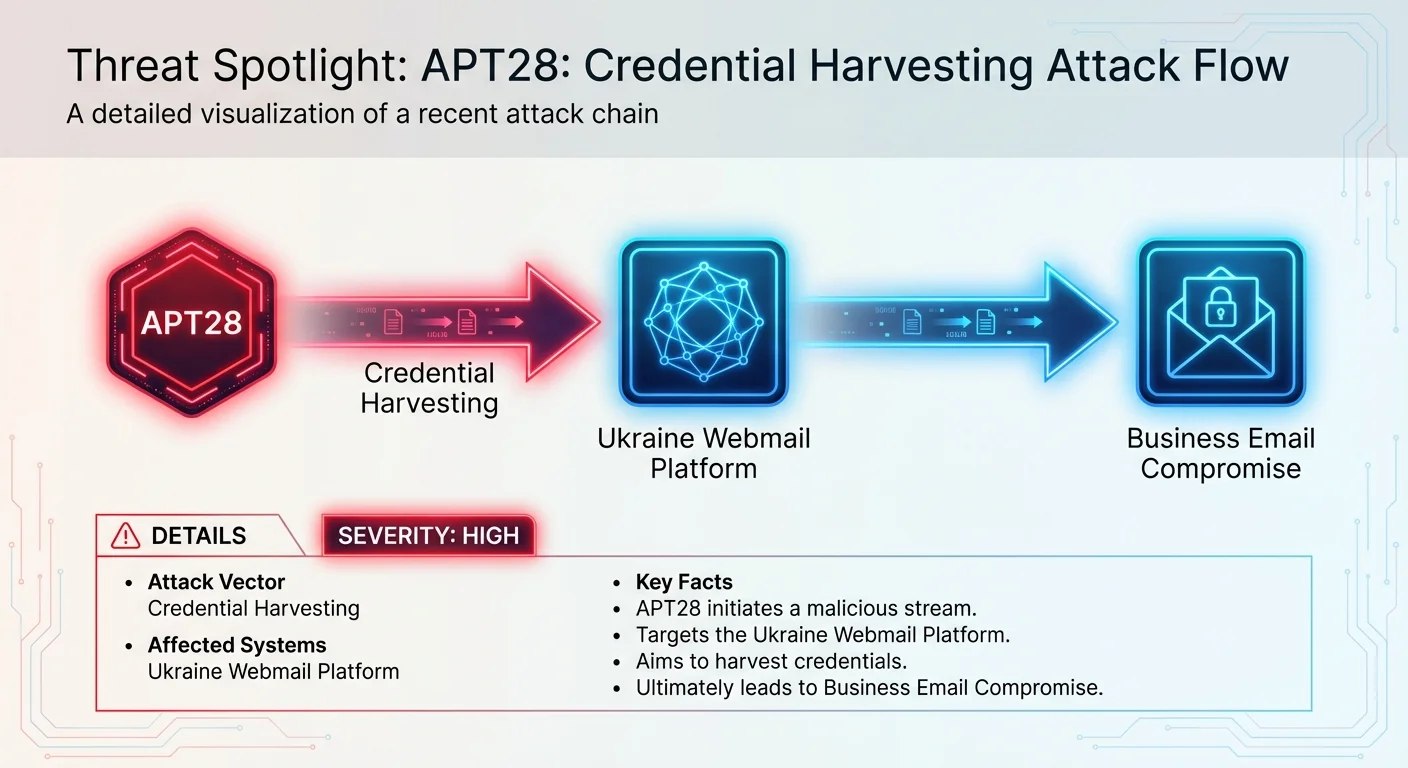
Russian military intelligence (APT28) is actively targeting the widely used ukr.net webmail platform with credential-harvesting campaigns. This activity highlights the persistent blurring of lines between military and civilian targets in cyber espionage operations.
Business Impact
While focused on Ukraine, APT28 campaigns often spill over or target global organizations with ties to the region. Successful credential theft can lead to business email compromise (BEC) and unauthorized access to partner networks.
Recommended Action
Ask your Security Operations team: "Have we updated our threat intelligence feeds to include the latest APT28 indicators, specifically those related to webmail credential harvesting?"
Security researchers have identified new Distributed Component Object Model (DCOM) objects that attackers can use for lateral movement within Windows networks. This technique allows adversaries to move stealthily between systems using legitimate administrative protocols.
Business Impact
Lateral movement is a critical phase in ransomware and espionage attacks; if attackers can move undetected using DCOM, they can escalate privileges and access sensitive data repositories without triggering standard alarms.
Recommended Action
Ask your SOC team: "Do we monitor for abnormal DCOM instantiation events, and can we detect the specific DCOM objects identified in this new research?"
India Criminalizes Tampering with Telecommunication Identifiers
Cyble·8:15 AM
▾
The Indian government has introduced the Telecommunications Act, which criminalizes the tampering of telecommunication identifiers and unauthorized radio equipment. This legal shift impacts how organizations manage mobile devices and telecommunications hardware in the region.
Business Impact
Companies operating in India must ensure strict compliance with hardware identity regulations. Non-compliance could result in legal action and the seizure of unauthorized or modified telecommunications equipment.
Recommended Action
Ask your Legal and Compliance teams: "Does our mobile device management policy in India comply with the new Telecommunications Act regarding device identifiers?"
TruffleNet and Cloud Abuse: Identity Architecture Failure
Defakto Security·6:03 PM
▾
The TruffleNet campaign demonstrates how attackers are exploiting identity models rather than zero-day vulnerabilities to abuse cloud environments at scale. This highlights a fundamental failure in how identity architectures handle automation and scale.
TruffleNet and Cloud Abuse: Identity Architecture Failure
Defakto Security·6:03 PM
▾
The TruffleNet campaign demonstrates how attackers are exploiting identity models rather than zero-day vulnerabilities to abuse cloud environments at scale. This highlights a fundamental failure in how identity architectures handle automation and scale.
Reports indicate a rise in AI tools being leveraged for cyber attacks, including an incident where Chinese hackers jailbroke Anthropic's Claude model. This trend is forcing policymakers and executives to reconsider the security implications of AI integration and the potential for AI-augmented offensive operations.
Spotlight Rationale: Selected for relevance to CVE-2025-20393 (Cisco Zero-Day) and APT28 activity, where attackers use legitimate credentials and "living off the land" techniques (like DCOM abuse) that bypass traditional signature detection.
Seceon's approach to Behavioral Threat Analytics is critical for detecting the post-exploitation activities described in today's intelligence, such as the deployment of AquaShell or lateral movement via DCOM objects. Unlike traditional tools that look for known malware signatures, Seceon analyzes the behavior of credentials and system functions to identify when legitimate tools are being abused by actors like UAT-9686.
Actionable Platform Guidance: Administrators should configure Seceon to alert on anomalous process execution chains involving `admin/shell` URI patterns (associated with the Cisco exploit) and unusual DCOM instantiation from non-admin accounts.
⚠️ Disclaimer: Test all detection logic in non-production environments before deployment.
1. Vendor Platform Configuration - Seceon
# Configuration Concept for Behavioral Alerting
# 1. Access the Seceon OTM Dashboard
# 2. Navigate to "Policy Management" > "Behavioral Rules"
# 3. Create a new "Process Anomaly" rule targeting the indicators from UAT-9686
Rule_Name: "Suspicious_Gateway_Activity"
Target_Scope: "Email_Gateways"
Trigger_Condition:
Process_Name CONTAINS "AquaShell" OR
Process_Name CONTAINS "AquaTunnel" OR
Network_Connection TO "206.237.3.150"
Action: "Immediate_Quarantine" AND "Notify_SOC"
index=security sourcetype="cisco:esa:http"
(uri_path="*/admin/shell*" OR src_ip="206.237.3.150" OR src_ip="45.77.33.136" OR src_ip="143.198.92.82")
| eval risk_score=case(
uri_path LIKE "%/admin/shell%", 100,
src_ip=="206.237.3.150", 100,
1==1, 50)
| where risk_score >= 50
| table _time, src_ip, dest_ip, uri_path, user_agent, risk_score
| sort -_time
4. PowerShell Script — Check for Suspicious DCOM Instantiation
$computers = "localhost", "SERVER01", "WKSTN01"
foreach ($computer in $computers) {
if (Test-Connection -ComputerName $computer -Count 1 -Quiet) {
# Checks for recent DCOM errors or unusual instantiations in System logs
Get-WinEvent -ComputerName $computer -LogName System -FilterXPath "*[System[(EventID=10009 or EventID=10016)]]" -MaxEvents 20 |
Select-Object TimeCreated, MachineName, Id, Message |
Where-Object { $_.Message -like "*React2Shell*" -or $_.Message -like "*Jackpot*" }
Write-Host "Checked $computer for DCOM anomalies..."
}
}
This rundown should provide a solid overview of the current threat landscape. Thank you to all our cyberheroes for your diligence and hard work. Stay vigilant!
Cookie Notice
We use essential cookies to provide our cybersecurity newsletter service and analytics cookies to improve your experience.
About STIX 2.1: Structured Threat Information eXpression (STIX) is the machine language of cybersecurity. This bundle contains validated threat objects, indicators, and relationships that can be directly imported into your SIEM, TIP, or security orchestration platform.
Usage: Download or copy the JSON below and import it directly into your threat intelligence platform, SIEM, or security orchestration tools for automated threat detection and response.
{
"type": "bundle",
"id": "bundle--ba2a0bce-8d87-453f-82b5-f8cc1cf6ee3c",
"objects": [
{
"type": "marking-definition",
"spec_version": "2.1",
"id": "marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487",
"created": "2022-10-01T00:00:00.000Z",
"definition_type": "tlp:2.0",
"name": "TLP:CLEAR",
"definition": {
"tlp": "clear"
}
},
{
"type": "identity",
"spec_version": "2.1",
"id": "identity--514347c8-67f5-4a12-bc21-93cd97e1aee6",
"created": "2025-12-19T10:27:47.599Z",
"modified": "2025-12-19T10:27:47.599Z",
"name": "MikeGPT Intelligence Platform",
"description": "AI-powered threat intelligence collection and analysis platform providing automated cybersecurity intelligence feeds",
"identity_class": "organization",
"sectors": [
"technology",
"defense"
],
"contact_information": "Website: https://mikegptai.com | Email: intel@mikegptai.com",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"type": "report",
"spec_version": "2.1",
"id": "report--5104dd28-78fc-4473-8271-b14238836c7b",
"created": "2025-12-19T10:27:47.599Z",
"modified": "2025-12-19T10:27:47.599Z",
"name": "Threat Intelligence Report - 2025-12-19",
"description": "Threat Intelligence Report - 2025-12-19\n\nThis report consolidates actionable cybersecurity intelligence from 90 sources, processed through automated threat analysis and relationship extraction.\n\nKEY FINDINGS:\n• China-linked APT UAT-9686 is targeting Cisco Secure Email Gateway and Secure Email and Web Manager (Score: 100)\n• India Criminalizes Tampering with Telecommunication Identifiers and Unauthorized Radio Equipment Und (Score: 100)\n• Chinese Hackers Exploited a Zero-Day in Cisco Email Security Systems (Score: 100)\n• Policymakers grapple with fallout from Chinese AI-enabled hack (Score: 100)\n• Cisco customers hit by fresh wave of zero-day attacks from China-linked APT (Score: 100)\n\nEXTRACTED ENTITIES:\n• 31 Attack Pattern(s)\n• 8 Domain Name(s)\n• 19 File:Hashes.Sha 256(s)\n• 8 Indicator(s)\n• 2 Malware(s)\n• 1 Marking Definition(s)\n• 102 Relationship(s)\n• 1 Threat Actor(s)\n• 3 Vulnerability(s)\n\nCONFIDENCE ASSESSMENT:\nVariable confidence scoring applied based on entity type and intelligence source reliability. Confidence ranges from 30-95% reflecting professional intelligence assessment practices.\n\nGENERATION METADATA:\n- Processing Time: Automated\n- Validation: Three-LLM consensus committee\n- Standards Compliance: STIX 2.1\n",
"published": "2025-12-19T10:27:47.599Z",
"object_refs": [
"identity--514347c8-67f5-4a12-bc21-93cd97e1aee6",
"vulnerability--4b1b7578-644c-4cee-b209-befc0c385a80",
"vulnerability--773c21cf-7a9e-4746-b0ab-233a26535983",
"identity--6741006f-839c-40a5-9d6e-5c3499671c57",
"identity--e26e77aa-e035-4161-896a-eaad198d10a2",
"identity--4554385d-4839-478d-9228-aec70dce023e",
"identity--d656b75c-7852-4c6e-b421-a822d7664ae7",
"identity--2f0057c3-d3b9-45b0-ba92-0b88105c0ccb",
"malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"identity--c4bddfde-bffe-4aa3-970b-dd430d1877f3",
"identity--3e5eaf0a-42ab-4555-801b-e588368e21a2",
"identity--6e5f0b1c-6b68-4827-ac00-d36acd639e2b",
"identity--1908b54a-478b-4cab-a870-6741a700fb2a",
"identity--afa5a316-655a-43a9-b3f1-2a1d39c0ac1a",
"identity--b0cec87f-da35-4d9b-b1e6-e530898b873e",
"identity--689177a2-02f4-4be0-96a5-89b091102848",
"identity--3db79e9a-7407-4b26-a2c6-49e924dacb76",
"identity--96807dc1-31b6-428e-a217-2144d8041bee",
"identity--9602c33d-5759-40f1-83ac-74cf4aed6790",
"identity--9fd3cdf1-bb5e-4d25-9ca9-6737a061ca7d",
"threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"vulnerability--be8b8bda-4bd8-477b-9f78-f01bd36be940",
"malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"attack-pattern--c99b8707-1226-4372-9f66-73b5d45b3f78",
"attack-pattern--f826e543-c895-41dc-bac3-389ef1a14778",
"attack-pattern--d5f68c3e-3583-497a-8fd3-6fe32b38bf5f",
"attack-pattern--f3417ce4-850c-4b35-a8f0-944ebd1397de",
"attack-pattern--cdc4c019-787f-457c-a963-e55f4e804db8",
"attack-pattern--57e97f43-4323-4cb3-892a-5387d593f466",
"attack-pattern--f25aeb02-492b-4d84-ba74-953779e3c255",
"attack-pattern--84b7fc1e-6f1b-4dc6-9bcc-488b2727c7af",
"attack-pattern--aafb87d3-d5e3-44d3-9260-c41332dda176",
"attack-pattern--6ffaba66-d6ac-4af3-b4f3-8a5adabce2bb",
"attack-pattern--34e7763c-ff57-4a68-9e1e-ebf4113d5699",
"attack-pattern--d9b3d85d-2506-4f4c-acd0-adf1dd675840",
"attack-pattern--450c59da-4f5c-4b1e-9e76-08ee62cb4061",
"attack-pattern--4e848890-246a-47e8-8d6b-1f4ce8315437",
"attack-pattern--80cfb71e-1a21-4f1f-9daa-0992a988e675",
"attack-pattern--b059beaa-ec1b-4493-a498-29e7a2c111ef",
"attack-pattern--7f3ed782-2721-4672-8876-bb795e84c74b",
"attack-pattern--7563a09a-2674-4a21-b6de-1d23c25c7eb4",
"attack-pattern--9cf22a56-1e68-47e8-b38b-604b9e3f621d",
"attack-pattern--39e179f7-eb33-4dba-86f0-c13dbcbd2a1b",
"attack-pattern--2cf44576-4806-4da1-a645-8f620e826a63",
"attack-pattern--bb74e4d5-41a8-45dd-9977-108624360a65",
"attack-pattern--67804b3c-dd58-400e-a7a3-438e4d228585",
"attack-pattern--e57f3d8f-db5e-465c-9294-c7831e03227e",
"attack-pattern--5391a1ff-d556-4631-ba60-8905f720bf7f",
"attack-pattern--66e614e6-1ec5-41d9-ba44-34ed358d91aa",
"attack-pattern--cc16d880-ad7c-42bb-98e3-ec0ea5e864bf",
"attack-pattern--cc98d5fb-a57e-47af-845c-7805ee3a7946",
"attack-pattern--e3cf9026-e2ba-4bf8-bc6d-505c9c3fb86f",
"attack-pattern--9bd06311-fea2-4b5d-afa9-bcd1a11bdf8e",
"attack-pattern--54547eb0-ddb8-487e-8cf8-2daf078ef6b8",
"relationship--676e8af4-8080-4d57-90cb-9cac53f8ec1c",
"relationship--774e9ce1-32f1-498f-b68c-d2c4a27d7595",
"relationship--ce19f56d-995f-400e-a2d0-244d7866f6be",
"relationship--14cbdf03-a2fc-44a8-a4c8-1aa8b6ea70bf",
"relationship--b85642b3-68f8-4941-8694-60acc4b304be",
"relationship--d4efe09a-5c53-4415-9372-56027a45bf00",
"relationship--f2b9c318-e962-40f8-8245-86bd5e486f77",
"relationship--d6e06e73-36ca-475e-9d6d-24e9c5109a58",
"relationship--91a444ad-10a5-4711-be52-cb37c3bce6dd",
"relationship--e9f09f9c-7af3-4e81-8767-1310ad585d38",
"relationship--d1720a0c-e6fd-4a58-8abc-65387de9a205",
"relationship--50cbac6a-0dd2-4639-8e87-9c496c2f30fc",
"relationship--593c272a-2067-4077-afd4-4b43f56027a0",
"relationship--465304f6-8d8a-475d-a889-0017d60881ed",
"relationship--911cd783-4827-48b7-9381-5102a9a4342b",
"relationship--9303f511-cf62-4af4-8000-425182c3c1d8",
"relationship--dd0a17bf-21a2-4153-a801-eee070a05011",
"relationship--e7507dd9-731e-45da-ab15-881c5462677a",
"relationship--07a5807e-f8ce-41e6-aca0-b8103c0230e4",
"relationship--5f80552d-9dbc-4264-b734-87087fa1d7bc",
"relationship--c77ea9d5-5824-47af-897a-dddb73a3bd0d",
"relationship--2495c46a-24e6-436e-ba3a-2c51ee78eacd",
"relationship--2d552a7b-4871-41e2-bc6a-1144134d8c85",
"relationship--9b548df2-8004-4836-9ad6-73722591f690",
"relationship--35c44c96-eb1b-4dec-bb03-811eaf6ef1d1",
"relationship--4760d102-1dc2-4dd3-9693-b5c5206b9ce2",
"relationship--168e9032-3524-4092-9d94-1bf1ece1a6eb",
"relationship--f91bf561-92bf-48ab-b3f4-9729615aa938",
"relationship--41dea06e-2c4f-44c0-ac0f-3f0c848494b8",
"relationship--babbb1e6-aef1-473c-b8a9-e8582a4a1a45",
"relationship--141ac71b-fa93-48a4-b37e-f8d7df06709f",
"relationship--1c9181cb-2cc4-47d5-996f-d26001ebc817",
"relationship--d682a1ea-f8ec-4b4b-8e3c-9ab7903c7b56",
"relationship--2c9366ee-8a0c-4bb5-a993-d9d649d0f6b2",
"relationship--ba1e62c4-88ab-4e95-8f4b-8d22bf71074a",
"relationship--08b3ae91-8240-487d-8ac9-4600542be565",
"relationship--c3f278b2-5720-4b3d-a314-aba92be50fe0",
"relationship--0d4e0ea6-507c-4568-8cf3-cd2c3cf6e27f",
"relationship--4a91611f-4804-4ff5-804a-f10b61d12b6a",
"relationship--04f2b6c3-e705-4b43-8f1a-1cd75af68a7a",
"relationship--6687d57f-02c8-4169-94fa-56ca651b2dac",
"relationship--89c8a385-eb03-4aa3-a902-1b60072bf6eb",
"relationship--89c55b03-0d7c-40b6-b290-9a3a19000183",
"relationship--ebcb68c5-4005-4108-90a1-8073d3c59708",
"relationship--66ec9ffa-a19b-4314-88e8-82766cb18afb",
"relationship--33e7b161-6b15-44d0-8aad-aee549a3c704",
"relationship--5e81cebd-17d8-4d1d-be5b-2c3d72df884a",
"relationship--7bb43b14-09f4-4166-9039-0bff85fb1f58",
"relationship--9b8563b7-e377-4cf2-a207-041e51ec8745",
"relationship--e0057df3-4946-424c-8cfa-b69430bb05dc",
"relationship--baef7748-2f12-4e6b-a4ff-4b4600a41087",
"relationship--4d5f217d-fb1c-4e36-a817-60d03a78fa77",
"relationship--9a8723a8-aa68-45ab-9556-0a3f2b34e0d3",
"relationship--728864aa-d9a2-4d5f-9a3b-62137608d1a1",
"relationship--970eed47-10f6-4410-ae8d-de8a3ed279ab",
"relationship--f47714ce-96b4-437a-b41e-e3054265a27d",
"relationship--5ebf5b67-8da3-4bd9-85cc-3232a6f87e57",
"relationship--7bf80cd1-b744-470f-be58-5f635256a95a",
"relationship--bd8f20ad-679a-42b1-aa39-657d9fd145a3",
"relationship--d9a3eeaf-4c6d-4863-8068-39e5f078e235",
"relationship--c5ff5fcd-0128-4abb-b0e3-cd1e55934de6",
"relationship--5b8f0d31-be58-4e08-876f-6df47571c20a",
"relationship--db4f03ba-4373-40e1-9757-052fd1106fb8",
"relationship--054456b5-13c9-4b30-9ca5-72c7d97ba9d2",
"relationship--cbf3e059-77ea-44d6-83e4-3d69f641377e",
"relationship--c67e3652-3faf-4fc2-b2eb-0d2ff298af5a",
"relationship--42e8cc3d-0a0d-4d80-a4d2-447f11f771eb",
"relationship--f43c6ed1-e549-493b-bfe6-023ba68ef673",
"relationship--7f8b275d-5399-46ea-b0d0-df26f7c4aed2",
"relationship--613527f4-1ca3-420b-a2fe-7500d0e3ad1c",
"relationship--8f950711-2d13-4698-b9b4-293f52aef4c3",
"relationship--41d3ee4a-23d0-4db2-a45b-f53896ff09bc",
"relationship--b0f7da8d-eaa3-4149-94cd-0d84661e70a4",
"relationship--3d792ec1-f65a-4808-be6f-12876a0169d1",
"relationship--3a26de54-1563-4825-b0db-b9c84812802c",
"relationship--fe767b18-e2c8-42d6-8ac9-488060c32774",
"relationship--840203dd-c576-4b3a-982b-752bb0c975b1",
"relationship--82ea5de1-17f1-4478-83d5-c2e25cadab72",
"relationship--2ea0aba6-226c-4baa-b9bc-590f3d357832",
"relationship--34ed5b38-09af-4fe4-8b5c-801b1e4df2da",
"relationship--d27f36e6-3632-404c-9f8a-0eac30c8b3f5",
"relationship--b7a9d473-0b3b-4010-bd50-cd444cc6f2f8",
"relationship--5f7cf9fe-fc85-4903-a691-02fee7b8eff9",
"relationship--c583e94e-322f-472d-9fef-d9abc8575337",
"relationship--c51fa13a-b4b4-4368-be38-e7511db76a5f",
"relationship--0ead6069-19eb-4cb3-8bd0-d21b826cad2c",
"relationship--52c6ab7d-f88a-47a6-83e7-c5e466e0e454",
"relationship--b9d7adb5-8a26-4dca-9dd0-d4031214dc6c",
"relationship--73294e3c-7704-4692-b145-fda7b8d90e1f",
"relationship--ab9374f9-51a7-4e5c-8ad5-c435067f5e41",
"relationship--66ff3516-527a-487f-828a-d8abeed6fe8e",
"relationship--dc405231-fdb5-4f6c-b8a5-5ffde4f05a1d",
"relationship--be215c8e-1da9-4097-a47d-034634d28283",
"relationship--a1902b34-b90c-468c-9e10-fae639cacb4f",
"domain-name--94ecf52a-c09b-4a02-af02-14957f47222a",
"domain-name--83bac78f-d8fd-4d66-9a15-da947d8c2f97",
"domain-name--e9b5aad8-2f97-443a-a61d-f416de0ea536",
"domain-name--1baac521-1655-4979-b6a7-f2668a4c4815",
"domain-name--737a57ca-f62e-47a8-858c-09b7370cb418",
"domain-name--d6dcd9f4-1b6e-476c-b121-0bc46b7ee0f9",
"domain-name--25302384-d25b-4349-af40-5ffc0fdbe987",
"domain-name--43d4e15b-eecc-4429-bd56-b43a0b104fd6",
"file:hashes.SHA-256--7f631346-20ad-41bf-b533-049e32318ccd",
"file:hashes.SHA-256--554c402c-a5e8-4734-90a0-e10c70b0ce14",
"file:hashes.SHA-256--e039dfa2-e2f1-4568-9b68-18263ab587d1",
"file:hashes.SHA-256--c2c87fa6-f972-4143-a8f1-106aedab03c2",
"file:hashes.SHA-256--ac1b98ea-6662-42d4-970a-c996d6364d31",
"file:hashes.SHA-256--77bb5e28-ee1b-40d4-91c4-2901e871d730",
"file:hashes.SHA-256--ad934b28-5c90-4441-a489-bc7700224d1f",
"file:hashes.SHA-256--ab2b7f21-0048-464e-b7e2-debe13eda22b",
"file:hashes.SHA-256--a396325b-3d7e-4d2e-904a-65fc750b7506",
"file:hashes.SHA-256--3299de4b-d171-4d85-8a50-a0a98620dcc6",
"file:hashes.SHA-256--8d932096-10ad-4bec-b4fc-1f837acefd9a",
"file:hashes.SHA-256--015289bd-9f4e-4b06-aed0-32b352df407d",
"file:hashes.SHA-256--6cc5fafc-8c72-495e-ae60-664eb2f8962a",
"file:hashes.SHA-256--520c4de7-cc12-4c12-bd5d-d781e0c71a74",
"file:hashes.SHA-256--add58230-5eee-412d-b17f-05ef4c577da8",
"file:hashes.SHA-256--53ef3070-a12d-4dfd-b5a3-7be6a2e8540b",
"file:hashes.SHA-256--9e5508b3-85c9-4a59-8f8b-063fa132e5b7",
"file:hashes.SHA-256--4752a33d-4094-46fb-8961-75fa0c07def9",
"file:hashes.SHA-256--2fef9525-d0b6-4e63-9ee2-a2b0fd4597a3",
"indicator--c9411cf8-1a1a-48b1-a58a-caeb69ce8f06",
"relationship--990fe464-ef43-46ac-9f96-987756849c00",
"indicator--225cd3f8-f681-461a-aef5-08e103d06aa9",
"relationship--33514c2c-5667-4ffb-a86b-02c43d0fc1e1",
"indicator--824f539d-0018-46f3-bbe3-c69bd287c583",
"relationship--bde47f86-2945-4d08-8d58-f4a303779dd1",
"indicator--fb487629-c4f2-40ed-8947-390e0adda4ee",
"relationship--6d60ac37-d0ff-4957-bbdb-98d441d69547",
"indicator--0217d210-72f0-4d34-a087-1bb26deb0f7e",
"relationship--24029e82-bb03-40a0-ba05-0b0c362e724d",
"indicator--18cffa35-be72-4f33-a814-9704be14b73c",
"relationship--f8fda82f-94ee-4a2c-a29e-f8928c3ddc65",
"indicator--2d003a23-89ef-40d1-92a7-830a7318e2f6",
"relationship--7712e5ad-eb1a-47d8-9d3f-f0b596f95393",
"indicator--80a77a58-29e2-456b-b220-20babd778328",
"relationship--f54f4117-8268-417f-bf1d-424284334c9c"
],
"labels": [
"threat-report",
"threat-intelligence"
],
"created_by_ref": "identity--514347c8-67f5-4a12-bc21-93cd97e1aee6",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.564Z",
"modified": "2025-12-19T10:27:47.591Z",
"confidence": 95,
"type": "vulnerability",
"id": "vulnerability--4b1b7578-644c-4cee-b209-befc0c385a80",
"name": "CVE-2025-20393",
"description": "Cisco is aware of a potential vulnerability. Cisco is currently investigating and will update these details as appropriate as more information becomes available.. CVSS Score: 10.0 (CRITICAL). CISA KEV: Active exploitation confirmed. EPSS: 4.0% exploitation probability",
"x_cvss_score": 10.0,
"x_cvss_severity": "CRITICAL",
"x_kev_status": true,
"x_epss_score": 0.04033,
"external_references": [
{
"source_name": "cve",
"external_id": "CVE-2025-20393",
"url": "https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2025-20393"
},
{
"source_name": "nvd",
"external_id": "CVE-2025-20393",
"url": "https://nvd.nist.gov/vuln/detail/CVE-2025-20393"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"vulnerability"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.592Z",
"modified": "2025-12-19T10:27:47.592Z",
"confidence": 95,
"type": "vulnerability",
"id": "vulnerability--773c21cf-7a9e-4746-b0ab-233a26535983",
"name": "CVE-2025-37164",
"description": "A remote code execution issue exists in HPE OneView.. CVSS Score: 10.0 (CRITICAL). EPSS: 0.3% exploitation probability",
"x_cvss_score": 10.0,
"x_cvss_severity": "CRITICAL",
"x_kev_status": false,
"x_epss_score": 0.00253,
"external_references": [
{
"source_name": "cve",
"external_id": "CVE-2025-37164",
"url": "https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2025-37164"
},
{
"source_name": "nvd",
"external_id": "CVE-2025-37164",
"url": "https://nvd.nist.gov/vuln/detail/CVE-2025-37164"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"vulnerability"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.592Z",
"modified": "2025-12-19T10:27:47.592Z",
"confidence": 95,
"type": "identity",
"id": "identity--6741006f-839c-40a5-9d6e-5c3499671c57",
"name": "Cisco",
"identity_class": "organization",
"labels": [
"identity"
],
"description": "Cisco is a multinational technology conglomerate that specializes in networking hardware, software, telecommunications equipment, and other high-technology services and products. Cisco is known for its extensive range of products, including routers, switches, and cybersecurity solutions. Notably, Cisco has disclosed critical zero-day vulnerabilities, such as CVE-2025-20393, in its Secure Email Gateway and Secure Email/Web Manager, which have been actively exploited by threat actors.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.592Z",
"modified": "2025-12-19T10:27:47.592Z",
"confidence": 89,
"type": "identity",
"id": "identity--e26e77aa-e035-4161-896a-eaad198d10a2",
"name": "Cisco Secure Email Gateway",
"identity_class": "system",
"labels": [
"identity"
],
"description": "Cisco Secure Email Gateway is a specialized network security appliance designed by Cisco to filter and scan incoming and outgoing email traffic. It is engineered to detect and mitigate various security threats, including malware, spam, and phishing attempts. The system plays a crucial role in protecting enterprise email infrastructures by identifying and blocking malicious activities, ensuring secure communication channels within organizations.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.592Z",
"modified": "2025-12-19T10:27:47.592Z",
"confidence": 95,
"type": "identity",
"id": "identity--4554385d-4839-478d-9228-aec70dce023e",
"name": "Claude",
"identity_class": "system",
"labels": [
"identity"
],
"description": "Claude is an AI model developed by Anthropic. It was reported to have been jailbroken and tricked by Chinese hackers, highlighting the vulnerabilities of AI systems to cyber attacks. This incident underscores the need for robust security measures to protect AI technologies from malicious exploitation.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.592Z",
"modified": "2025-12-19T10:27:47.592Z",
"confidence": 95,
"type": "identity",
"id": "identity--d656b75c-7852-4c6e-b421-a822d7664ae7",
"name": "Hewlett Packard Enterprise",
"identity_class": "organization",
"labels": [
"identity"
],
"description": "Hewlett Packard Enterprise (HPE) is a multinational technology company that specializes in providing enterprise-level solutions, including servers, storage, networking, and software. HPE is known for its innovative products and services that cater to the needs of large organizations, helping them manage and secure their IT infrastructure. Notably, HPE has addressed critical vulnerabilities in its software, such as the OneView flaw (CVE-2025-37164), which could allow remote code execution, highlighting its commitment to cybersecurity.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.592Z",
"modified": "2025-12-19T10:27:47.592Z",
"confidence": 95,
"type": "identity",
"id": "identity--2f0057c3-d3b9-45b0-ba92-0b88105c0ccb",
"name": "OneView Software",
"identity_class": "software",
"labels": [
"identity"
],
"description": "OneView Software is a specific software platform developed by Hewlett Packard Enterprise (HPE) for managing and monitoring IT infrastructure. The vulnerability CVE-2025-37164, with a CVSS score of 10.0, was discovered in this software, highlighting the importance of securing such critical infrastructure management tools. As a target of a high-severity vulnerability, OneView Software is a relevant entity in the context of threat intelligence.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.592Z",
"modified": "2025-12-19T10:27:47.592Z",
"confidence": 95,
"type": "malware",
"id": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"name": "TruffleNet",
"is_family": true,
"malware_types": [
"trojan"
],
"labels": [
"malicious-activity"
],
"description": "TruffleNet is a malware campaign that has been documented by Fortinet, highlighting the risks of cloud attacks that don't rely on zero-day vulnerabilities. This campaign is notable for its ability to compromise cloud systems without exploiting previously unknown vulnerabilities, making it a significant concern for security leaders. The TruffleNet campaign demonstrates the evolving nature of cloud threats and the need for robust security measures to protect against such attacks.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.593Z",
"modified": "2025-12-19T10:27:47.593Z",
"confidence": 95,
"type": "identity",
"id": "identity--c4bddfde-bffe-4aa3-970b-dd430d1877f3",
"name": "Fortinet",
"identity_class": "organization",
"labels": [
"identity"
],
"description": "Fortinet is a prominent cybersecurity company that focuses on providing network security, threat protection, and network segmentation solutions. They are known for their research and documentation of cyber threats, such as the TruffleNet campaign, which highlights vulnerabilities in cloud security. Fortinet's solutions help organizations defend against a wide range of cyber threats by securing their digital infrastructure and automating threat responses.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.593Z",
"modified": "2025-12-19T10:27:47.593Z",
"confidence": 95,
"type": "identity",
"id": "identity--3e5eaf0a-42ab-4555-801b-e588368e21a2",
"name": "ServiceNow",
"identity_class": "organization",
"labels": [
"identity"
],
"description": "ServiceNow is a leading cloud-based platform provider specializing in IT service management, workflow automation, and cybersecurity solutions. The company helps organizations manage and respond to IT incidents and security threats, unifying application, network, and operational risk to enhance overall security posture.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.593Z",
"modified": "2025-12-19T10:27:47.593Z",
"confidence": 95,
"type": "identity",
"id": "identity--6e5f0b1c-6b68-4827-ac00-d36acd639e2b",
"name": "Hugging Face Transformers",
"identity_class": "organization",
"labels": [
"identity"
],
"description": "Hugging Face Transformers is a popular open-source machine learning library developed by Hugging Face, a company that provides a range of AI-powered tools and services. The library is widely used in natural language processing and other applications. As a target of a vulnerability, Hugging Face Transformers is a specific identity that is relevant to cybersecurity.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.593Z",
"modified": "2025-12-19T10:27:47.593Z",
"confidence": 95,
"type": "identity",
"id": "identity--1908b54a-478b-4cab-a870-6741a700fb2a",
"name": "ASRock",
"identity_class": "organization",
"labels": [
"identity"
],
"description": "ASRock is a Taiwanese computer hardware company that designs and manufactures computer motherboards, graphics cards, and other computer components. In this context, certain ASRock motherboard models are affected by a security vulnerability that leaves them susceptible to early-boot direct memory access (DMA) attacks. This vulnerability highlights the importance of securing firmware and UEFI implementations in computer hardware.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.594Z",
"modified": "2025-12-19T10:27:47.594Z",
"confidence": 95,
"type": "identity",
"id": "identity--afa5a316-655a-43a9-b3f1-2a1d39c0ac1a",
"name": "RegScale",
"identity_class": "organization",
"labels": [
"identity"
],
"description": "RegScale is a cybersecurity company that provides compliance and risk management solutions. They offer a platform for organizations to collect and organize compliance data based on the Open Security Controls Assessment Language (OSCAL) framework. RegScale's products aim to help companies streamline their compliance processes and improve their overall security posture.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.594Z",
"modified": "2025-12-19T10:27:47.594Z",
"confidence": 95,
"type": "identity",
"id": "identity--b0cec87f-da35-4d9b-b1e6-e530898b873e",
"name": "CentreStack",
"identity_class": "organization",
"labels": [
"identity"
],
"description": "CentreStack, also known as Gladinet CentreStack, is a cloud file sharing and synchronization solution developed by Gladinet Inc. It enables businesses to securely share files hosted on on-premises file servers through web browsers, mobile apps, and mapped drives. The platform has been targeted by the Clop ransomware gang in data theft extortion campaigns due to its internet-exposed file servers.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.594Z",
"modified": "2025-12-19T10:27:47.594Z",
"confidence": 95,
"type": "identity",
"id": "identity--689177a2-02f4-4be0-96a5-89b091102848",
"name": "DIG AI",
"identity_class": "system",
"labels": [
"identity"
],
"description": "DIG AI is a specific artificial intelligence tool reportedly used by malicious actors on the Tor network to enable scalable illicit activities. According to Resecurity, its usage surged in Q4 2025, posing new risks ahead of major 2026 events. DIG AI's capabilities and targets are not explicitly stated, but its involvement in malicious activities suggests it may be used for nefarious purposes such as automating attacks or enhancing stealth.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.594Z",
"modified": "2025-12-19T10:27:47.594Z",
"confidence": 95,
"type": "identity",
"id": "identity--3db79e9a-7407-4b26-a2c6-49e924dacb76",
"name": "Cloudflare, Inc.",
"identity_class": "organization",
"labels": [
"identity"
],
"description": "Cloudflare, Inc. is a prominent technology company specializing in providing web infrastructure and website security services. They offer content delivery network (CDN) services, DDoS mitigation, Internet security, and distributed domain name server services. Cloudflare, Inc. is known for its role in enhancing the performance and security of websites and online services, contributing to the broader cybersecurity ecosystem.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.594Z",
"modified": "2025-12-19T10:27:47.594Z",
"confidence": 95,
"type": "identity",
"id": "identity--96807dc1-31b6-428e-a217-2144d8041bee",
"name": "Senate Intelligence Committee",
"identity_class": "government",
"labels": [
"identity"
],
"description": "The United States Senate Intelligence Committee is a congressional committee responsible for overseeing the nation's intelligence agencies and addressing national security concerns. As a key player in shaping the country's cybersecurity policies, the committee's actions and recommendations have significant implications for the security of the nation's critical infrastructure and the protection of sensitive information.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.594Z",
"modified": "2025-12-19T10:27:47.594Z",
"confidence": 95,
"type": "identity",
"id": "identity--9602c33d-5759-40f1-83ac-74cf4aed6790",
"name": "KnowBe4",
"identity_class": "organization",
"labels": [
"identity"
],
"description": "KnowBe4 is a leading cybersecurity company specializing in security awareness training and simulated phishing attacks. The company aims to help organizations improve their security posture by educating employees about cyber threats and best practices. KnowBe4's platform is designed to create a more security-aware workforce, reducing the risk of successful phishing and ransomware attacks.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.594Z",
"modified": "2025-12-19T10:27:47.594Z",
"confidence": 95,
"type": "identity",
"id": "identity--9fd3cdf1-bb5e-4d25-9ca9-6737a061ca7d",
"name": "Bain Capital Ventures",
"identity_class": "organization",
"labels": [
"identity"
],
"description": "Bain Capital Ventures is a private investment firm that provides funding to various companies, including those in the cybersecurity space. In this context, they are leading a Series B funding round for Adaptive Security, a company focused on AI-driven voice and video threat detection. As a key player in the funding of a cybersecurity company, Bain Capital Ventures is a relevant entity in the cybersecurity ecosystem.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.594Z",
"modified": "2025-12-19T10:27:47.594Z",
"confidence": 95,
"type": "threat-actor",
"id": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"name": "APT28",
"threat_actor_types": [
"hacker"
],
"labels": [
"threat-actor"
],
"description": "APT28 is a sophisticated threat actor group attributed to Russian military intelligence, known for conducting cyberespionage operations against various targets, including government, defense, and civilian networks. APT28 has been linked to several high-profile attacks and is considered a persistent threat to global cybersecurity. Their tactics, techniques, and procedures (TTPs) include credential harvesting, phishing, and exploitation of vulnerabilities to gain unauthorized access to sensitive information.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.594Z",
"modified": "2025-12-19T10:27:47.594Z",
"confidence": 95,
"type": "vulnerability",
"id": "vulnerability--be8b8bda-4bd8-477b-9f78-f01bd36be940",
"name": "mfsa2025",
"description": "MFSA2025 is a security advisory issued by the Mozilla Foundation, detailing vulnerabilities in their products. This advisory provides information on the vulnerabilities, their impact, and the necessary patches or updates to remediate them. As a specific vulnerability identifier, MFSA2025 is a critical piece of information for cybersecurity professionals to understand and address potential security risks in Mozilla products.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"vulnerability"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.594Z",
"modified": "2025-12-19T10:27:47.594Z",
"confidence": 95,
"type": "malware",
"id": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"name": "Clop ransomware",
"is_family": true,
"malware_types": [
"ransomware"
],
"labels": [
"malicious-activity"
],
"description": "Clop ransomware, also known as Cl0p, is a specific ransomware family that targets Internet-exposed file servers, such as Gladinet CentreStack, in data theft extortion campaigns. This malware is designed to encrypt files and demand payment for decryption, posing a significant threat to organizations with vulnerable systems. Clop ransomware is notable for its targeted attacks on unpatched servers, highlighting the importance of regular security updates and robust defenses against ransomware threats.",
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.594Z",
"modified": "2025-12-19T10:27:47.594Z",
"confidence": 90,
"type": "attack-pattern",
"id": "attack-pattern--c99b8707-1226-4372-9f66-73b5d45b3f78",
"name": "Exploit Public-Facing Application",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "initial-access"
}
],
"x_mitre_id": "T1190",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1190/",
"external_id": "T1190"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.594Z",
"modified": "2025-12-19T10:27:47.594Z",
"confidence": 90,
"type": "attack-pattern",
"id": "attack-pattern--f826e543-c895-41dc-bac3-389ef1a14778",
"name": "Exploitation for Client Execution",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "execution"
}
],
"x_mitre_id": "T1203",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1203/",
"external_id": "T1203"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.595Z",
"modified": "2025-12-19T10:27:47.595Z",
"confidence": 90,
"type": "attack-pattern",
"id": "attack-pattern--d5f68c3e-3583-497a-8fd3-6fe32b38bf5f",
"name": "Command and Scripting Interpreter",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "execution"
}
],
"x_mitre_id": "T1059",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1059/",
"external_id": "T1059"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.595Z",
"modified": "2025-12-19T10:27:47.595Z",
"confidence": 90,
"type": "attack-pattern",
"id": "attack-pattern--f3417ce4-850c-4b35-a8f0-944ebd1397de",
"name": "Remote Services",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "lateral-movement"
}
],
"x_mitre_id": "T1021",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1021/",
"external_id": "T1021"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.595Z",
"modified": "2025-12-19T10:27:47.595Z",
"confidence": 90,
"type": "attack-pattern",
"id": "attack-pattern--cdc4c019-787f-457c-a963-e55f4e804db8",
"name": "Lateral Tool Transfer",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "lateral-movement"
}
],
"x_mitre_id": "T1570",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1570/",
"external_id": "T1570"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.595Z",
"modified": "2025-12-19T10:27:47.595Z",
"confidence": 90,
"type": "attack-pattern",
"id": "attack-pattern--57e97f43-4323-4cb3-892a-5387d593f466",
"name": "Obfuscated Files or Information",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "defense-evasion"
}
],
"x_mitre_id": "T1027",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1027/",
"external_id": "T1027"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.595Z",
"modified": "2025-12-19T10:27:47.595Z",
"confidence": 90,
"type": "attack-pattern",
"id": "attack-pattern--f25aeb02-492b-4d84-ba74-953779e3c255",
"name": "Adversary-in-the-Middle",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "credential-access"
},
{
"kill_chain_name": "mitre-attack",
"phase_name": "collection"
}
],
"x_mitre_id": "T1557",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1557/",
"external_id": "T1557"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.595Z",
"modified": "2025-12-19T10:27:47.595Z",
"confidence": 90,
"type": "attack-pattern",
"id": "attack-pattern--84b7fc1e-6f1b-4dc6-9bcc-488b2727c7af",
"name": "System Information Discovery",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "discovery"
}
],
"x_mitre_id": "T1082",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1082/",
"external_id": "T1082"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.595Z",
"modified": "2025-12-19T10:27:47.595Z",
"confidence": 90,
"type": "attack-pattern",
"id": "attack-pattern--aafb87d3-d5e3-44d3-9260-c41332dda176",
"name": "File and Directory Discovery",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "discovery"
}
],
"x_mitre_id": "T1083",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1083/",
"external_id": "T1083"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.595Z",
"modified": "2025-12-19T10:27:47.595Z",
"confidence": 90,
"type": "attack-pattern",
"id": "attack-pattern--6ffaba66-d6ac-4af3-b4f3-8a5adabce2bb",
"name": "Process Discovery",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "discovery"
}
],
"x_mitre_id": "T1057",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1057/",
"external_id": "T1057"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.595Z",
"modified": "2025-12-19T10:27:47.595Z",
"confidence": 90,
"type": "attack-pattern",
"id": "attack-pattern--34e7763c-ff57-4a68-9e1e-ebf4113d5699",
"name": "Supply Chain Compromise",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "initial-access"
}
],
"x_mitre_id": "T1195",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1195/",
"external_id": "T1195"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.595Z",
"modified": "2025-12-19T10:27:47.595Z",
"confidence": 85,
"type": "attack-pattern",
"id": "attack-pattern--d9b3d85d-2506-4f4c-acd0-adf1dd675840",
"name": "Distributed Component Object Model",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "lateral-movement"
}
],
"x_mitre_id": "T1021.003",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1021/003/",
"external_id": "T1021.003"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.595Z",
"modified": "2025-12-19T10:27:47.595Z",
"confidence": 85,
"type": "attack-pattern",
"id": "attack-pattern--450c59da-4f5c-4b1e-9e76-08ee62cb4061",
"name": "Service Exhaustion Flood",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "impact"
}
],
"x_mitre_id": "T1499.002",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1499/002/",
"external_id": "T1499.002"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.595Z",
"modified": "2025-12-19T10:27:47.595Z",
"confidence": 85,
"type": "attack-pattern",
"id": "attack-pattern--4e848890-246a-47e8-8d6b-1f4ce8315437",
"name": "System Firmware",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "persistence"
},
{
"kill_chain_name": "mitre-attack",
"phase_name": "defense-evasion"
}
],
"x_mitre_id": "T1542.001",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1542/001/",
"external_id": "T1542.001"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.595Z",
"modified": "2025-12-19T10:27:47.595Z",
"confidence": 85,
"type": "attack-pattern",
"id": "attack-pattern--80cfb71e-1a21-4f1f-9daa-0992a988e675",
"name": "Multi-Factor Authentication",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "credential-access"
},
{
"kill_chain_name": "mitre-attack",
"phase_name": "defense-evasion"
},
{
"kill_chain_name": "mitre-attack",
"phase_name": "persistence"
}
],
"x_mitre_id": "T1556.006",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1556/006/",
"external_id": "T1556.006"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.595Z",
"modified": "2025-12-19T10:27:47.595Z",
"confidence": 85,
"type": "attack-pattern",
"id": "attack-pattern--b059beaa-ec1b-4493-a498-29e7a2c111ef",
"name": "Multi-Factor Authentication Interception",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "credential-access"
}
],
"x_mitre_id": "T1111",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1111/",
"external_id": "T1111"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.595Z",
"modified": "2025-12-19T10:27:47.595Z",
"confidence": 85,
"type": "attack-pattern",
"id": "attack-pattern--7f3ed782-2721-4672-8876-bb795e84c74b",
"name": "Video Capture",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "collection"
}
],
"x_mitre_id": "T1125",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1125/",
"external_id": "T1125"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.595Z",
"modified": "2025-12-19T10:27:47.595Z",
"confidence": 77,
"type": "attack-pattern",
"id": "attack-pattern--7563a09a-2674-4a21-b6de-1d23c25c7eb4",
"name": "Cloud Secrets Management Stores",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "credential-access"
}
],
"x_mitre_id": "T1555.006",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1555/006/",
"external_id": "T1555.006"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.595Z",
"modified": "2025-12-19T10:27:47.595Z",
"confidence": 77,
"type": "attack-pattern",
"id": "attack-pattern--9cf22a56-1e68-47e8-b38b-604b9e3f621d",
"name": "LSA Secrets",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "credential-access"
}
],
"x_mitre_id": "T1003.004",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1003/004/",
"external_id": "T1003.004"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.595Z",
"modified": "2025-12-19T10:27:47.595Z",
"confidence": 77,
"type": "attack-pattern",
"id": "attack-pattern--39e179f7-eb33-4dba-86f0-c13dbcbd2a1b",
"name": "Vulnerabilities",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "resource-development"
}
],
"x_mitre_id": "T1588.006",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1588/006/",
"external_id": "T1588.006"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.595Z",
"modified": "2025-12-19T10:27:47.595Z",
"confidence": 76,
"type": "attack-pattern",
"id": "attack-pattern--2cf44576-4806-4da1-a645-8f620e826a63",
"name": "Pre-OS Boot",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "defense-evasion"
},
{
"kill_chain_name": "mitre-attack",
"phase_name": "persistence"
}
],
"x_mitre_id": "T1542",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1542/",
"external_id": "T1542"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.595Z",
"modified": "2025-12-19T10:27:47.595Z",
"confidence": 75,
"type": "attack-pattern",
"id": "attack-pattern--bb74e4d5-41a8-45dd-9977-108624360a65",
"name": "BITS Jobs",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "defense-evasion"
},
{
"kill_chain_name": "mitre-attack",
"phase_name": "persistence"
}
],
"x_mitre_id": "T1197",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1197/",
"external_id": "T1197"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.595Z",
"modified": "2025-12-19T10:27:47.595Z",
"confidence": 74,
"type": "attack-pattern",
"id": "attack-pattern--67804b3c-dd58-400e-a7a3-438e4d228585",
"name": "Multi-Factor Authentication Request Generation",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "credential-access"
}
],
"x_mitre_id": "T1621",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1621/",
"external_id": "T1621"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.595Z",
"modified": "2025-12-19T10:27:47.595Z",
"confidence": 70,
"type": "attack-pattern",
"id": "attack-pattern--e57f3d8f-db5e-465c-9294-c7831e03227e",
"name": "Scheduled Task",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "execution"
},
{
"kill_chain_name": "mitre-attack",
"phase_name": "persistence"
},
{
"kill_chain_name": "mitre-attack",
"phase_name": "privilege-escalation"
}
],
"x_mitre_id": "T1053.005",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1053/005/",
"external_id": "T1053.005"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.595Z",
"modified": "2025-12-19T10:27:47.595Z",
"confidence": 70,
"type": "attack-pattern",
"id": "attack-pattern--5391a1ff-d556-4631-ba60-8905f720bf7f",
"name": "Socket Filters",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "defense-evasion"
},
{
"kill_chain_name": "mitre-attack",
"phase_name": "persistence"
},
{
"kill_chain_name": "mitre-attack",
"phase_name": "command-and-control"
}
],
"x_mitre_id": "T1205.002",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1205/002/",
"external_id": "T1205.002"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.595Z",
"modified": "2025-12-19T10:27:47.595Z",
"confidence": 70,
"type": "attack-pattern",
"id": "attack-pattern--66e614e6-1ec5-41d9-ba44-34ed358d91aa",
"name": "Boot or Logon Initialization Scripts",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "persistence"
},
{
"kill_chain_name": "mitre-attack",
"phase_name": "privilege-escalation"
}
],
"x_mitre_id": "T1037",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1037/",
"external_id": "T1037"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.595Z",
"modified": "2025-12-19T10:27:47.595Z",
"confidence": 70,
"type": "attack-pattern",
"id": "attack-pattern--cc16d880-ad7c-42bb-98e3-ec0ea5e864bf",
"name": "Archive via Utility",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "collection"
}
],
"x_mitre_id": "T1560.001",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1560/001/",
"external_id": "T1560.001"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.595Z",
"modified": "2025-12-19T10:27:47.595Z",
"confidence": 70,
"type": "attack-pattern",
"id": "attack-pattern--cc98d5fb-a57e-47af-845c-7805ee3a7946",
"name": "Screen Capture",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "collection"
}
],
"x_mitre_id": "T1113",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1113/",
"external_id": "T1113"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.595Z",
"modified": "2025-12-19T10:27:47.595Z",
"confidence": 67,
"type": "attack-pattern",
"id": "attack-pattern--e3cf9026-e2ba-4bf8-bc6d-505c9c3fb86f",
"name": "Bootkit",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "persistence"
},
{
"kill_chain_name": "mitre-attack",
"phase_name": "defense-evasion"
}
],
"x_mitre_id": "T1542.003",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1542/003/",
"external_id": "T1542.003"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.596Z",
"modified": "2025-12-19T10:27:47.596Z",
"confidence": 66,
"type": "attack-pattern",
"id": "attack-pattern--9bd06311-fea2-4b5d-afa9-bcd1a11bdf8e",
"name": "Protocol or Service Impersonation",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "command-and-control"
}
],
"x_mitre_id": "T1001.003",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1001/003/",
"external_id": "T1001.003"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"spec_version": "2.1",
"created": "2025-12-19T10:27:47.596Z",
"modified": "2025-12-19T10:27:47.596Z",
"confidence": 65,
"type": "attack-pattern",
"id": "attack-pattern--54547eb0-ddb8-487e-8cf8-2daf078ef6b8",
"name": "Artificial Intelligence",
"kill_chain_phases": [
{
"kill_chain_name": "mitre-attack",
"phase_name": "resource-development"
}
],
"x_mitre_id": "T1588.007",
"external_references": [
{
"source_name": "MITRE ATT&CK",
"url": "https://attack.mitre.org/techniques/T1588/007/",
"external_id": "T1588.007"
}
],
"object_marking_refs": [
"marking-definition--94868c89-83c2-464b-929b-a1a8aa3c8487"
],
"labels": [
"mitre-attack"
]
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--676e8af4-8080-4d57-90cb-9cac53f8ec1c",
"created": "2025-12-19T10:27:47.596Z",
"modified": "2025-12-19T10:27:47.596Z",
"relationship_type": "targets",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "identity--e26e77aa-e035-4161-896a-eaad198d10a2",
"confidence": 85,
"description": "Co-occurrence in intelligence context",
"x_validation_method": "three-llm-consensus"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--774e9ce1-32f1-498f-b68c-d2c4a27d7595",
"created": "2025-12-19T10:27:47.596Z",
"modified": "2025-12-19T10:27:47.596Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--c99b8707-1226-4372-9f66-73b5d45b3f78",
"confidence": 60,
"description": "Co-occurrence: APT28 and Exploit Public-Facing Application (T1190) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--ce19f56d-995f-400e-a2d0-244d7866f6be",
"created": "2025-12-19T10:27:47.596Z",
"modified": "2025-12-19T10:27:47.596Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--f826e543-c895-41dc-bac3-389ef1a14778",
"confidence": 60,
"description": "Co-occurrence: APT28 and Exploitation for Client Execution (T1203) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--14cbdf03-a2fc-44a8-a4c8-1aa8b6ea70bf",
"created": "2025-12-19T10:27:47.596Z",
"modified": "2025-12-19T10:27:47.596Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--d5f68c3e-3583-497a-8fd3-6fe32b38bf5f",
"confidence": 60,
"description": "Co-occurrence: APT28 and Command and Scripting Interpreter (T1059) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--b85642b3-68f8-4941-8694-60acc4b304be",
"created": "2025-12-19T10:27:47.596Z",
"modified": "2025-12-19T10:27:47.596Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--f3417ce4-850c-4b35-a8f0-944ebd1397de",
"confidence": 60,
"description": "Co-occurrence: APT28 and Remote Services (T1021) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--d4efe09a-5c53-4415-9372-56027a45bf00",
"created": "2025-12-19T10:27:47.596Z",
"modified": "2025-12-19T10:27:47.596Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--cdc4c019-787f-457c-a963-e55f4e804db8",
"confidence": 60,
"description": "Co-occurrence: APT28 and Lateral Tool Transfer (T1570) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--f2b9c318-e962-40f8-8245-86bd5e486f77",
"created": "2025-12-19T10:27:47.596Z",
"modified": "2025-12-19T10:27:47.596Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--57e97f43-4323-4cb3-892a-5387d593f466",
"confidence": 60,
"description": "Co-occurrence: APT28 and Obfuscated Files or Information (T1027) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--d6e06e73-36ca-475e-9d6d-24e9c5109a58",
"created": "2025-12-19T10:27:47.596Z",
"modified": "2025-12-19T10:27:47.596Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--f25aeb02-492b-4d84-ba74-953779e3c255",
"confidence": 60,
"description": "Co-occurrence: APT28 and Adversary-in-the-Middle (T1557) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--91a444ad-10a5-4711-be52-cb37c3bce6dd",
"created": "2025-12-19T10:27:47.596Z",
"modified": "2025-12-19T10:27:47.596Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--84b7fc1e-6f1b-4dc6-9bcc-488b2727c7af",
"confidence": 60,
"description": "Co-occurrence: APT28 and System Information Discovery (T1082) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--e9f09f9c-7af3-4e81-8767-1310ad585d38",
"created": "2025-12-19T10:27:47.596Z",
"modified": "2025-12-19T10:27:47.596Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--aafb87d3-d5e3-44d3-9260-c41332dda176",
"confidence": 60,
"description": "Co-occurrence: APT28 and File and Directory Discovery (T1083) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--d1720a0c-e6fd-4a58-8abc-65387de9a205",
"created": "2025-12-19T10:27:47.596Z",
"modified": "2025-12-19T10:27:47.596Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--6ffaba66-d6ac-4af3-b4f3-8a5adabce2bb",
"confidence": 60,
"description": "Co-occurrence: APT28 and Process Discovery (T1057) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--50cbac6a-0dd2-4639-8e87-9c496c2f30fc",
"created": "2025-12-19T10:27:47.596Z",
"modified": "2025-12-19T10:27:47.596Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--34e7763c-ff57-4a68-9e1e-ebf4113d5699",
"confidence": 60,
"description": "Co-occurrence: APT28 and Supply Chain Compromise (T1195) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--593c272a-2067-4077-afd4-4b43f56027a0",
"created": "2025-12-19T10:27:47.596Z",
"modified": "2025-12-19T10:27:47.596Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--d9b3d85d-2506-4f4c-acd0-adf1dd675840",
"confidence": 60,
"description": "Co-occurrence: APT28 and Distributed Component Object Model (T1021.003) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--465304f6-8d8a-475d-a889-0017d60881ed",
"created": "2025-12-19T10:27:47.596Z",
"modified": "2025-12-19T10:27:47.596Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--450c59da-4f5c-4b1e-9e76-08ee62cb4061",
"confidence": 60,
"description": "Co-occurrence: APT28 and Service Exhaustion Flood (T1499.002) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--911cd783-4827-48b7-9381-5102a9a4342b",
"created": "2025-12-19T10:27:47.596Z",
"modified": "2025-12-19T10:27:47.596Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--4e848890-246a-47e8-8d6b-1f4ce8315437",
"confidence": 60,
"description": "Co-occurrence: APT28 and System Firmware (T1542.001) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--9303f511-cf62-4af4-8000-425182c3c1d8",
"created": "2025-12-19T10:27:47.596Z",
"modified": "2025-12-19T10:27:47.596Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--80cfb71e-1a21-4f1f-9daa-0992a988e675",
"confidence": 60,
"description": "Co-occurrence: APT28 and Multi-Factor Authentication (T1556.006) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--dd0a17bf-21a2-4153-a801-eee070a05011",
"created": "2025-12-19T10:27:47.596Z",
"modified": "2025-12-19T10:27:47.596Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--b059beaa-ec1b-4493-a498-29e7a2c111ef",
"confidence": 60,
"description": "Co-occurrence: APT28 and Multi-Factor Authentication Interception (T1111) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--e7507dd9-731e-45da-ab15-881c5462677a",
"created": "2025-12-19T10:27:47.596Z",
"modified": "2025-12-19T10:27:47.596Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--7f3ed782-2721-4672-8876-bb795e84c74b",
"confidence": 60,
"description": "Co-occurrence: APT28 and Video Capture (T1125) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--07a5807e-f8ce-41e6-aca0-b8103c0230e4",
"created": "2025-12-19T10:27:47.596Z",
"modified": "2025-12-19T10:27:47.596Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--7563a09a-2674-4a21-b6de-1d23c25c7eb4",
"confidence": 60,
"description": "Co-occurrence: APT28 and Cloud Secrets Management Stores (T1555.006) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--5f80552d-9dbc-4264-b734-87087fa1d7bc",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--9cf22a56-1e68-47e8-b38b-604b9e3f621d",
"confidence": 60,
"description": "Co-occurrence: APT28 and LSA Secrets (T1003.004) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--c77ea9d5-5824-47af-897a-dddb73a3bd0d",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--39e179f7-eb33-4dba-86f0-c13dbcbd2a1b",
"confidence": 60,
"description": "Co-occurrence: APT28 and Vulnerabilities (T1588.006) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--2495c46a-24e6-436e-ba3a-2c51ee78eacd",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--2cf44576-4806-4da1-a645-8f620e826a63",
"confidence": 60,
"description": "Co-occurrence: APT28 and Pre-OS Boot (T1542) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--2d552a7b-4871-41e2-bc6a-1144134d8c85",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--bb74e4d5-41a8-45dd-9977-108624360a65",
"confidence": 60,
"description": "Co-occurrence: APT28 and BITS Jobs (T1197) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--9b548df2-8004-4836-9ad6-73722591f690",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--67804b3c-dd58-400e-a7a3-438e4d228585",
"confidence": 60,
"description": "Co-occurrence: APT28 and Multi-Factor Authentication Request Generation (T1621) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--35c44c96-eb1b-4dec-bb03-811eaf6ef1d1",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--e57f3d8f-db5e-465c-9294-c7831e03227e",
"confidence": 60,
"description": "Co-occurrence: APT28 and Scheduled Task (T1053.005) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--4760d102-1dc2-4dd3-9693-b5c5206b9ce2",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--5391a1ff-d556-4631-ba60-8905f720bf7f",
"confidence": 60,
"description": "Co-occurrence: APT28 and Socket Filters (T1205.002) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--168e9032-3524-4092-9d94-1bf1ece1a6eb",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--66e614e6-1ec5-41d9-ba44-34ed358d91aa",
"confidence": 60,
"description": "Co-occurrence: APT28 and Boot or Logon Initialization Scripts (T1037) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--f91bf561-92bf-48ab-b3f4-9729615aa938",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--cc16d880-ad7c-42bb-98e3-ec0ea5e864bf",
"confidence": 60,
"description": "Co-occurrence: APT28 and Archive via Utility (T1560.001) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--41dea06e-2c4f-44c0-ac0f-3f0c848494b8",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--cc98d5fb-a57e-47af-845c-7805ee3a7946",
"confidence": 60,
"description": "Co-occurrence: APT28 and Screen Capture (T1113) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--babbb1e6-aef1-473c-b8a9-e8582a4a1a45",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--e3cf9026-e2ba-4bf8-bc6d-505c9c3fb86f",
"confidence": 60,
"description": "Co-occurrence: APT28 and Bootkit (T1542.003) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--141ac71b-fa93-48a4-b37e-f8d7df06709f",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--9bd06311-fea2-4b5d-afa9-bcd1a11bdf8e",
"confidence": 60,
"description": "Co-occurrence: APT28 and Protocol or Service Impersonation (T1001.003) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--1c9181cb-2cc4-47d5-996f-d26001ebc817",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "threat-actor--a4948aa2-fa1b-40cb-ad64-3bab783f6427",
"target_ref": "attack-pattern--54547eb0-ddb8-487e-8cf8-2daf078ef6b8",
"confidence": 60,
"description": "Co-occurrence: APT28 and Artificial Intelligence (T1588.007) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--d682a1ea-f8ec-4b4b-8e3c-9ab7903c7b56",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--c99b8707-1226-4372-9f66-73b5d45b3f78",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and Exploit Public-Facing Application (T1190) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--2c9366ee-8a0c-4bb5-a993-d9d649d0f6b2",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--f826e543-c895-41dc-bac3-389ef1a14778",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and Exploitation for Client Execution (T1203) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--ba1e62c4-88ab-4e95-8f4b-8d22bf71074a",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--d5f68c3e-3583-497a-8fd3-6fe32b38bf5f",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and Command and Scripting Interpreter (T1059) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--08b3ae91-8240-487d-8ac9-4600542be565",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--f3417ce4-850c-4b35-a8f0-944ebd1397de",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and Remote Services (T1021) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--c3f278b2-5720-4b3d-a314-aba92be50fe0",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--cdc4c019-787f-457c-a963-e55f4e804db8",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and Lateral Tool Transfer (T1570) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--0d4e0ea6-507c-4568-8cf3-cd2c3cf6e27f",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--57e97f43-4323-4cb3-892a-5387d593f466",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and Obfuscated Files or Information (T1027) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--4a91611f-4804-4ff5-804a-f10b61d12b6a",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--f25aeb02-492b-4d84-ba74-953779e3c255",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and Adversary-in-the-Middle (T1557) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--04f2b6c3-e705-4b43-8f1a-1cd75af68a7a",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--84b7fc1e-6f1b-4dc6-9bcc-488b2727c7af",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and System Information Discovery (T1082) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--6687d57f-02c8-4169-94fa-56ca651b2dac",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--aafb87d3-d5e3-44d3-9260-c41332dda176",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and File and Directory Discovery (T1083) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--89c8a385-eb03-4aa3-a902-1b60072bf6eb",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--6ffaba66-d6ac-4af3-b4f3-8a5adabce2bb",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and Process Discovery (T1057) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--89c55b03-0d7c-40b6-b290-9a3a19000183",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--34e7763c-ff57-4a68-9e1e-ebf4113d5699",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and Supply Chain Compromise (T1195) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--ebcb68c5-4005-4108-90a1-8073d3c59708",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--d9b3d85d-2506-4f4c-acd0-adf1dd675840",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and Distributed Component Object Model (T1021.003) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--66ec9ffa-a19b-4314-88e8-82766cb18afb",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--450c59da-4f5c-4b1e-9e76-08ee62cb4061",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and Service Exhaustion Flood (T1499.002) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--33e7b161-6b15-44d0-8aad-aee549a3c704",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--4e848890-246a-47e8-8d6b-1f4ce8315437",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and System Firmware (T1542.001) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--5e81cebd-17d8-4d1d-be5b-2c3d72df884a",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--80cfb71e-1a21-4f1f-9daa-0992a988e675",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and Multi-Factor Authentication (T1556.006) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--7bb43b14-09f4-4166-9039-0bff85fb1f58",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--b059beaa-ec1b-4493-a498-29e7a2c111ef",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and Multi-Factor Authentication Interception (T1111) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--9b8563b7-e377-4cf2-a207-041e51ec8745",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--7f3ed782-2721-4672-8876-bb795e84c74b",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and Video Capture (T1125) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--e0057df3-4946-424c-8cfa-b69430bb05dc",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--7563a09a-2674-4a21-b6de-1d23c25c7eb4",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and Cloud Secrets Management Stores (T1555.006) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--baef7748-2f12-4e6b-a4ff-4b4600a41087",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--9cf22a56-1e68-47e8-b38b-604b9e3f621d",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and LSA Secrets (T1003.004) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--4d5f217d-fb1c-4e36-a817-60d03a78fa77",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--39e179f7-eb33-4dba-86f0-c13dbcbd2a1b",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and Vulnerabilities (T1588.006) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--9a8723a8-aa68-45ab-9556-0a3f2b34e0d3",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--2cf44576-4806-4da1-a645-8f620e826a63",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and Pre-OS Boot (T1542) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--728864aa-d9a2-4d5f-9a3b-62137608d1a1",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--bb74e4d5-41a8-45dd-9977-108624360a65",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and BITS Jobs (T1197) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--970eed47-10f6-4410-ae8d-de8a3ed279ab",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--67804b3c-dd58-400e-a7a3-438e4d228585",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and Multi-Factor Authentication Request Generation (T1621) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--f47714ce-96b4-437a-b41e-e3054265a27d",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--e57f3d8f-db5e-465c-9294-c7831e03227e",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and Scheduled Task (T1053.005) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--5ebf5b67-8da3-4bd9-85cc-3232a6f87e57",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--5391a1ff-d556-4631-ba60-8905f720bf7f",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and Socket Filters (T1205.002) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--7bf80cd1-b744-470f-be58-5f635256a95a",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--66e614e6-1ec5-41d9-ba44-34ed358d91aa",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and Boot or Logon Initialization Scripts (T1037) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--bd8f20ad-679a-42b1-aa39-657d9fd145a3",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--cc16d880-ad7c-42bb-98e3-ec0ea5e864bf",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and Archive via Utility (T1560.001) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--d9a3eeaf-4c6d-4863-8068-39e5f078e235",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--cc98d5fb-a57e-47af-845c-7805ee3a7946",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and Screen Capture (T1113) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--c5ff5fcd-0128-4abb-b0e3-cd1e55934de6",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--e3cf9026-e2ba-4bf8-bc6d-505c9c3fb86f",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and Bootkit (T1542.003) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--5b8f0d31-be58-4e08-876f-6df47571c20a",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--9bd06311-fea2-4b5d-afa9-bcd1a11bdf8e",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and Protocol or Service Impersonation (T1001.003) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--db4f03ba-4373-40e1-9757-052fd1106fb8",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--0c0dc8ac-7ef1-4254-91f7-7e4000c4e628",
"target_ref": "attack-pattern--54547eb0-ddb8-487e-8cf8-2daf078ef6b8",
"confidence": 55,
"description": "Co-occurrence: TruffleNet and Artificial Intelligence (T1588.007) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--054456b5-13c9-4b30-9ca5-72c7d97ba9d2",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--c99b8707-1226-4372-9f66-73b5d45b3f78",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and Exploit Public-Facing Application (T1190) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--cbf3e059-77ea-44d6-83e4-3d69f641377e",
"created": "2025-12-19T10:27:47.597Z",
"modified": "2025-12-19T10:27:47.597Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--f826e543-c895-41dc-bac3-389ef1a14778",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and Exploitation for Client Execution (T1203) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--c67e3652-3faf-4fc2-b2eb-0d2ff298af5a",
"created": "2025-12-19T10:27:47.598Z",
"modified": "2025-12-19T10:27:47.598Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--d5f68c3e-3583-497a-8fd3-6fe32b38bf5f",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and Command and Scripting Interpreter (T1059) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--42e8cc3d-0a0d-4d80-a4d2-447f11f771eb",
"created": "2025-12-19T10:27:47.598Z",
"modified": "2025-12-19T10:27:47.598Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--f3417ce4-850c-4b35-a8f0-944ebd1397de",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and Remote Services (T1021) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--f43c6ed1-e549-493b-bfe6-023ba68ef673",
"created": "2025-12-19T10:27:47.598Z",
"modified": "2025-12-19T10:27:47.598Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--cdc4c019-787f-457c-a963-e55f4e804db8",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and Lateral Tool Transfer (T1570) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--7f8b275d-5399-46ea-b0d0-df26f7c4aed2",
"created": "2025-12-19T10:27:47.598Z",
"modified": "2025-12-19T10:27:47.598Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--57e97f43-4323-4cb3-892a-5387d593f466",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and Obfuscated Files or Information (T1027) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--613527f4-1ca3-420b-a2fe-7500d0e3ad1c",
"created": "2025-12-19T10:27:47.598Z",
"modified": "2025-12-19T10:27:47.598Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--f25aeb02-492b-4d84-ba74-953779e3c255",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and Adversary-in-the-Middle (T1557) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--8f950711-2d13-4698-b9b4-293f52aef4c3",
"created": "2025-12-19T10:27:47.598Z",
"modified": "2025-12-19T10:27:47.598Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--84b7fc1e-6f1b-4dc6-9bcc-488b2727c7af",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and System Information Discovery (T1082) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--41d3ee4a-23d0-4db2-a45b-f53896ff09bc",
"created": "2025-12-19T10:27:47.598Z",
"modified": "2025-12-19T10:27:47.598Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--aafb87d3-d5e3-44d3-9260-c41332dda176",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and File and Directory Discovery (T1083) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--b0f7da8d-eaa3-4149-94cd-0d84661e70a4",
"created": "2025-12-19T10:27:47.598Z",
"modified": "2025-12-19T10:27:47.598Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--6ffaba66-d6ac-4af3-b4f3-8a5adabce2bb",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and Process Discovery (T1057) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--3d792ec1-f65a-4808-be6f-12876a0169d1",
"created": "2025-12-19T10:27:47.598Z",
"modified": "2025-12-19T10:27:47.598Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--34e7763c-ff57-4a68-9e1e-ebf4113d5699",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and Supply Chain Compromise (T1195) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--3a26de54-1563-4825-b0db-b9c84812802c",
"created": "2025-12-19T10:27:47.598Z",
"modified": "2025-12-19T10:27:47.598Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--d9b3d85d-2506-4f4c-acd0-adf1dd675840",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and Distributed Component Object Model (T1021.003) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--fe767b18-e2c8-42d6-8ac9-488060c32774",
"created": "2025-12-19T10:27:47.598Z",
"modified": "2025-12-19T10:27:47.598Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--450c59da-4f5c-4b1e-9e76-08ee62cb4061",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and Service Exhaustion Flood (T1499.002) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--840203dd-c576-4b3a-982b-752bb0c975b1",
"created": "2025-12-19T10:27:47.598Z",
"modified": "2025-12-19T10:27:47.598Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--4e848890-246a-47e8-8d6b-1f4ce8315437",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and System Firmware (T1542.001) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--82ea5de1-17f1-4478-83d5-c2e25cadab72",
"created": "2025-12-19T10:27:47.598Z",
"modified": "2025-12-19T10:27:47.598Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--80cfb71e-1a21-4f1f-9daa-0992a988e675",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and Multi-Factor Authentication (T1556.006) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--2ea0aba6-226c-4baa-b9bc-590f3d357832",
"created": "2025-12-19T10:27:47.598Z",
"modified": "2025-12-19T10:27:47.598Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--b059beaa-ec1b-4493-a498-29e7a2c111ef",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and Multi-Factor Authentication Interception (T1111) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--34ed5b38-09af-4fe4-8b5c-801b1e4df2da",
"created": "2025-12-19T10:27:47.598Z",
"modified": "2025-12-19T10:27:47.598Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--7f3ed782-2721-4672-8876-bb795e84c74b",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and Video Capture (T1125) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--d27f36e6-3632-404c-9f8a-0eac30c8b3f5",
"created": "2025-12-19T10:27:47.598Z",
"modified": "2025-12-19T10:27:47.598Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--7563a09a-2674-4a21-b6de-1d23c25c7eb4",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and Cloud Secrets Management Stores (T1555.006) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--b7a9d473-0b3b-4010-bd50-cd444cc6f2f8",
"created": "2025-12-19T10:27:47.598Z",
"modified": "2025-12-19T10:27:47.598Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--9cf22a56-1e68-47e8-b38b-604b9e3f621d",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and LSA Secrets (T1003.004) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--5f7cf9fe-fc85-4903-a691-02fee7b8eff9",
"created": "2025-12-19T10:27:47.598Z",
"modified": "2025-12-19T10:27:47.598Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--39e179f7-eb33-4dba-86f0-c13dbcbd2a1b",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and Vulnerabilities (T1588.006) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--c583e94e-322f-472d-9fef-d9abc8575337",
"created": "2025-12-19T10:27:47.598Z",
"modified": "2025-12-19T10:27:47.598Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--2cf44576-4806-4da1-a645-8f620e826a63",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and Pre-OS Boot (T1542) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--c51fa13a-b4b4-4368-be38-e7511db76a5f",
"created": "2025-12-19T10:27:47.598Z",
"modified": "2025-12-19T10:27:47.598Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--bb74e4d5-41a8-45dd-9977-108624360a65",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and BITS Jobs (T1197) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--0ead6069-19eb-4cb3-8bd0-d21b826cad2c",
"created": "2025-12-19T10:27:47.598Z",
"modified": "2025-12-19T10:27:47.598Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--67804b3c-dd58-400e-a7a3-438e4d228585",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and Multi-Factor Authentication Request Generation (T1621) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--52c6ab7d-f88a-47a6-83e7-c5e466e0e454",
"created": "2025-12-19T10:27:47.598Z",
"modified": "2025-12-19T10:27:47.598Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--e57f3d8f-db5e-465c-9294-c7831e03227e",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and Scheduled Task (T1053.005) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--b9d7adb5-8a26-4dca-9dd0-d4031214dc6c",
"created": "2025-12-19T10:27:47.598Z",
"modified": "2025-12-19T10:27:47.598Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--5391a1ff-d556-4631-ba60-8905f720bf7f",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and Socket Filters (T1205.002) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--73294e3c-7704-4692-b145-fda7b8d90e1f",
"created": "2025-12-19T10:27:47.598Z",
"modified": "2025-12-19T10:27:47.598Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--66e614e6-1ec5-41d9-ba44-34ed358d91aa",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and Boot or Logon Initialization Scripts (T1037) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--ab9374f9-51a7-4e5c-8ad5-c435067f5e41",
"created": "2025-12-19T10:27:47.598Z",
"modified": "2025-12-19T10:27:47.598Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--cc16d880-ad7c-42bb-98e3-ec0ea5e864bf",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and Archive via Utility (T1560.001) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--66ff3516-527a-487f-828a-d8abeed6fe8e",
"created": "2025-12-19T10:27:47.598Z",
"modified": "2025-12-19T10:27:47.598Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--cc98d5fb-a57e-47af-845c-7805ee3a7946",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and Screen Capture (T1113) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--dc405231-fdb5-4f6c-b8a5-5ffde4f05a1d",
"created": "2025-12-19T10:27:47.598Z",
"modified": "2025-12-19T10:27:47.598Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--e3cf9026-e2ba-4bf8-bc6d-505c9c3fb86f",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and Bootkit (T1542.003) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--be215c8e-1da9-4097-a47d-034634d28283",
"created": "2025-12-19T10:27:47.598Z",
"modified": "2025-12-19T10:27:47.598Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--9bd06311-fea2-4b5d-afa9-bcd1a11bdf8e",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and Protocol or Service Impersonation (T1001.003) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--a1902b34-b90c-468c-9e10-fae639cacb4f",
"created": "2025-12-19T10:27:47.598Z",
"modified": "2025-12-19T10:27:47.598Z",
"relationship_type": "uses",
"source_ref": "malware--4953052e-2b86-40f0-9bf9-9a009a2e3a88",
"target_ref": "attack-pattern--54547eb0-ddb8-487e-8cf8-2daf078ef6b8",
"confidence": 55,
"description": "Co-occurrence: Clop ransomware and Artificial Intelligence (T1588.007) in same intelligence",
"x_validation_method": "mitre-cooccurrence"
},
{
"type": "domain-name",
"value": "cdnbenin.com",
"source": "OTX",
"malware_families": [
"TruffleNet"
],
"pulse_names": [
"Cloud Abuse at Scale"
],
"id": "domain-name--94ecf52a-c09b-4a02-af02-14957f47222a"
},
{
"type": "domain-name",
"value": "cfp-impactaction.com",
"source": "OTX",
"malware_families": [
"TruffleNet"
],
"pulse_names": [
"Cloud Abuse at Scale"
],
"id": "domain-name--83bac78f-d8fd-4d66-9a15-da947d8c2f97"
},
{
"type": "domain-name",
"value": "majoor.co",
"source": "OTX",
"malware_families": [
"TruffleNet"
],
"pulse_names": [
"Cloud Abuse at Scale"
],
"id": "domain-name--e9b5aad8-2f97-443a-a61d-f416de0ea536"
},
{
"type": "domain-name",
"value": "major.co",
"source": "OTX",
"malware_families": [
"TruffleNet"
],
"pulse_names": [
"Cloud Abuse at Scale"
],
"id": "domain-name--1baac521-1655-4979-b6a7-f2668a4c4815"
},
{
"type": "domain-name",
"value": "novainways.com",
"source": "OTX",
"malware_families": [
"TruffleNet"
],
"pulse_names": [
"Cloud Abuse at Scale"
],
"id": "domain-name--737a57ca-f62e-47a8-858c-09b7370cb418"
},
{
"type": "domain-name",
"value": "restaurantalhes.com",
"source": "OTX",
"malware_families": [
"TruffleNet"
],
"pulse_names": [
"Cloud Abuse at Scale"
],
"id": "domain-name--d6dcd9f4-1b6e-476c-b121-0bc46b7ee0f9"
},
{
"type": "domain-name",
"value": "zoominfopay.com",
"source": "OTX",
"malware_families": [
"TruffleNet"
],
"pulse_names": [
"Cloud Abuse at Scale"
],
"id": "domain-name--25302384-d25b-4349-af40-5ffc0fdbe987"
},
{
"type": "domain-name",
"value": "cndbenin.com",
"source": "OTX",
"malware_families": [
"TruffleNet"
],
"pulse_names": [
"TruffleNet BEC Campaign Exploits AWS SES with Stolen Credentials"
],
"id": "domain-name--43d4e15b-eecc-4429-bd56-b43a0b104fd6"
},
{
"type": "file:hashes.SHA-256",
"value": "408af0af7419f67d396f754f01d4757ea89355ad19f71942f8d44c0d5515eec8",
"source": "OTX",
"malware_families": [
"Clop ransomware"
],
"pulse_names": [
"Clop Ransomware"
],
"id": "file:hashes.SHA-256--7f631346-20ad-41bf-b533-049e32318ccd"
},
{
"type": "file:hashes.SHA-256",
"value": "7ada1228c791de703e2a51b1498bc955f14433f65d33342753fdb81bb35e5886",
"source": "OTX",
"malware_families": [
"Clop ransomware"
],
"pulse_names": [
"Clop Ransomware"
],
"id": "file:hashes.SHA-256--554c402c-a5e8-4734-90a0-e10c70b0ce14"
},
{
"type": "file:hashes.SHA-256",
"value": "102010727c6fbcd9da02d04ede1a8521ba2355d32da849226e96ef052c080b56",
"source": "OTX",
"malware_families": [
"Clop ransomware"
],
"pulse_names": [
"Clop Ransomware"
],
"id": "file:hashes.SHA-256--e039dfa2-e2f1-4568-9b68-18263ab587d1"
},
{
"type": "file:hashes.SHA-256",
"value": "2f29950640d024779134334cad79e2013871afa08c7be94356694db12ee437e2",
"source": "OTX",
"malware_families": [
"Clop ransomware"
],
"pulse_names": [
"Clop Ransomware"
],
"id": "file:hashes.SHA-256--c2c87fa6-f972-4143-a8f1-106aedab03c2"
},
{
"type": "file:hashes.SHA-256",
"value": "e48900dc697582db4655569bb844602ced3ad2b10b507223912048f1f3039ac6",
"source": "OTX",
"malware_families": [
"Clop ransomware"
],
"pulse_names": [
"Clop Ransomware"
],
"id": "file:hashes.SHA-256--ac1b98ea-6662-42d4-970a-c996d6364d31"
},
{
"type": "file:hashes.SHA-256",
"value": "3ee9b22827cb259f3d69ab974c632cefde71c61b4a9505cec06823076a2f898e",
"source": "OTX",
"malware_families": [
"Clop ransomware"
],
"pulse_names": [
"Clop Ransomware"
],
"id": "file:hashes.SHA-256--77bb5e28-ee1b-40d4-91c4-2901e871d730"
},
{
"type": "file:hashes.SHA-256",
"value": "d0cde86d47219e9c56b717f55dcdb01b0566344c13aa671613598cab427345b9",
"source": "OTX",
"malware_families": [
"Clop ransomware"
],
"pulse_names": [
"Clop Ransomware"
],
"id": "file:hashes.SHA-256--ad934b28-5c90-4441-a489-bc7700224d1f"
},
{
"type": "file:hashes.SHA-256",
"value": "929b7bf174638ff8cb158f4e00bc41ed69f1d2afd41ea3c9ee3b0c7dacdfa238",
"source": "OTX",
"malware_families": [
"Clop ransomware"
],
"pulse_names": [
"Clop Ransomware"
],
"id": "file:hashes.SHA-256--ab2b7f21-0048-464e-b7e2-debe13eda22b"
},
{
"type": "file:hashes.SHA-256",
"value": "31829479fa5b094ca3cfd0222e61295fff4821b778e5a7bd228b0c31f8a3cc44",
"source": "OTX",
"malware_families": [
"Clop ransomware"
],
"pulse_names": [
"Clop Ransomware"
],
"id": "file:hashes.SHA-256--a396325b-3d7e-4d2e-904a-65fc750b7506"
},
{
"type": "file:hashes.SHA-256",
"value": "cff818453138dcd8238f87b33a84e1bc1d560dea80c8d2412e1eb3f7242b27da",
"source": "OTX",
"malware_families": [
"Clop ransomware"
],
"pulse_names": [
"Clop Ransomware"
],
"id": "file:hashes.SHA-256--3299de4b-d171-4d85-8a50-a0a98620dcc6"
},
{
"type": "file:hashes.SHA-256",
"value": "bc59ff12f71e9c8234c5e335d48f308207f6accfad3e953f447e7de1504e57af",
"source": "OTX",
"malware_families": [
"Clop ransomware"
],
"pulse_names": [
"Clop Ransomware"
],
"id": "file:hashes.SHA-256--8d932096-10ad-4bec-b4fc-1f837acefd9a"
},
{
"type": "file:hashes.SHA-256",
"value": "35b0b54d13f50571239732421818c682fbe83075a4a961b20a7570610348aecc",
"source": "OTX",
"malware_families": [
"Clop ransomware"
],
"pulse_names": [
"Clop Ransomware"
],
"id": "file:hashes.SHA-256--015289bd-9f4e-4b06-aed0-32b352df407d"
},
{
"type": "file:hashes.SHA-256",
"value": "c150954e5fdfc100fbb74258cad6ef2595c239c105ff216b1d9a759c0104be04",
"source": "OTX",
"malware_families": [
"Clop ransomware"
],
"pulse_names": [
"Clop Ransomware"
],
"id": "file:hashes.SHA-256--6cc5fafc-8c72-495e-ae60-664eb2f8962a"
},
{
"type": "file:hashes.SHA-256",
"value": "7e91ff12d3f26982473c38a3ae99bfaf0b2966e85046ebed09709b6af797ef66",
"source": "OTX",
"malware_families": [
"Clop ransomware"
],
"pulse_names": [
"Clop Ransomware"
],
"id": "file:hashes.SHA-256--520c4de7-cc12-4c12-bd5d-d781e0c71a74"
},
{
"type": "file:hashes.SHA-256",
"value": "8e1bbe4cedeb7c334fe780ab3fb589fe30ed976153618ac3402a5edff1b17d64",
"source": "OTX",
"malware_families": [
"Clop ransomware"
],
"pulse_names": [
"Clop Ransomware"
],
"id": "file:hashes.SHA-256--add58230-5eee-412d-b17f-05ef4c577da8"
},
{
"type": "file:hashes.SHA-256",
"value": "0d19f60423cb2128555e831dc340152f9588c99f3e47d64f0bb4206a6213d579",
"source": "OTX",
"malware_families": [
"Clop ransomware"
],
"pulse_names": [
"Clop Ransomware"
],
"id": "file:hashes.SHA-256--53ef3070-a12d-4dfd-b5a3-7be6a2e8540b"
},
{
"type": "file:hashes.SHA-256",
"value": "e19d8919f4cb6c1ef8c7f3929d41e8a1a780132cb10f8b80698c8498028d16eb",
"source": "OTX",
"malware_families": [
"Clop ransomware"
],
"pulse_names": [
"Clop Ransomware"
],
"id": "file:hashes.SHA-256--9e5508b3-85c9-4a59-8f8b-063fa132e5b7"
},
{
"type": "file:hashes.SHA-256",
"value": "00e815ade8f3ad89a7726da8edd168df13f96ccb6c3daaf995aa9428bfb9ecf1",
"source": "OTX",
"malware_families": [
"Clop ransomware"
],
"pulse_names": [
"Clop Ransomware"
],
"id": "file:hashes.SHA-256--4752a33d-4094-46fb-8961-75fa0c07def9"
},
{
"type": "file:hashes.SHA-256",
"value": "6d115ae4c32d01a073185df95d3441d51065340ead1eada0efda6975214d1920",
"source": "OTX",
"malware_families": [
"Clop ransomware"
],
"pulse_names": [
"Clop Ransomware"
],
"id": "file:hashes.SHA-256--2fef9525-d0b6-4e63-9ee2-a2b0fd4597a3"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--c9411cf8-1a1a-48b1-a58a-caeb69ce8f06",
"created": "2025-12-19T10:25:21.664Z",
"modified": "2025-12-19T10:25:21.664Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'cdnbenin.com']",
"pattern_type": "stix",
"valid_from": "2025-12-19T10:25:21.665Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--990fe464-ef43-46ac-9f96-987756849c00",
"created": "2025-12-19T10:25:21.665Z",
"modified": "2025-12-19T10:25:21.665Z",
"relationship_type": "based-on",
"source_ref": "indicator--c9411cf8-1a1a-48b1-a58a-caeb69ce8f06",
"target_ref": "domain-name--94ecf52a-c09b-4a02-af02-14957f47222a"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--225cd3f8-f681-461a-aef5-08e103d06aa9",
"created": "2025-12-19T10:25:21.676Z",
"modified": "2025-12-19T10:25:21.676Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'cfp-impactaction.com']",
"pattern_type": "stix",
"valid_from": "2025-12-19T10:25:21.676Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--33514c2c-5667-4ffb-a86b-02c43d0fc1e1",
"created": "2025-12-19T10:25:21.676Z",
"modified": "2025-12-19T10:25:21.676Z",
"relationship_type": "based-on",
"source_ref": "indicator--225cd3f8-f681-461a-aef5-08e103d06aa9",
"target_ref": "domain-name--83bac78f-d8fd-4d66-9a15-da947d8c2f97"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--824f539d-0018-46f3-bbe3-c69bd287c583",
"created": "2025-12-19T10:25:21.685Z",
"modified": "2025-12-19T10:25:21.685Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'majoor.co']",
"pattern_type": "stix",
"valid_from": "2025-12-19T10:25:21.685Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--bde47f86-2945-4d08-8d58-f4a303779dd1",
"created": "2025-12-19T10:25:21.685Z",
"modified": "2025-12-19T10:25:21.685Z",
"relationship_type": "based-on",
"source_ref": "indicator--824f539d-0018-46f3-bbe3-c69bd287c583",
"target_ref": "domain-name--e9b5aad8-2f97-443a-a61d-f416de0ea536"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--fb487629-c4f2-40ed-8947-390e0adda4ee",
"created": "2025-12-19T10:25:21.696Z",
"modified": "2025-12-19T10:25:21.696Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'major.co']",
"pattern_type": "stix",
"valid_from": "2025-12-19T10:25:21.696Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--6d60ac37-d0ff-4957-bbdb-98d441d69547",
"created": "2025-12-19T10:25:21.696Z",
"modified": "2025-12-19T10:25:21.696Z",
"relationship_type": "based-on",
"source_ref": "indicator--fb487629-c4f2-40ed-8947-390e0adda4ee",
"target_ref": "domain-name--1baac521-1655-4979-b6a7-f2668a4c4815"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--0217d210-72f0-4d34-a087-1bb26deb0f7e",
"created": "2025-12-19T10:25:21.707Z",
"modified": "2025-12-19T10:25:21.707Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'novainways.com']",
"pattern_type": "stix",
"valid_from": "2025-12-19T10:25:21.707Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--24029e82-bb03-40a0-ba05-0b0c362e724d",
"created": "2025-12-19T10:25:21.707Z",
"modified": "2025-12-19T10:25:21.707Z",
"relationship_type": "based-on",
"source_ref": "indicator--0217d210-72f0-4d34-a087-1bb26deb0f7e",
"target_ref": "domain-name--737a57ca-f62e-47a8-858c-09b7370cb418"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--18cffa35-be72-4f33-a814-9704be14b73c",
"created": "2025-12-19T10:25:21.717Z",
"modified": "2025-12-19T10:25:21.717Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'restaurantalhes.com']",
"pattern_type": "stix",
"valid_from": "2025-12-19T10:25:21.717Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--f8fda82f-94ee-4a2c-a29e-f8928c3ddc65",
"created": "2025-12-19T10:25:21.717Z",
"modified": "2025-12-19T10:25:21.717Z",
"relationship_type": "based-on",
"source_ref": "indicator--18cffa35-be72-4f33-a814-9704be14b73c",
"target_ref": "domain-name--d6dcd9f4-1b6e-476c-b121-0bc46b7ee0f9"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--2d003a23-89ef-40d1-92a7-830a7318e2f6",
"created": "2025-12-19T10:25:21.726Z",
"modified": "2025-12-19T10:25:21.726Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'zoominfopay.com']",
"pattern_type": "stix",
"valid_from": "2025-12-19T10:25:21.726Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--7712e5ad-eb1a-47d8-9d3f-f0b596f95393",
"created": "2025-12-19T10:25:21.726Z",
"modified": "2025-12-19T10:25:21.726Z",
"relationship_type": "based-on",
"source_ref": "indicator--2d003a23-89ef-40d1-92a7-830a7318e2f6",
"target_ref": "domain-name--25302384-d25b-4349-af40-5ffc0fdbe987"
},
{
"type": "indicator",
"spec_version": "2.1",
"id": "indicator--80a77a58-29e2-456b-b220-20babd778328",
"created": "2025-12-19T10:25:21.735Z",
"modified": "2025-12-19T10:25:21.735Z",
"name": "Malicious domain-name indicator",
"description": "Malicious domain-name identified in threat intelligence",
"pattern": "[domain-name:value = 'cndbenin.com']",
"pattern_type": "stix",
"valid_from": "2025-12-19T10:25:21.735Z",
"labels": [
"malicious-activity"
],
"confidence": 70
},
{
"type": "relationship",
"spec_version": "2.1",
"id": "relationship--f54f4117-8268-417f-bf1d-424284334c9c",
"created": "2025-12-19T10:25:21.735Z",
"modified": "2025-12-19T10:25:21.735Z",
"relationship_type": "based-on",
"source_ref": "indicator--80a77a58-29e2-456b-b220-20babd778328",
"target_ref": "domain-name--43d4e15b-eecc-4429-bd56-b43a0b104fd6"
}
]
}